

TAMECAT is a sophisticated PowerShell-based backdoor linked to APT42, an Iranian state-sponsored hacking group.
It steals login credentials from Microsoft Edge and Chrome browsers while evading detection.
Security researchers from Israel’s National Digital Agency detailed its modular design in recent SpearSpecter campaign analysis.
APT42 deploys TAMECAT in long-term espionage operations against senior defense and government officials.
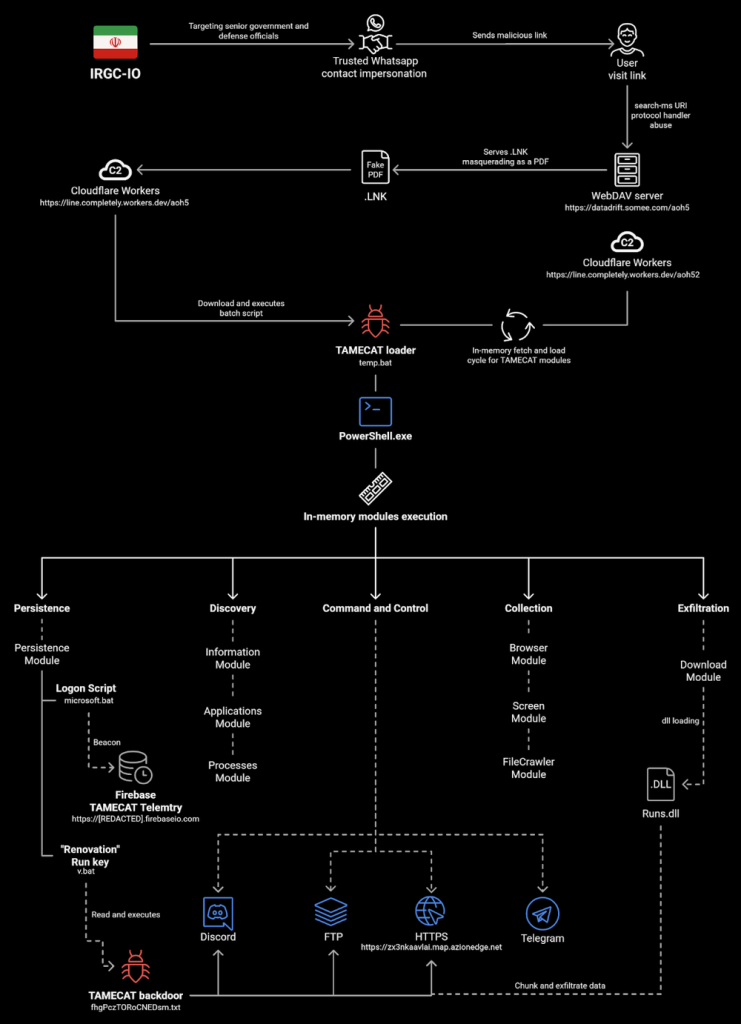
The group builds trust through social engineering before compromising systems. TAMECAT receives commands via Telegram bots, downloading extra scripts for tasks like screen captures and browser data theft, as reported by Pulsedive.
The infection chain starts with a VBScript downloader (SHA256: 5404e39f2f175a0fc993513ee52be3679a64c69c79e32caa656fbb7645965422). This script scans for antivirus products using WMI queries.
If “Windows” appears in the AV list, it launches PowerShell via conhost with wget to fetch the loader from tebi[.]io. Otherwise, it falls back to cmd.exe and curl for an alternate payload.
Loader Analysis
The loader, nconf.txt (SHA256: bd1f0fb085c486e97d82b6e8acb3977497c59c3ac79f973f96c395e7f0ca97f8), uses AES-encrypted payloads.
It defines Gorba for decryption with key “T2r0y1M1e1n1o0w1” and Borjol for further processing.
The script drops the first three bytes from a base64 URL, downloads df32s.txt, and applies bitwise operations plus UTF-8 conversion to reveal more code.
Decrypted modules handle victim ID generation (written to %LocalAppData%\config.txt) and C2 communication to accurate-sprout-porpoise[.]glitch[.]me.

It collects OS details, computer name, and a hardcoded token (GILNH9LX6TCZ9V8ZZSUF), encrypts via Borpos (AES-256, key: kNz0CXiP0wEQnhZXYbvraigXvRVYHk1B), and exfils via POST with custom “Content-DPR” header for the IV.

C2 responses, separated by ¶, include language (PowerShell/C#), base64 command, thread name, and start/stop flags.
TAMECAT executes these in-memory, suspending Chrome processes and using Edge’s remote debugging for credential extraction.
TAMECAT creates a Chrome directory in %LocalAppData% and targets saved logins. It leverages browser debugging protocols to dump credentials without disk writes.

Obfuscation includes array fragments, wildcards, and string replacement traits shared with PowerStar variants.
User-agent mimics Chrome 119: “Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36…”. Platforms like Discord supplement Telegram for C2 flexibility.
MITRE ATT&CK Mapping
- T1059.001: PowerShell execution.
- T1547: Boot/Logon Autostart (suspected persistence).
- T1555: Credentials from Password Stores (Edge/Chrome).
- T1071.001: Web Protocols (HTTPS C2).
- T1027: Obfuscated Files/Information.
Deploy EDR/AV to catch process chains like wscript spawning PowerShell. Enable PowerShell script-block logging and constrain execution policies to signed scripts only. Monitor VBScript launching interpreters and anomalous browser debugging.
TAMECAT evolves, but layered defenses limit its impact on high-value targets. Organizations should prioritize browser security and logging amid rising nation-state threats.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.





