
A new shellcode loader, dubbed “TriBack Loader,” to a China-nexus intrusion cluster tracked as JadeProx, with the malware explicitly engineered to evade modern EDR by abusing signed binaries and uncommon Win32 callback APIs.
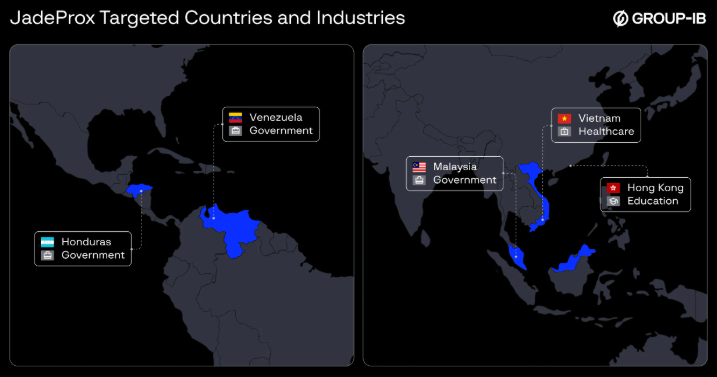
Across at least four observed variants, the loader underpins simultaneous espionage campaigns in South-East Asia and Latin America, including targeting of a Vietnamese public hospital, Malaysia’s Ministry of Foreign Affairs, Hong Kong education institutions, Honduras’ National Congress, and a Venezuelan municipal tax system.
The JadeProx cluster surfaced after operators accidentally exposed an Alibaba Cloud staging server with directory listing enabled, revealing bash history, post-exploitation toolkits, and paths to compromised victims in Vietnam, Malaysia, and Hong Kong.
In parallel, investigators tracked phishing activity aimed at Honduras’ National Congress via a decoy invoicing document, and a credential-harvesting portal impersonating a Venezuelan municipal tax administration portal in Bolívar state.
The campaign further extends into AI-themed lures, including fake Anthropic Claude software portals and Claude-Pro themed phishing sites used to disseminate TriBack Loader-based infection chains.
The loader implements a two-stage decryption routine byte-order reversal followed by a rolling XOR transform using hard-coded keys to reconstruct embedded shellcode in memory, closely mirroring patterns seen in other Chinese APT tooling.
To evade behavioral heuristics, each build dynamically rotates its choice of Win32 callback API and avoids the canonical VirtualAlloc–CreateThread sequence that EDR engines heavily profile.community.
In one variant recovered from the exposed directory, the decrypted payload is executed via InitOnceExecuteOnce. This rarely monitored one-time initialization callback allows shellcode to run without tripping common thread-creation hooks.
GroupIB Researchers said that, TriBack Loader is a custom shellcode loader distributed via DLL sideloading triads: a signed host executable, a malicious loader DLL, and an encrypted DAT or LOG payload embedded alongside.
Another variant observed in a Honduras-focused lure uses a TimerQueue timer callback, registering the shellcode as a deferred timer routine to bypass CreateThread-based telemetry collection.

A third variant, themed around Claude-Pro, resolves and invokes the undocumented EtwpCreateEtwThread function from ntdll to spawn a stealthy execution context, further complicating stack tracing and endpoint logging.
TriBack Loader Evades EDR
Two of the four TriBack Loader variants decrypted and executed AdaptixC2 beacons, an open-source post-exploitation framework previously adopted by actors such as Tropic Trooper.
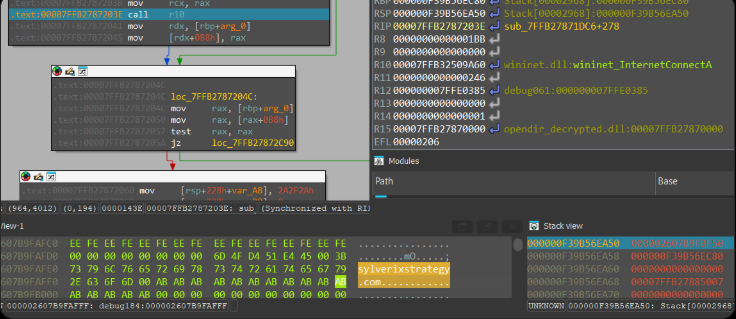
Group-IB analysts extracted full beacon configurations, revealing HTTP listener profiles, RC4 keys, and C2 endpoints including sylverixstrategy[.]com and gouvvbo[.]top, both registered via NameSilo and brought online within days of the payload compilation timestamps.
Notably, one configuration embedded a GitHub analytics cookie linking to a previously documented custom beacon profile associated with Chinese-aligned operators.
In the Claude-Pro themed chain, TriBack Loader does not deploy AdaptixC2; instead, decrypted shellcode corresponds to a Donut-based reflective loader that stages a previously undocumented backdoor, Beagle, on systems compromised via fake Claude-Pro MSI installers and ZIP archives.
his infrastructure pivots around license[.]claude-pro[.]com, hosted on Alibaba infrastructure and fronting a site impersonating a “Vertex Trust Advisors” financial entity, aligning with broader Chinese economic and intelligence interests in the targeted regions.
The exposed staging server hosted a full offensive toolkit spanning internal recon and cloud-evading persistence: iox and suo5 for SOCKS5 and HTTP-based tunneling, Neo-reGeorg for webshell pivoting, nuclei and fscan for vulnerability discovery.
A modified fuckaliyun.sh script to disable Alibaba Cloud security agents, and XMRig plus SOCKS5 proxies likely used during idle monetization phases.
Investigators also noted a garbled NPS intranet proxy, consistent with other Chinese-origin penetration frameworks, further supporting JadeProx’s China-nexus attribution.
All identified command-and-control domains including sylverixstrategy[.]com, gouvvbo[.]top, license[.]claude-pro[.]com, vertextrust-advisors[.]com, and security-themed update-* domains such as update-trellix[.]com and update-sentinelone[.]com.
The reuse of signed binaries from Microsoft, G DATA, and other trusted vendors for DLL sideloading reflects a long-running trend of certificate and signature abuse to bypass application control and EDR behavioral models.
Defenders should prioritize telemetry for unusual use of InitOnceExecuteOnce, TimerQueue timers, and EtwpCreateEtwThread in conjunction with in-memory decryption routines and reflective PE loading patterns, especially when invoked by signed binaries with atypical sidecar DLLs.
Organizations in government, healthcare, and education across SEA and LATAM should hunt for NameSilo-registered C2 domains noted above, scrutinize traffic to Cloudflare and Alibaba-hosted infrastructure, and monitor for AdaptixC2 and Donut-derived shellcode loaders as indicators of TriBack Loader activity.
IOCs
| Indicator | Type |
|---|---|
| 43.106.71[.]28:8000 | IP:Port |
| 8.217.190[.]58 | IP Address |
| sylverixstrategy[.]com | Domain |
| gouvvbo[.]top | Domain |
| license.claude-pro[.]com | Subdomain |
| vertextrust-advisors[.]com | Domain |
| update-trellix[.]com | Domain (Impersonation/Spoofing likely) |
| update-crowdstrike[.]com | Domain (Impersonation/Spoofing likely) |
| update-sentinelone[.]com | Domain (Impersonation/Spoofing likely) |
| dlrz-web.oss-cn-beijing.aliyuncs[.]com | Cloud Storage URL (Alibaba OSS) |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
What Features Should AI SOC Have in 2026? A Complete Checklist : Download the AI SOC Features Checklist


