

The ongoing supply chain attack targeting Aqua Security’s Trivy ecosystem has escalated, with new compromised Docker images discovered on Docker Hub.
According to Socket’s analysis, two new Docker image tags, 0.69.5 and 0.69.6, were published on March 22 without corresponding GitHub releases or version tags.
This discrepancy immediately raised concerns about unauthorized publishing activity. Both images have now been confirmed to contain indicators of compromise (IOCs) associated with the TeamPCP infostealer, a payload observed in earlier stages of the attack.
Security researchers at Socket have identified malicious artifacts tied to the same campaign that previously affected the aquasecurity/trivy-action GitHub repository, indicating a broader and more persistent intrusion.
Notably, the “latest” Docker tag currently points to version 0.69.6, meaning unsuspecting users pulling the default image may have inadvertently deployed compromised code into their environments.
Trivy Supply Chain Attack
Detailed binary analysis of the affected images revealed multiple known IOCs linked to the TeamPCP malware attack. Among the most prominent indicators is a typosquatted command-and-control (C2) domain, scan.aquasecurity.org, designed to mimic Aqua Security’s legitimate infrastructure.
Researchers also identified exfiltration-related artifacts, including files such as payload.enc and tpcp.tar.gz, suggesting active data harvesting capabilities.
Additionally, references to a fallback GitHub repository named tpcp-docs were embedded within the binaries, likely serving as a secondary channel for payload delivery or updates.
These findings confirm that the attack extends beyond simple code tampering, incorporating infrastructure designed for persistence and data exfiltration.
Further compounding concerns, security researcher Paul McCarty reported signs that the Aqua Security GitHub organization itself may have been exposed during the attack. Observations suggest that internal repositories could have been temporarily accessible, pointing to a deeper compromise of access controls.
While the full extent of this exposure remains unclear, the incident highlights the possibility that attackers gained elevated permissions, enabling them to manipulate both source code and distribution channels.
Current findings establish a clear timeline of compromised and safe releases. Version 0.69.3 remains the last verified clean release.
Version 0.69.4 was the first compromised version but has since been removed. The newly identified Docker images 0.69.5 and 0.69.6 are also confirmed to be malicious.
There is no evidence suggesting that versions prior to or including 0.69.3 were altered after publication. However, security experts caution that Docker tags are mutable, meaning previously trusted tags can be reassigned to malicious images without notice.
Mitigation and Response اقدامات
A search for “trivy” on Docker Hub reveals thousands of related images, including third-party builds and CI/CD integrations.
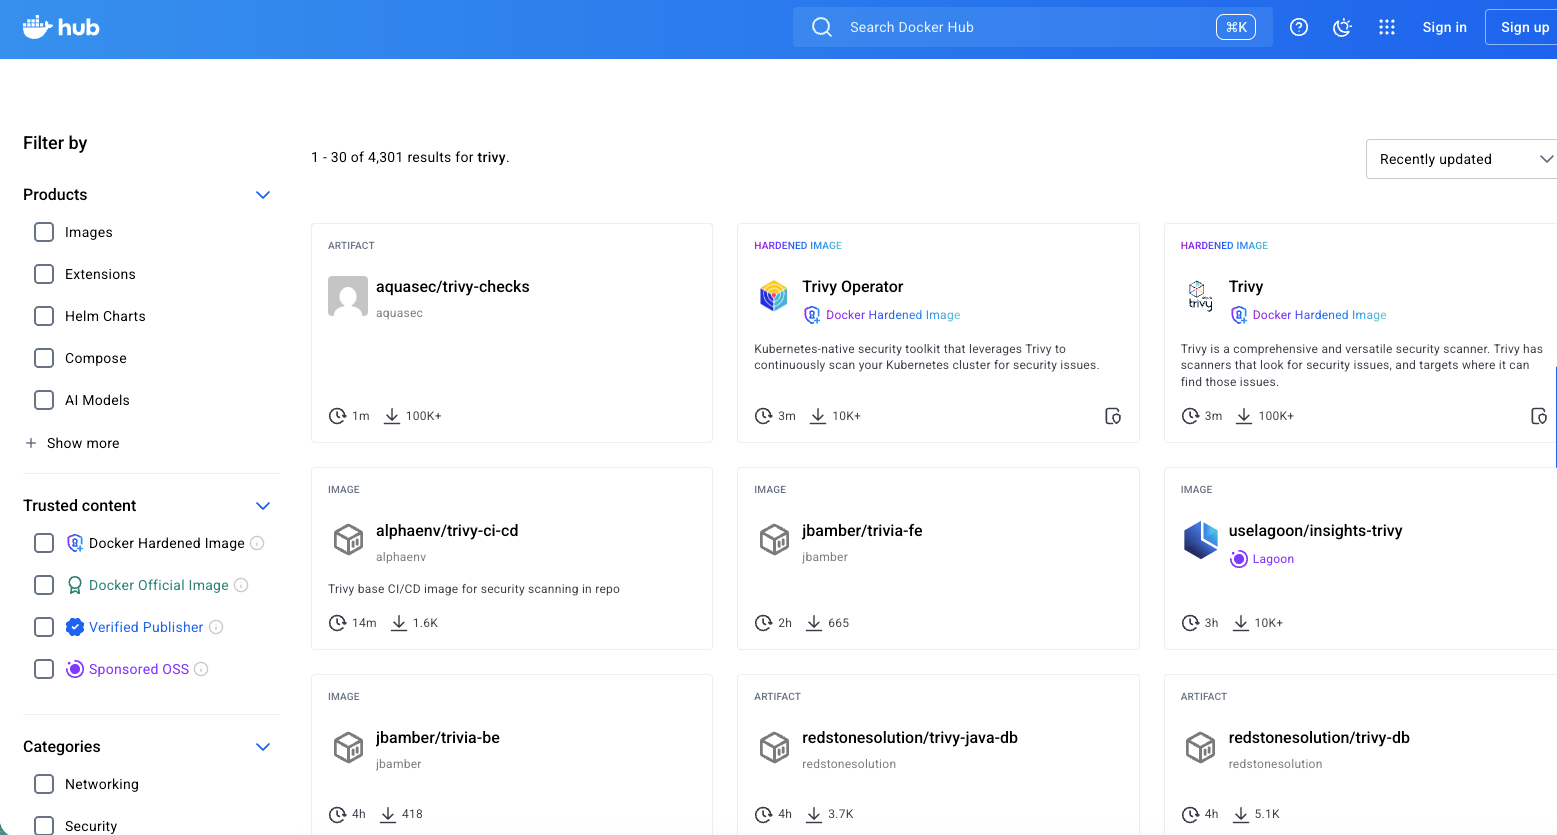
While these images are not inherently compromised, any that automatically pulled or rebuilt using affected versions during the attack window may have incorporated malicious components.
This significantly broadens the potential attack surface, especially for organizations relying on automated pipelines and dependency updates.
In response, organizations are already taking defensive measures. Maintainers of widely used open-source projects dependent on Trivy have begun revoking access tokens and transitioning to more secure publishing mechanisms, such as trusted publishing workflows.
Security teams are advised to immediately audit their CI/CD pipelines for Trivy usage, avoid affected versions, and treat any recent executions involving compromised images as potentially hostile.
As the investigation continues, this incident underscores the growing risks associated with software supply chains and the importance of strict integrity verification across development and deployment pipelines.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.


.webp?fit=1600,900&ssl=1&description=The ongoing supply chain attack targeting Aqua Security’s Trivy ecosystem has escalated, with new compromised Docker images discovered on Docker Hub.)