

Infamous Turla APT Hackers group renew its arsenal with a new hacking tool named “Topinambour ” also called as aka Sunchoke that is mainly used to target and compromise the government networks.
The newly added tool started using at the beginning of 2019, and the malware authors named it as Tonpinambour by themselves for this renewed hacking tool.
Turla APT group also known as Venomous Bear or Waterbug which is actively attacking various government network since 2004 especially in the Middle East, Central and Far East Asia, Europe, North and South America.
Turla is also responsible for some of the high-profile breaches including United States Central Command in 2008, Swiss military company RUAG in 2014, French Armed Forces in 2018 and the APT has actively attacked more than a decade.
In this campaign, this renewed tool relaying with .NET module which is intended to deliver the known KopiLuwak JavaScript Trojan and also it has heavily obfuscated PowerShell Trojan.
Threat actors randomly using various strings within this .NET module including “TrumpTower”, “RocketMan, “MiamiBeach” and is used as an initial message from compromised victims to control server, compromised WordPress websites where threat actor injected the .php scripts.
Topinambour Infection Process
The initial stage of an attack, threat actors using legitimate software installer that already infected by Topinambour dropper, which is one of the effective methods to bypass the internet censorship.
This dropper holding the .NET shell that will wait for Windows shell commands from threat actors. Using this .NET shell and rented SMB shares on virtual private servers (VPS), threat actors launch the next stage of malware using Windows shell commands such as “net use” and “copy”.
In this case, researchers stated that “It’s hard to believe, but SMB still works through public networks.” and the campaign-related VPSs are located in South Africa.
According to Kaspersky Research, ” The purpose of all this infrastructure and modules in JavaScript, .NET and PowerShell is to build a “fileless” module chain on the victim’s computer consisting of an initial small runner and several Windows system registry values containing the encrypted remote administration tool. The tool does all that a typical Trojan needs to accomplish: upload, download and execute files, fingerprint target systems. “
Threat actors creatively using a “make_some_noise()”, a remote shell persistence function to avoid detection from security detection software.
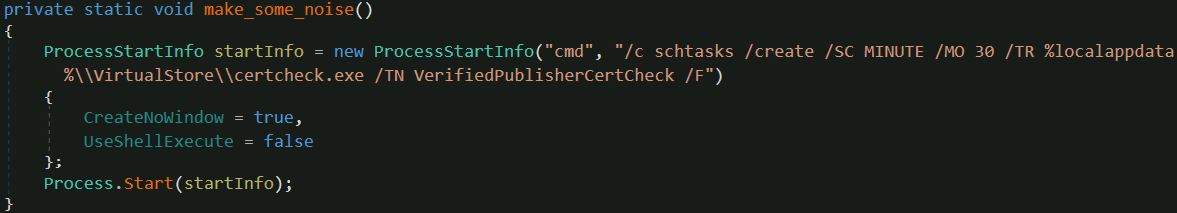
Tiny .NET shell receives the Windows shell commands from the Command & Control server and silently execute them.
Later, KopiLuwak dropper is ready to launch into the victim’s machine .NET remote shell silently downloads scripts from the C2 server using “Net use” and “copy” Windows shell commands and eventually victims infected with KopiLuwak obfuscated JavaScript.
“The downloaded script takes a binary from the Windows registry and runs it. The registry subkeys and values vary from target to target.”
Researchers believe that the development of KopiLuwak’s PowerShell and .NET modules to prevent the detection of the javascript version.
“Using the Windows system registry to store encrypted data that is later used by the malware also seems to be aimed at minimizing detection and reducing the digital footprint on any victim’s computer,” Kaspersky reported.
Indicators of compromise
Some campaign-related MD5 hashes
47870ff98164155f088062c95c448783
2c1e73da56f4da619c4c53b521404874
6acf316fed472300fa50db54fa6f3cbc
9573f452004b16eabd20fa65a6c2c1c4
3772a34d1b731697e2879bef54967332
d967d96ea5d0962e08844d140c2874e0
a80bbd753c07512b31ab04bd5e3324c2
37dc2eb8ee56aeba4dbd4cf46f87ae9a
710f729ab26f058f2dbf08664edb3986
Domains and IP’s – VPSs used as control servers
197.168.0.73
197.168.0.98
197.168.0.212
197.168.0.243
197.168.0.247
197.168.0.250
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity updates also you can take the Best Cybersecurity course online to keep yourself updated.
Also Read:
Turla APT Hackers Attack Microsoft Exchange Server using Powerful Malware to Spying on Emails
Turla Mosquito Hacking Group Exploiting Backdoor Using Metasploit To Compromise the Target System


