The insurance company, CNA Financial Corp., has been recently cyberattacked using a new variant of the “Phoenix CryptoLocker” Ransomware.
According to the reports, on March 21, 2021, the threat actors stationed a ransomware program on the IT network of CNA, and encrypted 15,000 devices.
However, to restore and regain all the controls of the hijacked systems and internal networks of the company, CNA Financial paid a massive amount of ransom to the hackers.

CNA Paid $40 Million in Ransom
CNA Financial Corp. is one of the largest insurance companies in the US, and to regain all the control of its internal IT network and infected systems they paid a hefty amount of $40 million at the end of March to the hackers.
As this ransom was demanded by the hackers who have used the Phoenix CryptoLocker ransomware to encrypt all the data on infected computers and the internal network of the company during the attack.
The ransom paid by CNA Financial to the hackers after two weeks of the attack, as a result of which the threat actors contrived to deaden the company’s internal network system.
But, according to the internal sources of the company, CNA tried to recover the data on its own, but they agreed to negotiate with the attacker after a week of unsuccessful attempts. And that’s why they yearned to maintain confidentiality since they have no right to discuss this concern openly.
Phoenix CryptoLocker and possible links to ‘Evil Corp’
Apart from the internal network of CNA, the Phoenix CryptoLocker also encrypted the computers of remote employees who were connected to the corporate VPN during the attack.
Throughout the encryption process, the ransomware added the “.phoenix” extension to all encrypted files and created a ransom note with the name, “PHOENIX-HELP.txt.”
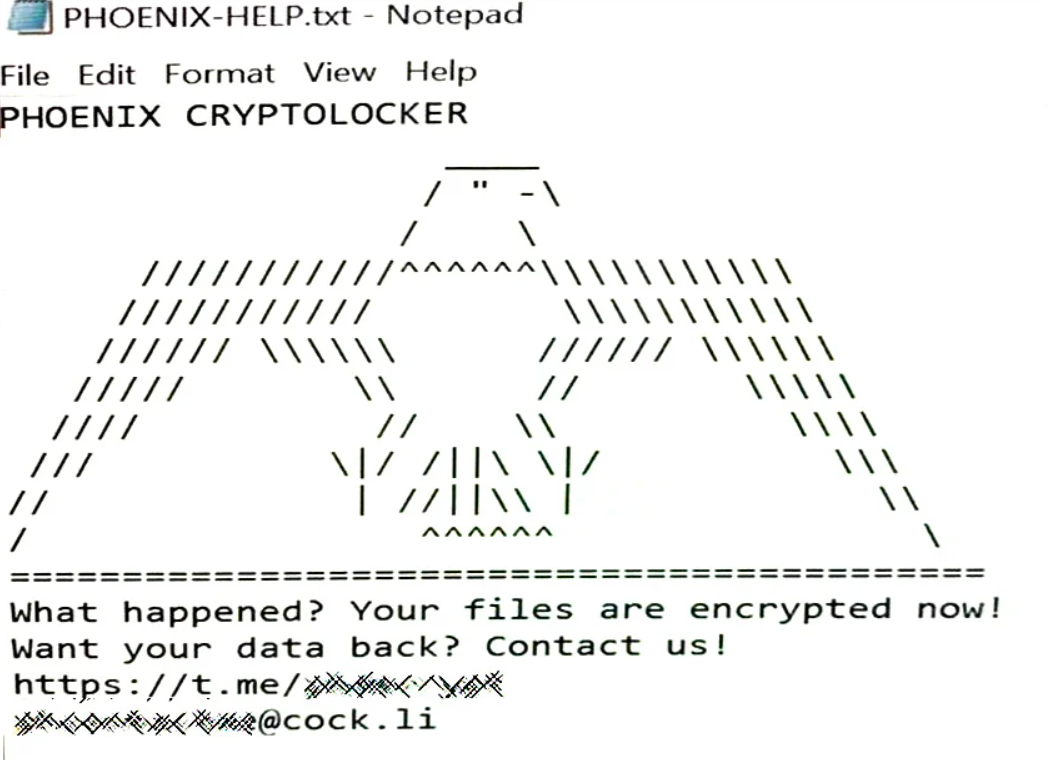
Moreover, the security experts have hinted that the popular cybercriminal group, “Evil Corp” is behind this Phoenix CryptoLocker ransomware. And this ransomware is the upgraded version of the WastedLocker ransomware.
The US government imposed sanctions on Evil Corp in 2019 and to avoid fines & lawsuits, most of the ransomware stopped facilitating the ransom payments to WastedLocker operators from the victims.
However, the company claimed that they have followed the law, consulted, and relinquished all the necessary data to the FBI and the Office of Foreign Assets Control of the US Treasury Department.
In short, CNA Financial has followed all the current guidelines to desist from violating any sanctions while paying the ransom amount to the threat actors.
But, according to an internal investigation, the hackers who have carried out this campaign were not subject to sanctions, so CNA decided to pay the ransom.
Restoration update
In an official web press, CNA has confirmed that they have now fully restored all their internal networks and operating usually. But, for further security measures they have claimed that they are implementing all the following points:-
- On the newly restored systems, they are deploying advanced endpoint detection and monitoring tools.
- To keep their network fully secured they are thoroughly scanning their systems.
- On detection of any indicators of compromise, deploying instant remedies.
- Before bringing back the systems online and making sure they are clean, the company also performing double checks.
These types of events are clearly showing that how hackers are using these types of ransomware operations as an easy and common tactic to steal unencrypted data. But, everyone should note down that always paying hackers doesn’t guarantee full recovery.