

Cybersecurity researchers at TrendMicro security firm have recently administered a very comprehensive insight into a productive hacking group operating as Hacker-for-Hire has targeted nearly 3500 individuals and corporations to steal their emails and highly-sensitive data.
This group has been implementing its attack since 2015, and after knowing about the attack, the senior researcher Feike Hacquebord of Trend Micro has implemented all the key details of the activities of the group, and later he named the attack “Void Balaur.”
Wide Range of Services & Targets
The hacking group of Void Balaur has been targeting different victims since 2015, but its initial report was disclosed from September 2017.
The Void Balaur has paid ads that were initially started to appear in 2018 on Russian-speaking forums like:-
- Darkmoney
- Probiv
- Tenec
- Dublikat
Moreover, in 2019, the group’s services increased their shell as they started to sell all the delicate data of Russian individuals, and the price starts from $21 and $124.
Data that were available for sale:-
- Passport and flight information
- Traffic camera snapshots
- Traffic police data (fines, car registration)
- Weapon registration
- Criminal records
- Credit history
- Bank account balance and statements
- Tax service records
A Comprehensive List of Victims
Here, the hackers have initiated attacks on the following entities:-
- Human rights activists
- Journalists
- Media websites
- Websites that broadcast political news
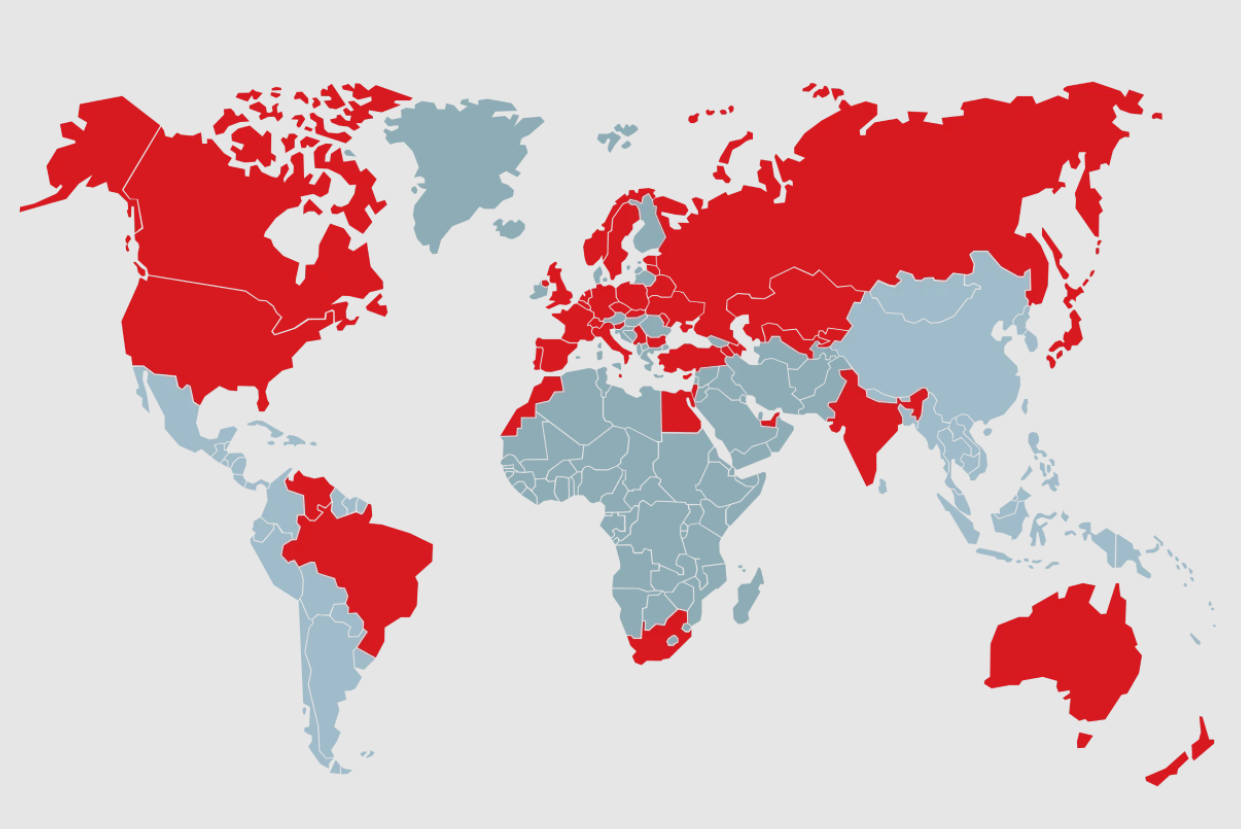
Void Balaur is not opposed to going after more high-profile targets, as recently the group has also propelled attacks on the former head of an intelligence agency, active government ministers, members of the national parliament in an Eastern European country, and even presidential candidates as well.
Recommendations
Here are some of the best practices that will surely help you to mitigate the consequence of an attack, not only this but it will also prevent an attack from being successful:-
- Initially, select email providers that prioritize security and have extreme security protocols.
- Always prefer Two-factor authentication (2FA) while email and social media accounts, rather than by using apps or devices especially produced for 2FA.
- Assure that apps that are being used to convey sensitive data must have end-to-end encryption for communications.
- Remember to delete older messages to reduce the chance of sensitive data ending up in the hands of malicious elements.
- Use drive encryption for every machine.
- Switch off both work and personal machines that collect important data when not in use.
- Estimate the use of encryption systems for communication that include delicate information or dialogue.
Following all these mitigations will surely help to stop this kind of attack, and the impact of such attacks are quite impactful, so, that’s why it is very important for the organizations to follow all the mitigations properly.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity, and hacking news updates.







