
Warden Stealer as a rapidly growing malware-as-a-service operation targeting data stored by AI assistants and coding agents, including Claude, Codex, Grok, and Cursor.
The Rust-based infostealer is among the first malware families observed systematically harvesting AI-agent configuration files, local tokens, prompt histories, conversation databases, and Model Context Protocol (MCP) settings.
The campaign signals a significant expansion of the infostealer threat model. Rather than stealing only browser passwords, cryptocurrency wallets, and session cookies, operators are increasingly pursuing AI tools as a concentrated source of credentials and sensitive developer context.
Local AI-agent data can expose access and refresh tokens, API keys, MCP connection details, project names, internal source-code context, and historical prompts that reveal an organization’s systems and ongoing work.
Researchers attributed CallbackBeaver to Warden based on technical overlap, including Rust development, highly distinctive code morphing, a dedicated loader, and matching cryptocurrency clipper configurations.
The malware supports Windows 8 through Windows 11 and is marketed as an expansive data-theft platform capable of collecting data from Chromium- and Gecko-based browsers, cryptocurrency wallet extensions, password managers, messaging apps, 2FA tools, and VPN clients.
Its actual collection scope varies by operator-controlled build configuration, enabling affiliates to customize targets and file-grabbing rules.
Warden version 1.9, announced on September 29, added officially advertised support for stealing tokens from AI coding agents.
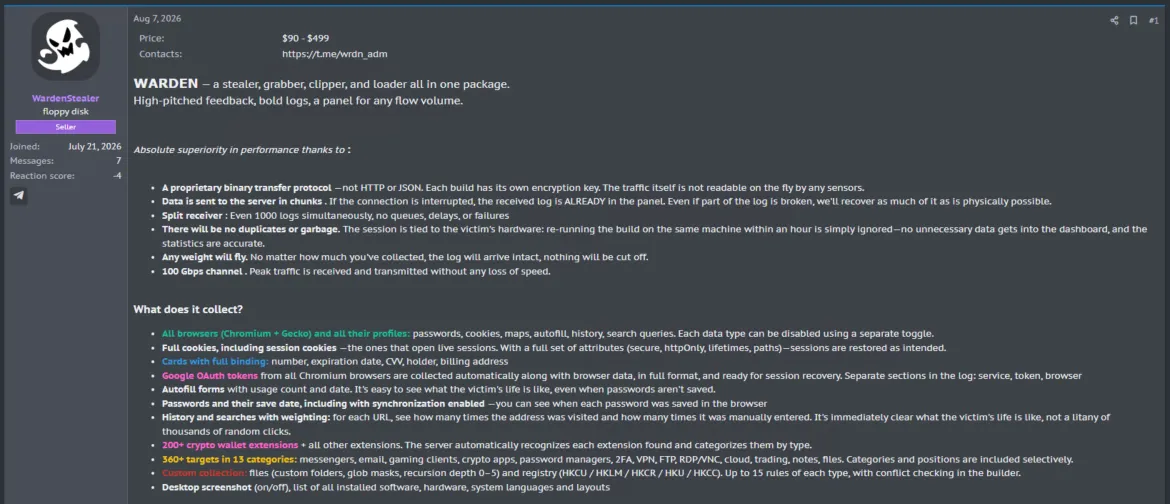
Earlier samples already contained custom collection rules for AI-agent data, indicating that operators had begun pursuing these artifacts before the capability became a mainstream feature.
The development matters because AI assistants increasingly function as a developer’s working memory.
A stolen archive can give attackers both a route into an account and the operational context to identify high-value projects, connected services, repositories, cloud environments, or credentials.
Unlike many MaaS stealers that leave payload delivery and evasion to affiliates, Warden includes its own loader and cryptocurrency clipper.
Gen said in a report shared with GBhackers, Warden Stealer as CallbackBeaver, has been advertised on Russian-language underground forums since August 2026.
Warden Stealer Malware
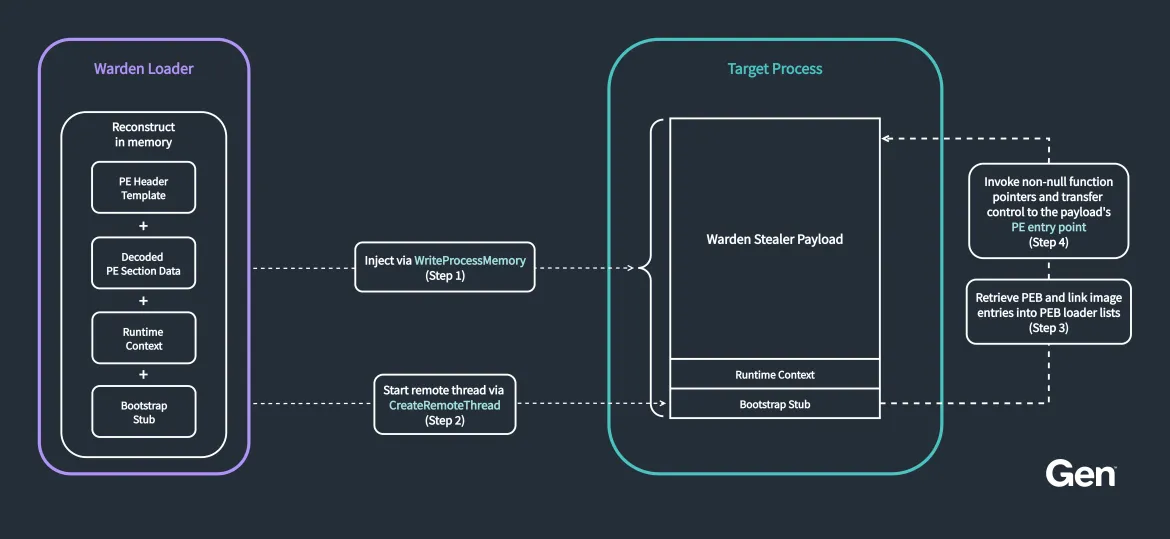
The loader reconstructs an embedded stealer payload in memory and commonly injects it into explorer.exe through remote-process memory allocation, payload writing, and remote-thread execution.
Its builds use a per-sample Base64-like encoding alphabet, custom LZSS-style decompression, lazy string decoding, dynamic API resolution, indirect control-flow obfuscation, opaque predicates, junk code, and constant masking.
The malware also inflates binaries with oversized PE overlays, a technique intended to complicate scanning, sandboxing, and automated analysis.
Warden conducts anti-virtual-machine checks through SMBIOS inspection, CPUID vendor checks, registry enumeration for VirtIO software, and display-adapter checks.
If it detects a virtualized environment, it halts its reporting workflow, helping operators reduce exposure to researchers and automated malware-analysis systems.
Warden also targets Chromium browser secrets protected by Application-Bound Encryption (ABE).
Google introduced ABE to bind encrypted browser data to the legitimate application and machine, making ordinary malware decryption attempts fail unless attackers elevate privileges or inject into Chrome.
Researchers found that Warden scans browser memory for the v20 key material associated with Chromium’s encryption system, then injects shellcode into the browser process to invoke CryptUnprotectMemory.
This allows the malware to decrypt the browser’s v20_master_key within the process context where Windows permits the operation.
The technique resembles recent ABE bypass work observed in Vidar and Remus. Vidar, for example, extracts the encrypted browser key from memory and executes decryption within the victim browser process through code injection.
Warden’s implementation differs in execution details, suggesting independent development rather than a direct code copy.
Warden is delivered through common infostealer channels, including cracked software, game cheats, malvertising, and ClickFix campaigns.
Organizations should now include AI assistants in endpoint inventories, secret-management reviews, and incident-response playbooks.
After a suspected infostealer infection, teams should revoke AI-service sessions, rotate API keys and MCP-linked credentials, review agent-connected applications, investigate prompt and conversation-history exposure, and assess whether browser sessions or developer credentials were stolen.
Local agent files should be treated with the same sensitivity as browser profiles, password stores, cloud CLI credentials, and source-control tokens.
Indicators of Compromise
| Malware | Hash Type | Hash |
|---|---|---|
| Warden Loader | SHA-256 | 006510ce1da2b7410376f0788c19e55616eb4bcc30072d25b7d0871dc32aa11c |
| Warden Loader | SHA-256 | 0d727a4ef1178e767afdd0080ba1ebda0f24ac52b639f0501021affd8f88d26a |
| Warden Loader | SHA-256 | 63959ef6309cd01b5d3c7262a3a41394dca2db2dc74bd030a517b7e23a2c3fef |
| Warden Loader | SHA-256 | 77c8266935bc040c992ab70abd402bd203b9c12e7548c80b84fd21308c250f0e |
| Warden Loader | SHA-256 | 77cc246272f2af21b64bbc6c6173d57affee97eb0ccf747d89492d06d4c52865 |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
Stops Cyber threats before impact with 21 min faster MTTR. Integrate ANYRUN’s Sandbox in your SOC.


