

The majority of top-ranked websites (100,000 websites) include malicious keyloggers that are designed to capture every single character that you type or enter in forms before submitting like:-
- Signing up for a Newsletter
- Making a hotel reservation
- Checking out online
The top 100,000 websites were crawled and analyzed by researchers at the following universities:-
- The University of Lausanne
- The KU Leuven
- The Radboud University
The aim of this study is to look at how users might interact with a site while inside the European Union and while inside the USA.
In-depth Analysis
The researchers determined that there were 1,844 websites that recorded the email of EU users without their permission and that 2,950 of these gathered a US user’s email address without their consent.
During a specific crawl of password leak websites in May 2021, the researchers found 52 instances of third-parties collecting password data before submission, including Yandex from Russia.
In the meantime, the 52 cases reported by the group were all resolved after they were disclosed to those organizations. A keystroke feature in some websites is used to log the data from keystrokes as they are keyed in.
The trouble with this is that there are plenty of websites that get the complete submission from one field when the user clicks on the next.
Here’s what a privacy and identity researcher at KU Leuven and one of the study co-authors, Asuman Senol stated:-
“In some cases, when you click the next field, they collect the previous one, like you click the password field and they collect the email, or you just click anywhere and they collect all the information immediately. We didn’t expect to find thousands of websites; and in the US, the numbers are really high, which is interesting.”
Because of the General Data Protection Regulation of the EU, it has been suggested regional differences are caused by European companies being more cautious about tracking users, and even possible integration with fewer third parties.
During the meeting, the group discovered that Meta Pixel and TikTok Pixel are invisible marketing tracking tools that web-based services incorporate into their websites in order to track consumers across the web and target them with advertisements.
While it has been confirmed that 8,438 sites may have been sending information to Meta (Facebook’s parent company) through “pixels” of the US users. Apart from the US, in total, there are 7,379 sites that are likely to be affected by users in Europe.
LeakInspector
You may not be able to fully protect yourself from all collection attempts by simply removing your data from a form before submitting it. That’s why a new addon for Mozilla Firefox has been developed by the experts which is dubbed, “LeakInspector.”
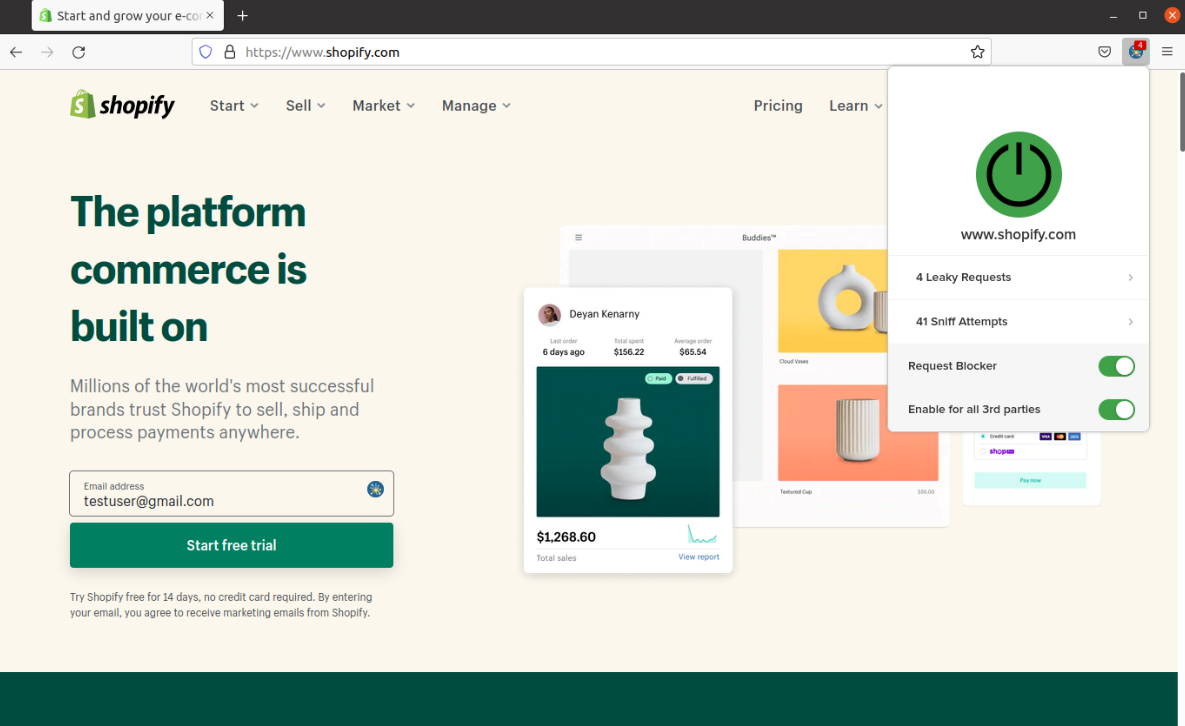
LeakInspector highlights input fields that contain personal data when tracker scripts read (“sniff”) these fields and block leaky requests.
Technology firms are looking at restricting the use of cookie-based tracking as a means of protecting privacy. There will be a growing reliance on static IDs, such as phone numbers and email addresses by marketers and analysts.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.







 include malicious keyloggers that are designed to capture every single character.)