

Recently cybersecurity researchers has recently discovered a severe vulnerability in the IIS (Internet Information Services) of Windows. Though Microsoft has recently fixed this critical vulnerability in patch Tuesday released in 12 may, and it’s tracked as CVE-2021-31166.
Many security experts and security companies have claimed that this vulnerability is one of the most critical security flaws that have been detected and fixed by Microsoft this month.
HTTP Protocol Stack RCE Vulnerability
This critical flaw (CVE-2021-31166) is akin to corruption of information in the memory of the HTTP protocol stack (HTTP.sys) that is already included in all the recent versions of Windows.
- CVE ID: CVE-2021-31166
- Assigning CNA: Microsoft
- Released: May 11, 2021
- CVSS: 3.0 (9.8 out of 10)
In general, this HTTP Protocol Stack is used by the Windows IIS (Internet Information Services) server, so, the security expert, Axel Souchet, who used to work for Microsoft has explained that if this server is active, then an attacker can easily send it a specially crafted packet to execute malicious code at the OS kernel level.
This security flaw is quite similar to another Microsoft vulnerability that was detected in the HTTP network stack. It was tracked as CVE-2015-1635 and detected or reported by the security experts in 2015.
Moreover, it becomes worse when Microsoft warned that this RCE vulnerability has the potential of a worm, as it can be used by the threat actors to create malware that spreads itself from server to server.
PoC for CVE-2021-31166 triggers Blue Screen of Death (BSOD)
To show the flaw in action the former Microsoft security researcher, Axel Suchet published a PoC exploit for CVE-2021-31166 (“HTTP Protocol Stack Remote Code Execution Vulnerability”).
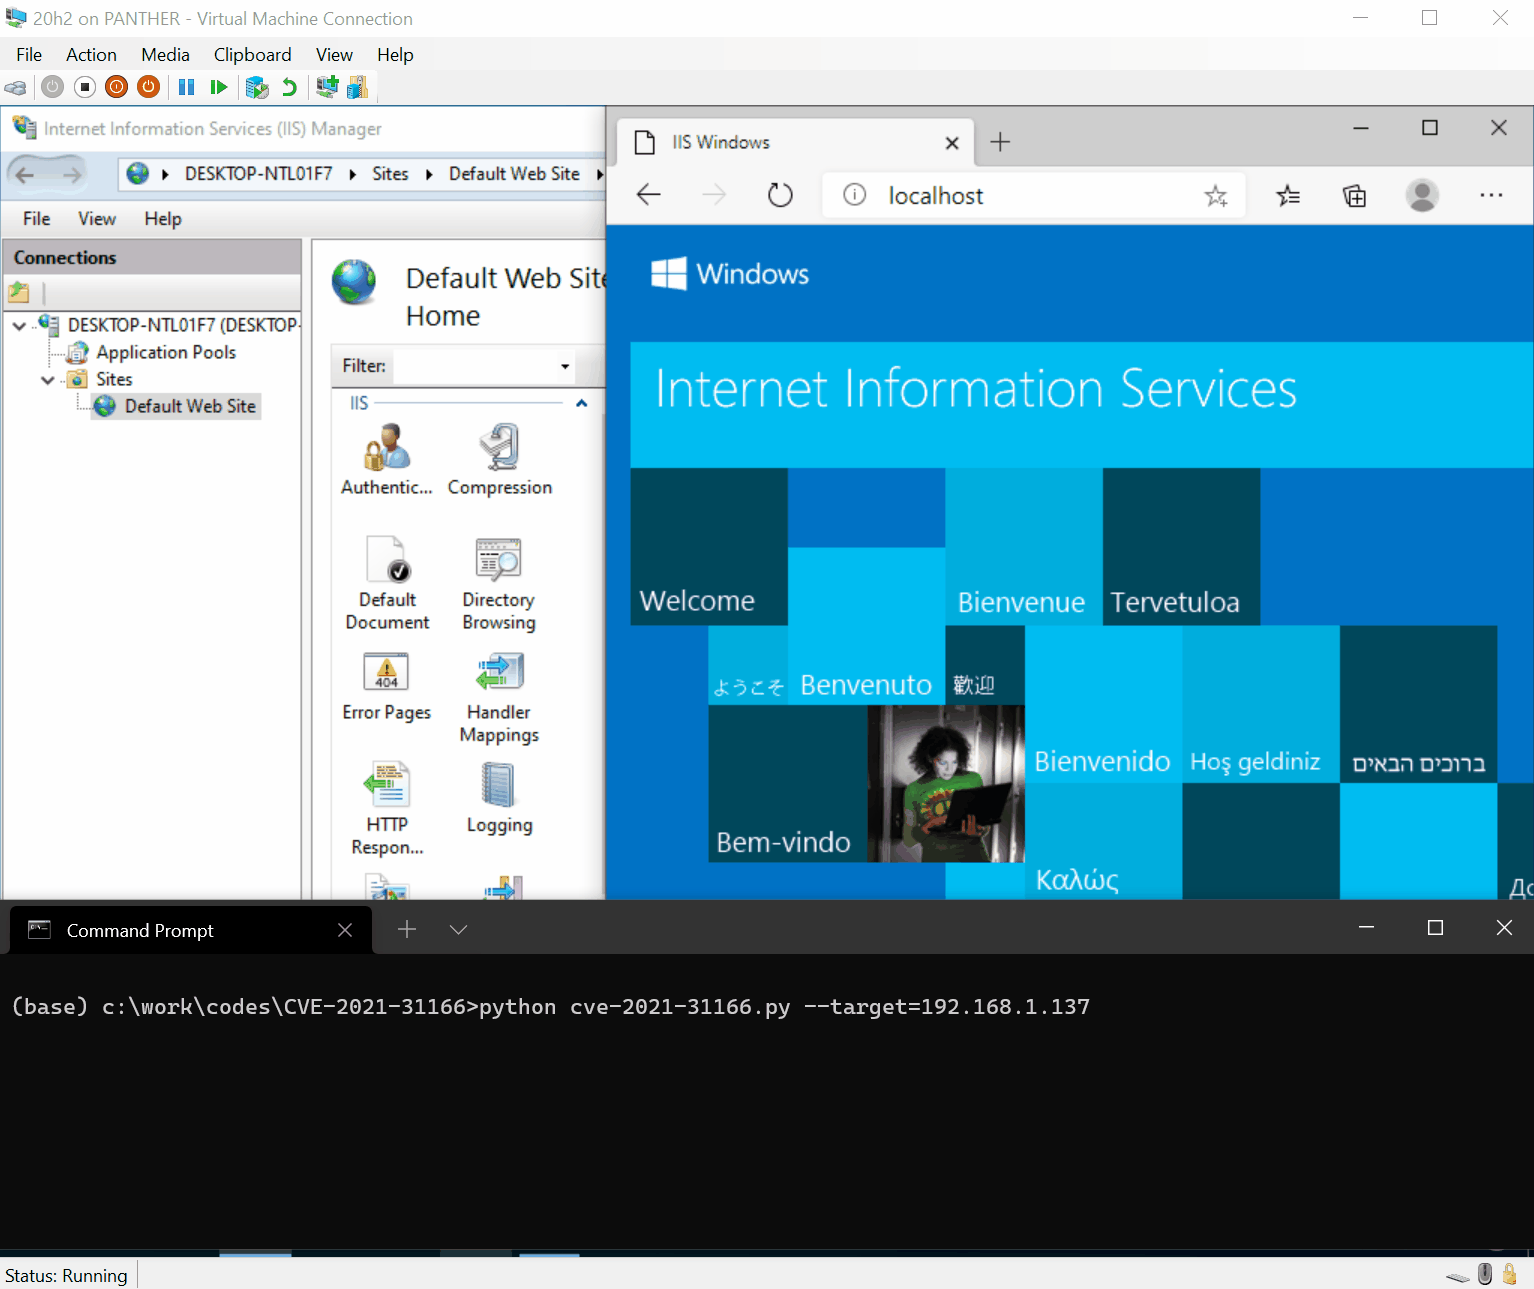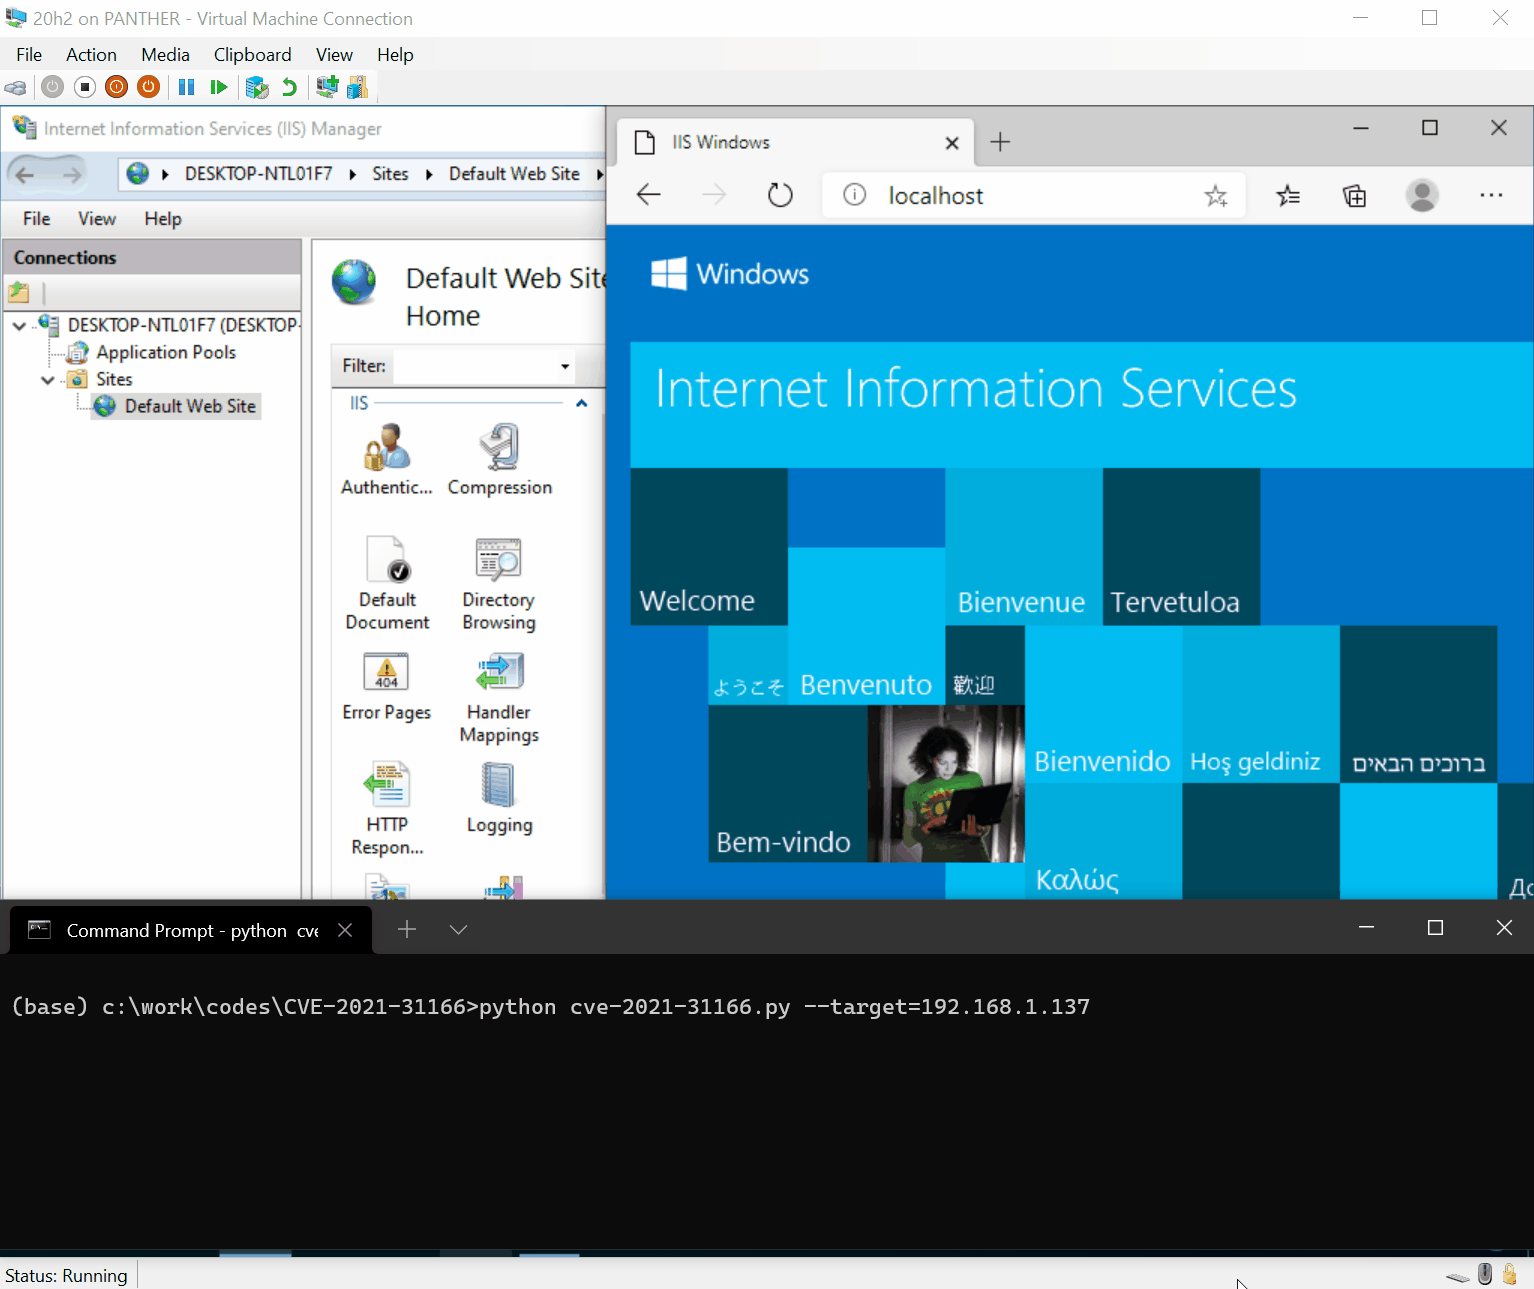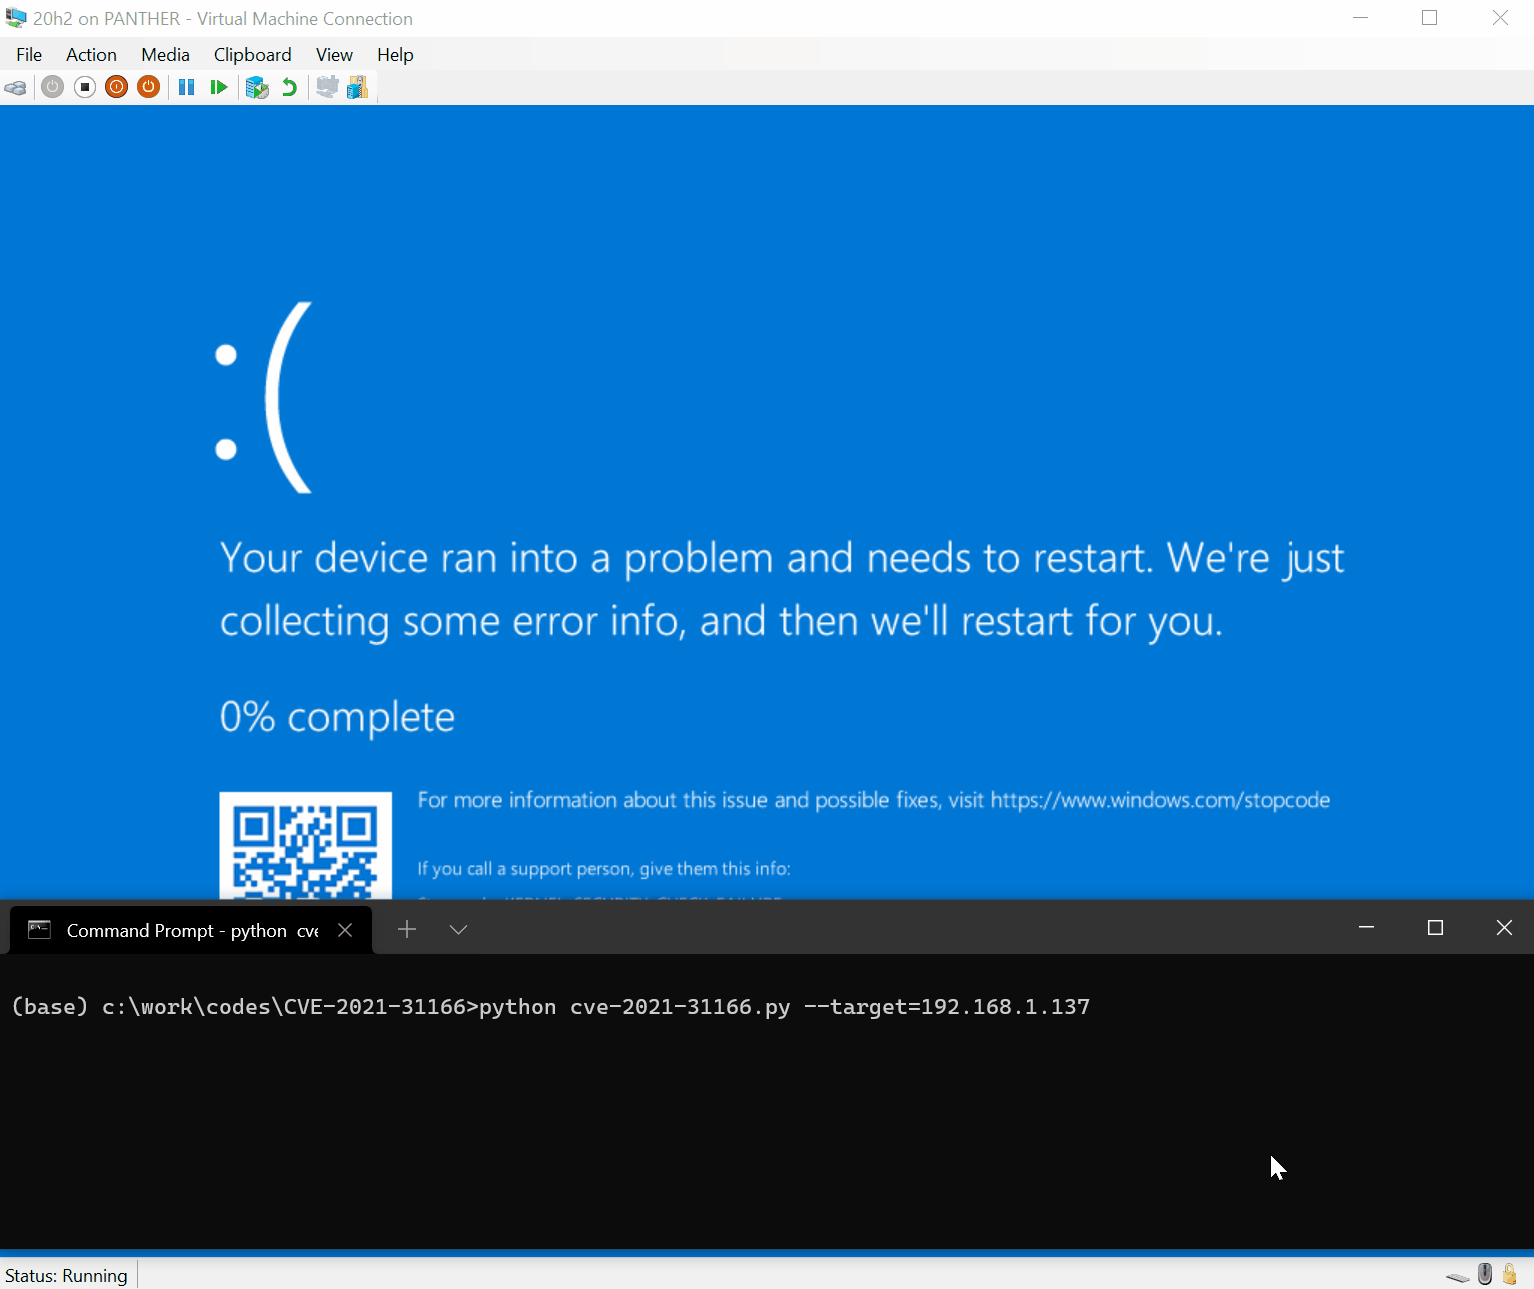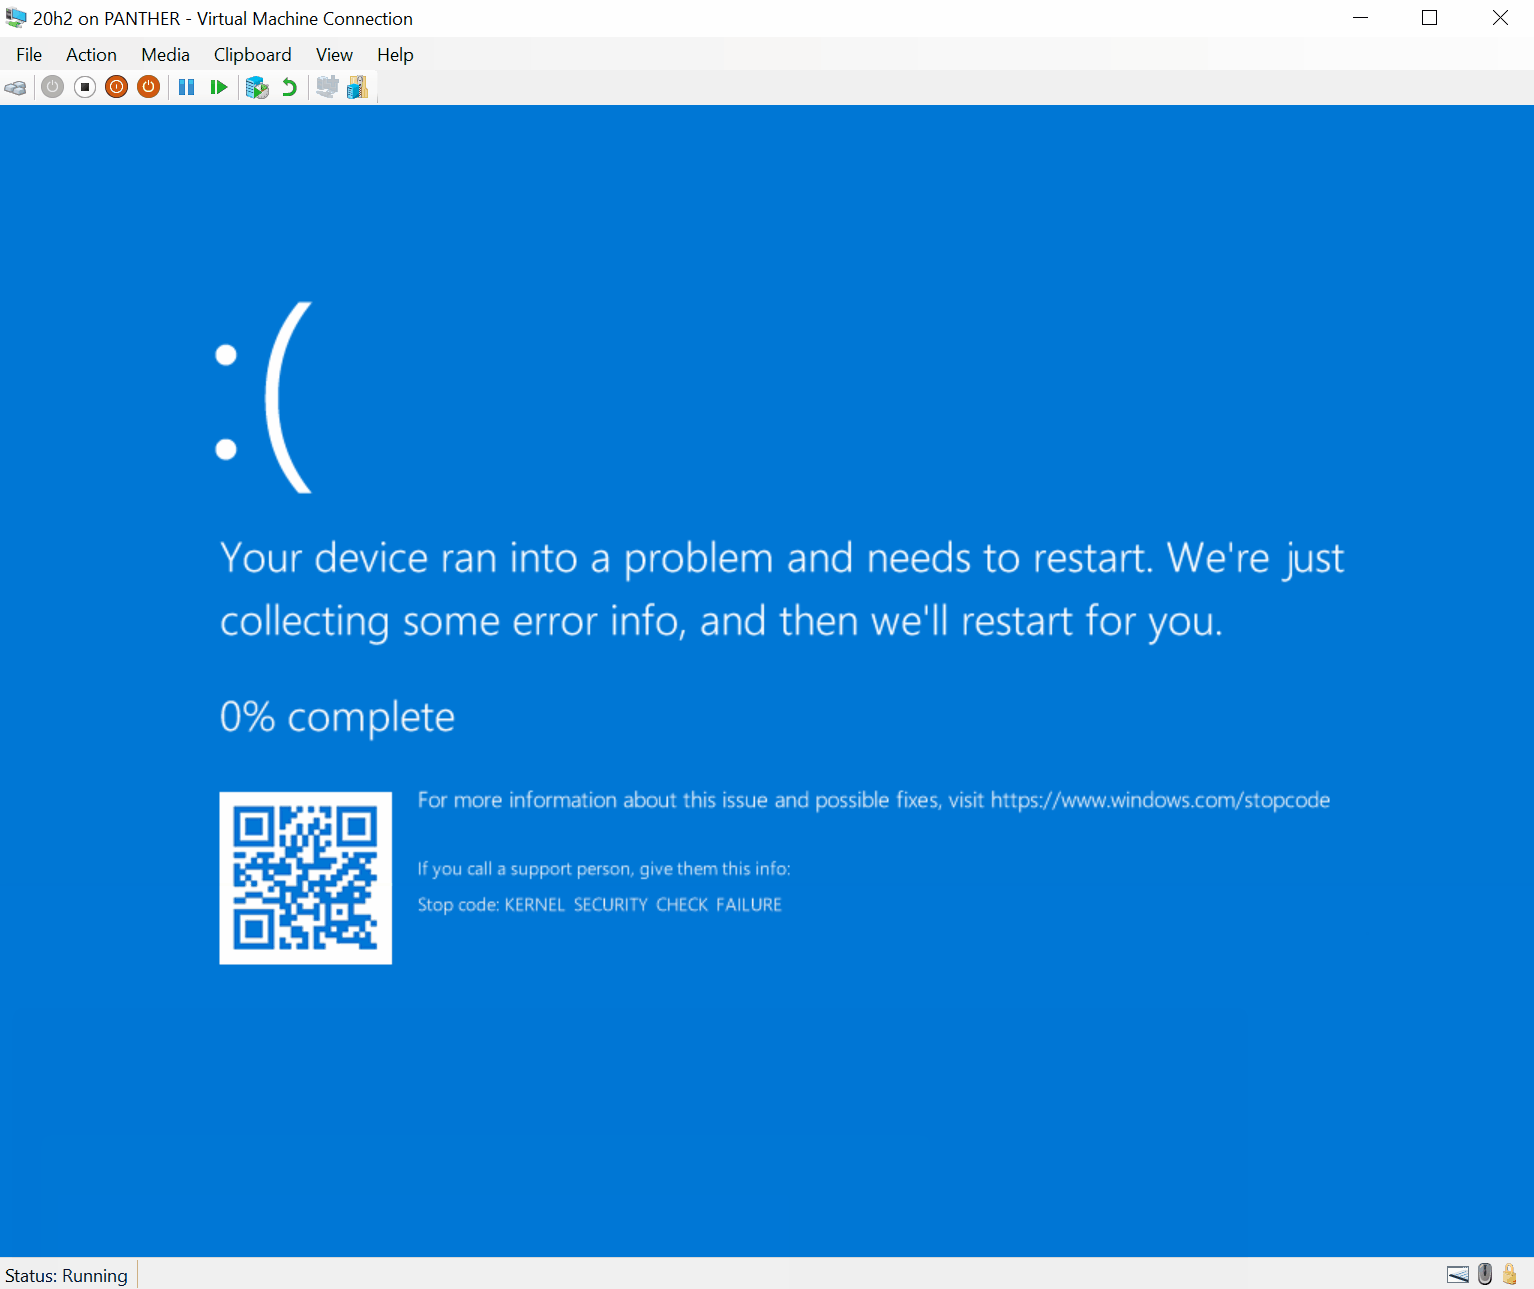
From the above image, you can see the flaw in action, and how this critical flaw triggers the Blue Screen of Death (BSOD). Here, Axel explains that where the function has a local LIST_ENTRY, this bug happens itself in the “http!UlpParseContentCoding” and then it affix the item to it.
And here the interesting thing is that it does not NULL out the local list (LIST_ENTRY) after it moves it into the Request structure when it is done.
It means that an attacker can easily leave all the entries of the local list in a hanging state in the Request object by triggering the code path that unlocks all the entries of the local list.
Possible targets are safe from attacks
Axel Suchet claimed since the capabilities of the HTTP Protocol Stack RCE flaw are artificially limited, so, it is likely that most of the potential targets are safe from such attacks.
While this security flaw only affects the newest OS versions like Windows 10 2004 and 20H2, as well as Windows Server 2004 and 20H2, and all these versions are not yet very widespread.
Moreover, the vulnerability CVE-2021-31166 does not allow the formulation of a full-fledged worm, and it only leads to a “crash” (DoS) of unpatched Windows versions that are running the IIS server.
But, apart from all these things, the security team at Microsoft has strongly recommended all its users to install all the security updates published on an immediate basis.







. read more here.)