
Hackers have weaponized a WinRAR path-traversal flaw tracked as CVE-2025-8088 to silently plant a Startup shortcut and run a multi-stage PowerShell loader that maps a headerless, reflectively loaded PE in memory.
The campaign reuses the Ukrainian reconnaissance-themed lure seen in earlier UAC-0226/GIFTEDCROOK activity but significantly advances operational packaging: instead of relying on a user to launch a visible shortcut, the adversary exploits NTFS Alternate Data Streams (ADS).
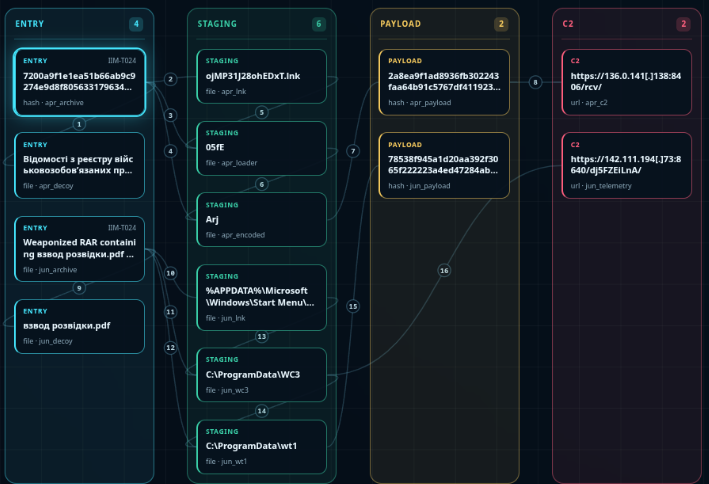
Inside the RAR to write a .lnk directly into the current user’s Startup folder and drop two encoded stages into C:\ProgramData.
When the victim next logs in the planted shortcut launches a minimized CMD that spawns hidden PowerShell processes which IEX the staged script from C:\ProgramData\WC3, removing the need for a remote download at execution time.
The PowerShell stage (WC3) is highly noisy by design thousands of junk functions, random identifiers and Write-Host calls but contains a compact execution core that waits 60 seconds, decodes a 1,131,008‑byte blob (wt1) by subtracting 0x48 from each byte, allocates executable memory through native APIs.
(NtAllocateVirtualMemory/NtProtectVirtualMemory), copies the decoded bytes, and creates a thread at a fixed offset: 0x173B0.
According to Synaptics, the PowerShell loader is still buried under generated garbage, but the payload behind it is more interesting: an additively encoded, headerless PE image containing its own reflective mapper.
That offset resolves to an exported function Main.dll!Func inside the reconstructed image, revealing the actor’s intent: the exported routine implements a custom reflective PE mapper rather than the stealer’s core logic.
WinRAR CVE-2025-8088 Exploited
The decoded blob is not a conventional PE on disk; it is a headerless image with a small custom header that supplies metadata (original ImageBase 0x180000000, SizeOfImage 0x11A000, entry RVA, export/import/reloc RVAs).
This iteration differs from the April UAC-0226 sample mainly in packaging and resilience: ADS-based silent planting into Startup, a headerless PE with a custom reflective mapper, loader telemetry, and explicit, broader collection logic.
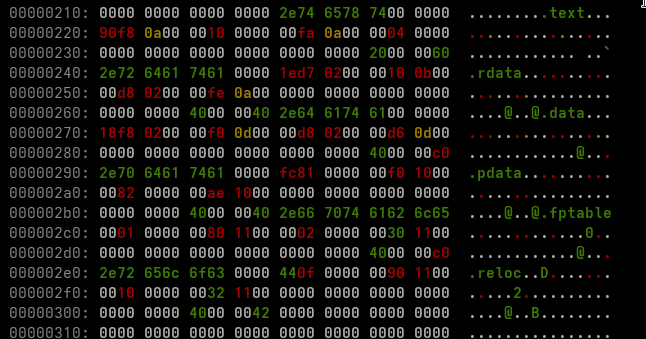
0x400 bytes form a custom header (Source : Synaptics).The reflective mapper in memory performs PEB-walking API resolution, allocates full SizeOfImage, copies sections, resolves imports, applies relocations, sets permissions and calls DLL_PROCESS_ATTACH.
This architecture hides a meaningful amount of static indicators: the file on disk lacks MZ/PE headers and the payload never needs to be written as a conventional DLL.
The loader also writes four 32-bit status values (thread exit code and three mapper-status fields) and POSTs the 16-byte telemetry to hxxps://142.111.194[.]73:8640/dj5FZEiLnA/ after globally disabling TLS validation, giving the operator granular feedback (mapping started, relocations failed, entry reached, payload exited) separate from the payload.
Inside the reflectively mapped module, strings are protected with an RC4-like stream cipher operating on UTF‑16 words; most strings were reconstructed statically, revealing targeted collection modules.
The payload implements dedicated browser and file theft: Chromium-family (Chrome, Edge, Opera) credential and cookie harvesting using CryptUnprotectData, Firefox profile collection (logins.json, key3/key4.db, cookies.sqlite).
Broad document/archive/VPN/keystore collection including .ovpn, .kdbx and .jks. Local staging occurs under user-profile paths and a randomly named ZIP container likely assembles harvested material before exfiltration.
Persistence cleanup paths reference ProgramData and Startup and include delayed self‑deletion routines, but the initial persistence is accomplished by the ADS-placed Startup LNK.
Infrastructure fingerprints persist hosting via evoxt.com but operators adjusted TLS certificates, changed the callback port from 8406 to 8640 and replaced the static /rcv endpoint with a randomized path, likely to evade YARA/EDR signatures and network detections.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.


