

A state-sponsored hacking group, WIRTE has been active since at least 2019 that targets high-profile public and private entities in the Middle East using weaponized MS Excel 4.0 macros as droppers.
The cyber security researchers at Kaspersky have closely investigated the following things to know the motives of WIRTE:-
- Campaign
- Toolset
- Methods
But, after analyzing the above things they have concluded that the motives of WIRTE are still not clear, but, it has been reported that with the Gaza Cybergang threat actors WIRTE group has some links.
Tricky dropper
And not only that even they have also observed targets in other regions apart from the Middle East. While as compared to other hacking groups, WIRTE has superior skills like:-
- Better OpSec
- Better stealthy techniques
- Better evasion
- Better persistence
On recipients’ devices the hackers from WIRTE hacking group download and install malware payloads by executing the MS Excel macros that are sent via phishing emails.
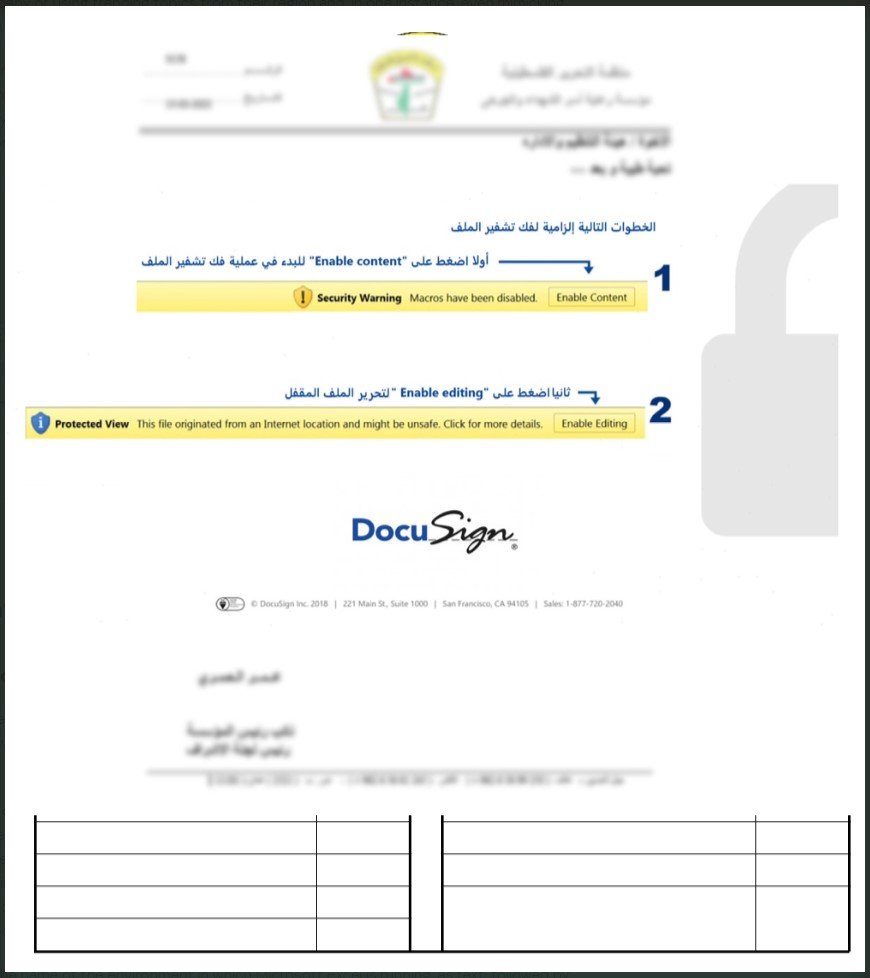
Initially, in a hidden column, the Excel dropper runs a series of formulas to enable the editing request. Later, the third spreadsheet with hidden columns runs the dropper and checks the following anti-sandbox checks that we have mentioned below:-
- Get the name of the environment
- Check if a mouse is present
- Check if the host computer can play sounds
Targets
The primary focus of the WIRTE:-
- Government entities
- Diplomatic entities
- Financial institutions
- Law firms
- Military organizations
- Technology companies
Actions
During the investigation process, the experts have observed several commands and actions that we have mentioned below:-
- List local disk drives
- Get the list of installed AV software
- Check if the current user is an admin
- Get OS architecture
- Check for the existence of backdoor services
- Check for registry keys added for COM hijacking
- List all installed hotfixes
- Get a screenshot and save it to %AppData% until the next POST request
Hidden command and control
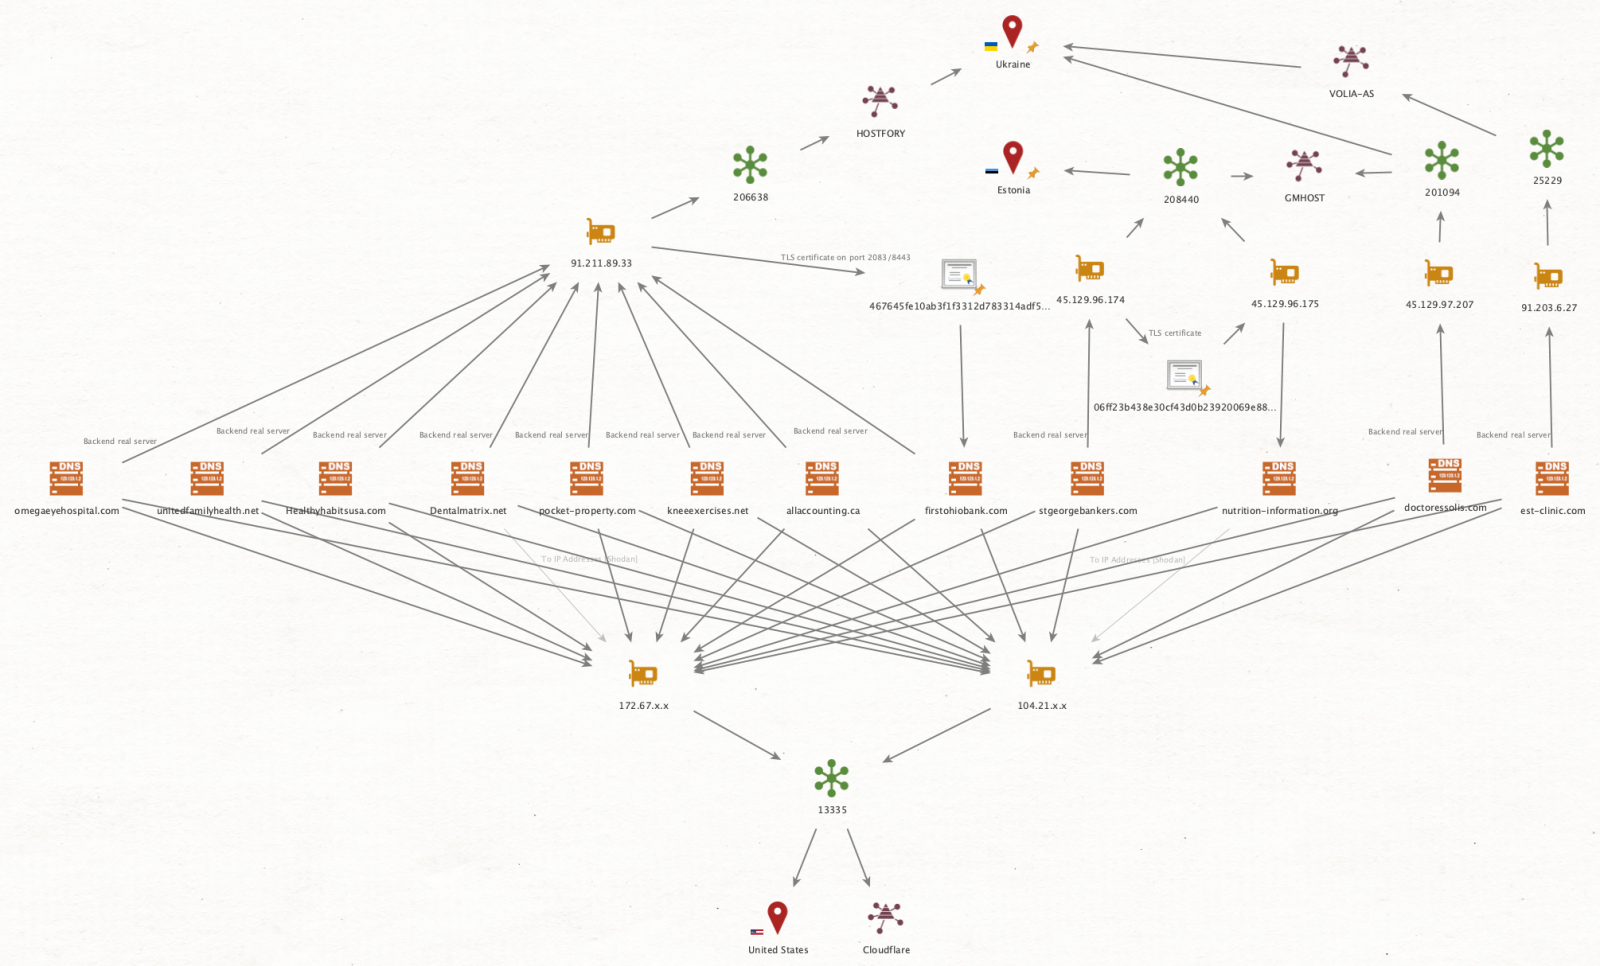
To hide the actual IP addresses the hackers place their C2 domains behind Cloudflare. However, the security analysts at Kaspersky have managed to identify some that are hosted in the following countries:-
- Ukraine
- Estonia
But, the threat actors have used TCP ports 2096 and 2087 along with TCP/443 over HTTPS in C2 communication for their most recent intrusions.
Apart from this, the most serious thing about their actions is that WIRTE hacking group is expanding its targeting scope to several organizations including financial institutes and large private organizations.
That’s why as a recommendation the analysts have strongly recommended organizations to stay alert and develop their security practices to mitigate such situations.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity updates.







