

Researchers from Wordfence uncovered two RCE vulnerabilities in WordPress SEO plugin called Rank Math let hackers hijack nearly 200,000 vulnerable Websites and gain remote access.
Rank Math is an SEO plugin for WordPress and it gives various SEO features such as Setup Wizard, Google Schema Markup, Optimizes Unlimited Keywords with 200,000 active installations.
The first vulnerability is the most critical one that allows attackers to update arbitrary metadata, including the ability to grant or revoke administrative privileges.
The second vulnerability lets attackers redirect the victims to any website for their choice and any location on the site.
Rank Math’s one of the SEO features allow users to update Metadata on the post. To use this feature, plugin registered a REST-API endpoint that failed to include a permission_callback used for capability checking.
A function called “update_metadata” which you can see in the below image is used to update the slug existing posts or could be used to delete or update metadata for posts which enable this critical vulnerability and it can be exploited
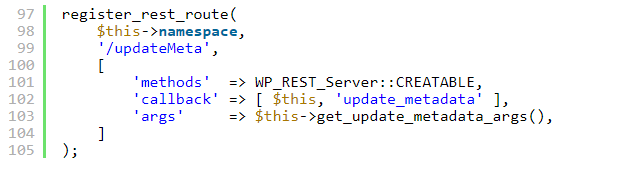
According to WordFence report ” WordPress user permissions are stored in the usermeta table, which meant that an unauthenticated attacker could grant any registered user administrative privileges and remove the existing admin privilege.
If the site has the single administrative right, then the attacker could lock an administrator out of their own site.
The second vulnerability existing in a module that can be used to create redirects on a site and the feature can be used by registered a REST-API endpoint, which is again failed to include a permission_callback for capability checking.
“The endpoint called a function, update_redirection, which could be used to create new redirects or modify existing redirects, with an important limitation”
According to the researchers “The redirect could not be set to an existing file or folder on the server, including the site’s main page. This limited the damage to some extent in that, while an attacker could create a redirect from most locations on the site, including new location”
Also attacker will lock the existing content access in the site except the home page and redirect the visitors to the malicious website that hosted by the attacker.
Also Read: WPScan – Penetration Testing Tool to Find The Security Vulnerabilities in Your WordPress Websites
You can share your thoughts about the article via Twitter, Facebook and Linkedin page also get the Daily cyber security & hacking news updates.







