

A critical privilege escalation vulnerability discovered in the Advanced Custom Fields: Extended WordPress plugin threatens over 100,000 active installations.
The vulnerability, identified as CVE-2025-14533 with a CVSS score of 9.8, allows unauthenticated attackers to elevate their privileges to administrative by exploiting a misconfigured user registration form.
The Advanced Custom Fields: Extended plugin, an addon for the widely-used Advanced Custom Fields suite, fails to enforce role restrictions in its “insert_user” form action function.
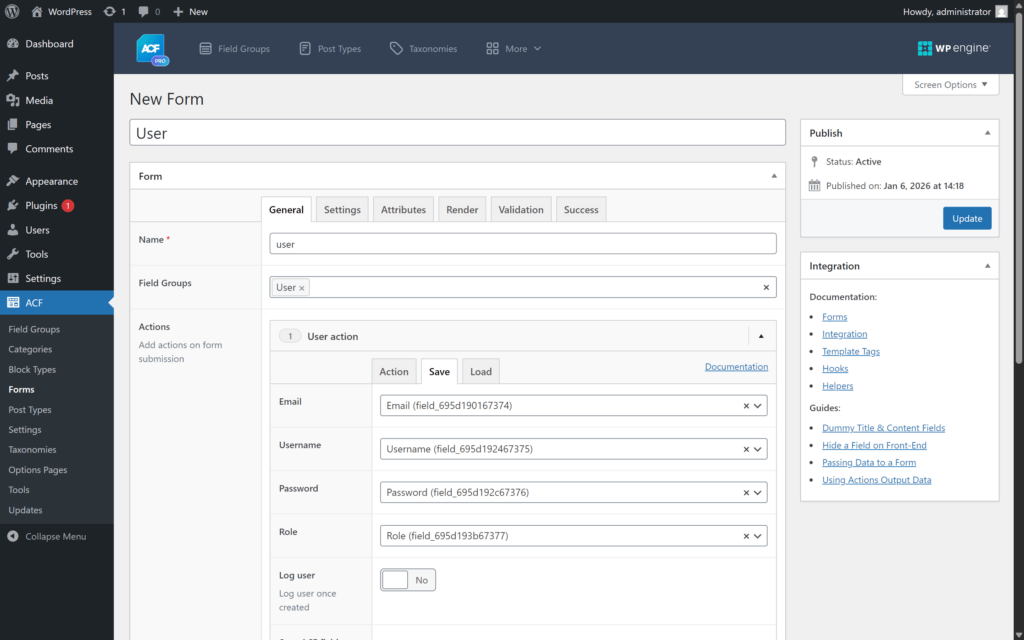
When a form contains a mapped role field, attackers can arbitrarily assign themselves the “administrator” role during user registration, bypassing all intended access controls.
The vulnerability affects all versions up to and including 0.9.2.1, with patches available in version 0.9.2.2.
Andrea Bocchetti, a security researcher, discovered the vulnerability through the Wordfence Bug Bounty Program and earned a $975 bounty for responsible disclosure.
| Field | Details |
|---|---|
| CVE ID | CVE-2025-14533 |
| CVSS Rating | 9.8 (Critical) |
| Affected Versions | ≤ 0.9.2.1 |
| Patched Version | 0.9.2.2 |
| Bounty | $975.00 |
The researcher identified that while the plugin offers an “Allow User Role” restriction setting at the field group level, this restriction is completely ignored when processing form submissions, creating a dangerous inconsistency between intended and actual functionality.
Attack Scope and Impact
The vulnerability critically impacts WordPress site owners who have deployed “Create user” or “Update user” form actions with role fields.
Once an attacker gains administrative access, they can execute arbitrary code by uploading malicious plugins or themes, inject spam content into pages, redirect visitors to phishing sites, or establish persistent backdoors for long-term compromise.
The attack requires no authentication, making exploitation trivial for threat actors.
Mitigations
Wordfence disclosed findings to the ACF Extended development team on December 11, 2025. The vendor responded swiftly, releasing a patched version on December 14, 2025.
Premium Wordfence users received firewall protection on December 11, while free users obtained the same safeguard on January 10, 2026, following the standard 30-day protection delay.
Site administrators should update Advanced Custom Fields: Extended to version 0.9.2.2 or later immediately.
Organizations using affected versions with active user registration forms face heightened compromise risk.
The Wordfence Vulnerability Management Portal continues monitoring for exploitation attempts, while organizations without current security tools should prioritize updates before threat actors develop automated exploitation frameworks.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.


