

Exploit acquisition platform Zerodium released a new payout for mobile exploits with surprising payment for both Android and iOS platforms.
Zerodium, a Cybersecurity company known for buying premium exploits from security researchers for several platforms including Operating Systems, Web Browsers, Mobiles, Web Servers, Email Servers, WebApps/ Panels.
Unlike the majority of existing bug bounty programs that accept almost any kind of vulnerabilities and PoCs but pay very low rewards but Zerodium mainly focuses on very high-risk vulnerabilities and with fully functional exploits.
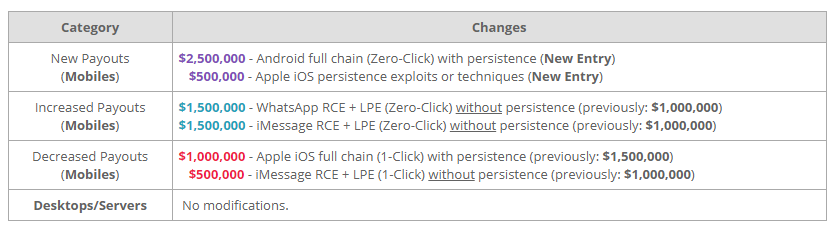
According to New payout release, Zerodium now paying more for Android Exploits than iOS, In which, they are paying $2,500,000 for Android full chain (Zero-Click) with persistence exploit and $1,500,000 for iMessage RCE with LPE( Local Privilege Escalation).
It’s a surprising moment for bug bounty community to earn more money by reporting quality of mobile zero-day exploits and there is no price changes for Desktops/Servers exploits.
In the Mobile platform, Zerodium Increased Payouts for WhatsApp RCE and iMessage RCE + LPE (Zero-Click) without persistence from $1,000,000 to $1,500,000.
Also decreased the payout from $1,500,000 to $1,000,000 for Apple iOS full chain exploit and $1,000,000 to $500,000 for iMessage RCE + LPE without persistance.
According to ZERODIUM new report, “The amounts paid to researchers to acquire their original zero-day exploits depend on the popularity and security level of the affected software/system, as well as the quality of the submitted exploit (full or partial chain, supported versions/systems/architectures, reliability, bypassed exploit mitigations, default vs. non-default components, process continuation, etc).

New changes applied only for mobile platform and there is no changes in Desktops/Servers based zero-day exploit acquisition.

Zerodium takes one week and less to verify all submitted research. Once they confirm the then the payment will be initiated via various medium including bank transfer or cryptocurrencies such as Bitcoin or Monero.
You can also take Master in Bug Bounty course online to enhance your skill in Bub Bounty programs and ethically reporting the vulnerabilities.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and Hacking News update







