Sunday, October 18, 2026

ZeroFont Phishing: Hackers Manipulating Font Size to Bypass Office 365 Security

A new but ancient technique for Phishing emails has been recently identified called ZeroFont Phishing. Threat actors have followed several tactics for sending phishing emails, bypassing all the security mechanisms.

However, using this technique, threat actors could bypass Microsoft’s Natural Language Processing, which was acting as a Phishing email protection for Office users. 

Office 365 – Natural Language Processing

Microsoft has been working towards their way of securing its customers in all aspects. One of the major areas they focus on is phishing (Business Email Compromise) attacks, which have been the most used technique by threat actors for infiltrating organizations.

To prevent these phishing emails, Microsoft has been relying on Natural Language Processing, which scans the contents of an email for signs of impersonation or fraud. If an email content includes text like “© 2018 Microsoft Corporation. All rights reserved” and the email is not from Microsoft.com, Microsoft immediately flags this email as fraudulent.

This technique was also used to interpret email contents like banking information, user accounts, password resets, and financial requests and are checked for authenticity. However, threat actors bypassed this technique using the ZeroFont Phishing attack.

ZeroFont Phishing

The threat actor sends an email to the victim impersonating an Office 365 quota limit notification, which looks like an administrative service email. However, this phishing email bypassed the protection due to the use of the ZeroFont attack.

ZeroFont Phishing attack (Source: AVANAN)

Threat actors inserted random text inside the email, which had <span style=”FONT-SIZE: 0px”> for a zero font size, and broke up the text strings to bypass Microsoft’s natural language processing. 
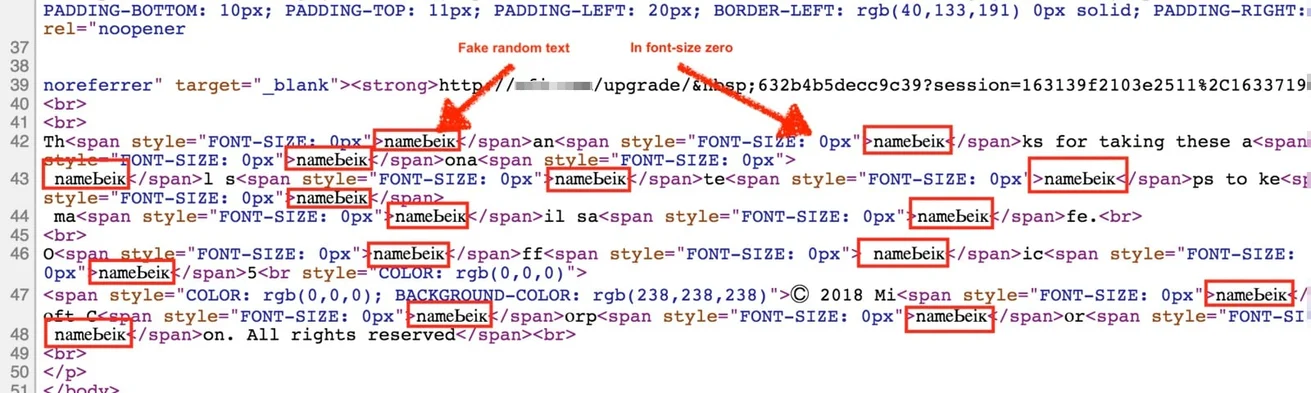
zerofont
Source: Avanan

A complete report has been published by Avanan, which provides detailed information about this attack and bypass scenarios used by threat actors. 

Protect yourself from vulnerabilities using Patch Manager Plus to quickly patch over 850 third-party applications. Take advantage of the free trial to ensure 100% security.

Eswar
Eswar
Eswar is a Cyber security content editor with a passion for creating captivating and informative content. With years of experience under his belt in Cyber Security, he is covering Cyber Security News, technology and other news.

Hot this week

How To Access Dark Web Anonymously and know its Secretive and Mysterious Activities

What is Deep Web The deep web, invisible web, or...

How to Build and Run a Security Operations Center (SOC Guide) – 2023

Today’s Cyber security operations center (CSOC) should have everything...

Russian Hackers Bypass EDR to Deliver a Weaponized TeamViewer Component

TeamViewer's popularity and remote access capabilities make it an...

Web Server Penetration Testing Checklist – 2026

Web server pentesting is performed under three significant categories: identity,...

ATM Penetration Testing – Advanced Testing Methods to Find The Vulnerabilities

ATM Penetration testing, Hackers have found different approaches to...

Hackers Use ConnectWise SkyKick Credentials to Access Microsoft 365, Halting Cloud Backups

Attackers abused compromised ConnectWise Cloud Backup credentials to access...

Anthropic’s Claude AI Uncovers Origins of NSA-Provided Cryptographic Keys After 25 Years

Anthropic says an internal Claude research model reconstructed how...

OpenBSD Kernel Flaw Dating Back 37 Years Enables Local Privilege Escalation to Root

A newly disclosed OpenBSD kernel exploitation chain combines a...

GhostAction Hackers Hide Credential-Stealing Malware in Fake Font Files Across 94 GitHub Repositories

GhostAction attackers have expanded their GitHub credential theft campaign...

SideCopy Hackers Target Indian Organizations With ReverseRAT Malware to Steal Data

Indian authorities have warned that SideCopy hackers are targeting...

New GhostBat Android Malware Targets 60 Banking and UPI Apps to Steal PINs

A new GhostBat RAT variant targets 60 Android financial...

New ROMULUS Malware Platform Uses Six Servers to Deliver Multiple Malicious Payloads

ROMULUS, a shared ClickFix delivery platform operating across six...

Related Articles

Recent News


