CISA has released a new tool for administrators and users to check for Citrix Application Delivery Controller (ADC) and Citrix Gateway vulnerability.
The vulnerability can be tracked as CVE-2019-19781, it allows an unauthenticated remote attacker to execute arbitrary code on the vulnerable system.
CISA has published a tool that allows users and administrators to check their Citrix Application Delivery Controller (ADC) and Citrix Gateway vulnerable to CVE-2019-19781.
The tool can be downloaded from GitHub, to execute it requires Python versions 3.6 and above.
To scan a host:
cve-2019-19781 citrix.example.org
If the system is vulnerable it shows the message as “2020-01-10 22:11:46,312 WARNING citrix.example.org appears to be vulnerable.”
The vulnerability was discovered in December, A couple of days before researchers spotted active scans targeting the vulnerability.
Citrix earlier released a security advisory detailing steps to mitigate the execution vulnerability.
Last weekend a group of security researchers published working exploit code for the vulnerability online. More details can be found here.
After the public release, there is a huge spike detected on honeypots, attackers started using public exploits to install backdoors.
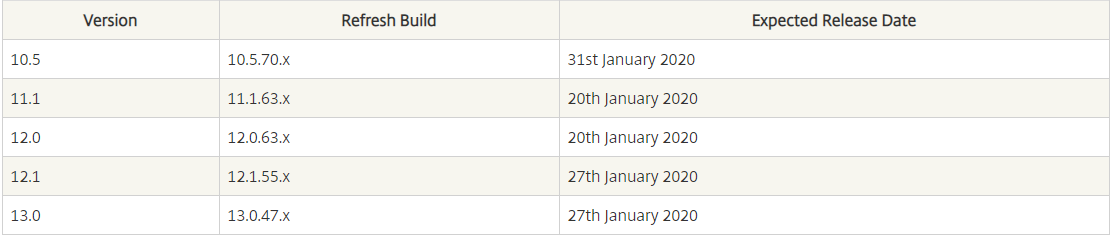
Citrix says that patch to be published with the end of January 2020, in the meantime users are strongly recommended to deploy a responder policy to mitigate the issue in the interim until a permanent fix is available.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates
Attackers abused compromised ConnectWise Cloud Backup credentials to access Microsoft 365 customer environments, prompting ConnectWise…
Anthropic says an internal Claude research model reconstructed how the National Security Agency generated seeds…
Two WordPress Core vulnerabilities can be chained to execute remote code without authentication, according to…
A newly disclosed OpenBSD kernel exploitation chain combines a shared memory accounting flaw with a…
GhostAction attackers have expanded their GitHub credential theft campaign with a second stage that disguises…
Indian authorities have warned that SideCopy hackers are targeting Indian organizations, including academic institutions, with…