Friday, November 6, 2026

Massive Hacking Campaign Targets WordPress Websites to Steal Database Credentials

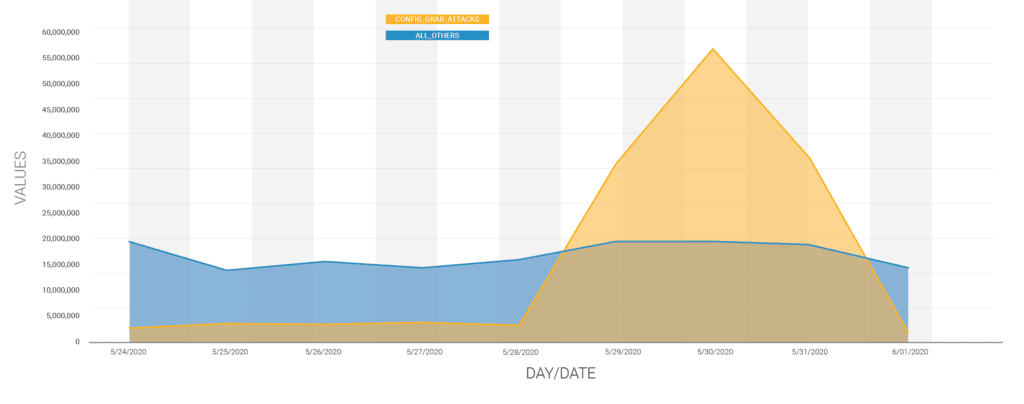
Cybercriminals launched more than 130 million attacks aiming to harvest database credentials from 1.3 million WordPress sites.

In this massive attack campaign, cybercriminals used several plugin and theme vulnerabilities across the WordPress ecosystem.

Security researchers from Wordfence observed the attack, the peak of the attack occurred on May 30, 2020.
Campaign Linked to Previous

Researchers were able to link the campaign with the same threat actor who previously targeting XSS vulnerabilities at a similar scale.

The previous campaign was conducted from 20,000 different IP addresses and the new campaign also using the same IP address.

All the attack targets older vulnerabilities in outdated plugins or themes that let attackers to download files or to export.

With this campaign the threat actor attempting to download wp-config.php file, which is the core that contains the website’s base configuration details, such as database-connection information.

The previous campaign targeted only XSS vulnerabilities whereas the new campaign targets number in outdated plugins or themes. But researchers believe both the attacks carried out by the same threat actor.

By downloading the file attackers can download database credentials and connection information that lets attackers gain access to the site’s database.

The database is the place where all the site contents such as usernames, passwords, posts, pages, and comments, even the website theme, and WordPress configuration settings.

If your website infected by this campaign you can find the entries “containing wp-config.php in the query string that returned a 200 response code,” reads Wordfence blog.

You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates

Gurubaran
Gurubaran
Gurubaran is a co-founder of Cyber Security News and GBHackers On Security. He has 10+ years of experience as a Security Consultant, Editor, and Analyst in cybersecurity, technology, and communications.

Hot this week

How To Access Dark Web Anonymously and know its Secretive and Mysterious Activities

What is Deep Web The deep web, invisible web, or...

How to Build and Run a Security Operations Center (SOC Guide) – 2023

Today’s Cyber security operations center (CSOC) should have everything...

Russian Hackers Bypass EDR to Deliver a Weaponized TeamViewer Component

TeamViewer's popularity and remote access capabilities make it an...

Web Server Penetration Testing Checklist – 2026

Web server pentesting is performed under three significant categories: identity,...

ATM Penetration Testing – Advanced Testing Methods to Find The Vulnerabilities

ATM Penetration testing, Hackers have found different approaches to...

Storm-2603 Hackers Exploit SharePoint and Abuse Cloudflare Tunnel to Hide Remote Access

A December intrusion to Storm-2603, the China-based group Microsoft...

New GhostMap Android Vulnerability Can Crash Phones Permanently Without Opening an App or Granting Permissions

Bitdefender researchers have revealed a vulnerability called GhostMap that...

ARTEX AI Framework Linked to Bank Breaches and Cloud Attacks Found Exposed Across Hundreds of Servers

An autonomous penetration-testing framework linked to South Korean banking...

OpenMatter Network Positions Decentralized Computing as an Alternative to Data Centers for AI

Melbourne, Florida, November 5th, 2026, CyberNewswire OpenMatter Network, a pioneer...

Related Articles

Recent News



