

The analysts of the Ben-Gurion University of Negev in Israel have detected a very unique way to spy on electronic conversations. The main initiative of finding this unique method was the TEMPEST Glowworm attack.
According to the report, this attack was targeting the speech of participants in a virtual meeting platform. The threat actors of this attack measure an audio output device’s LED power light that generally turns and transforms them into audio reproductions.
However, doing this generally allows the threat actors to have all the delicate conversations and know all the data that were being discussed in the meeting.
A modern and passive approach
According to the experts, the most active features of the Glowworm attack that makes it more powerful are its modernity and its passivity.
However, the approach for this attack needs no current signaling, as it would be resistant to any sort of electronic countermeasure movement.
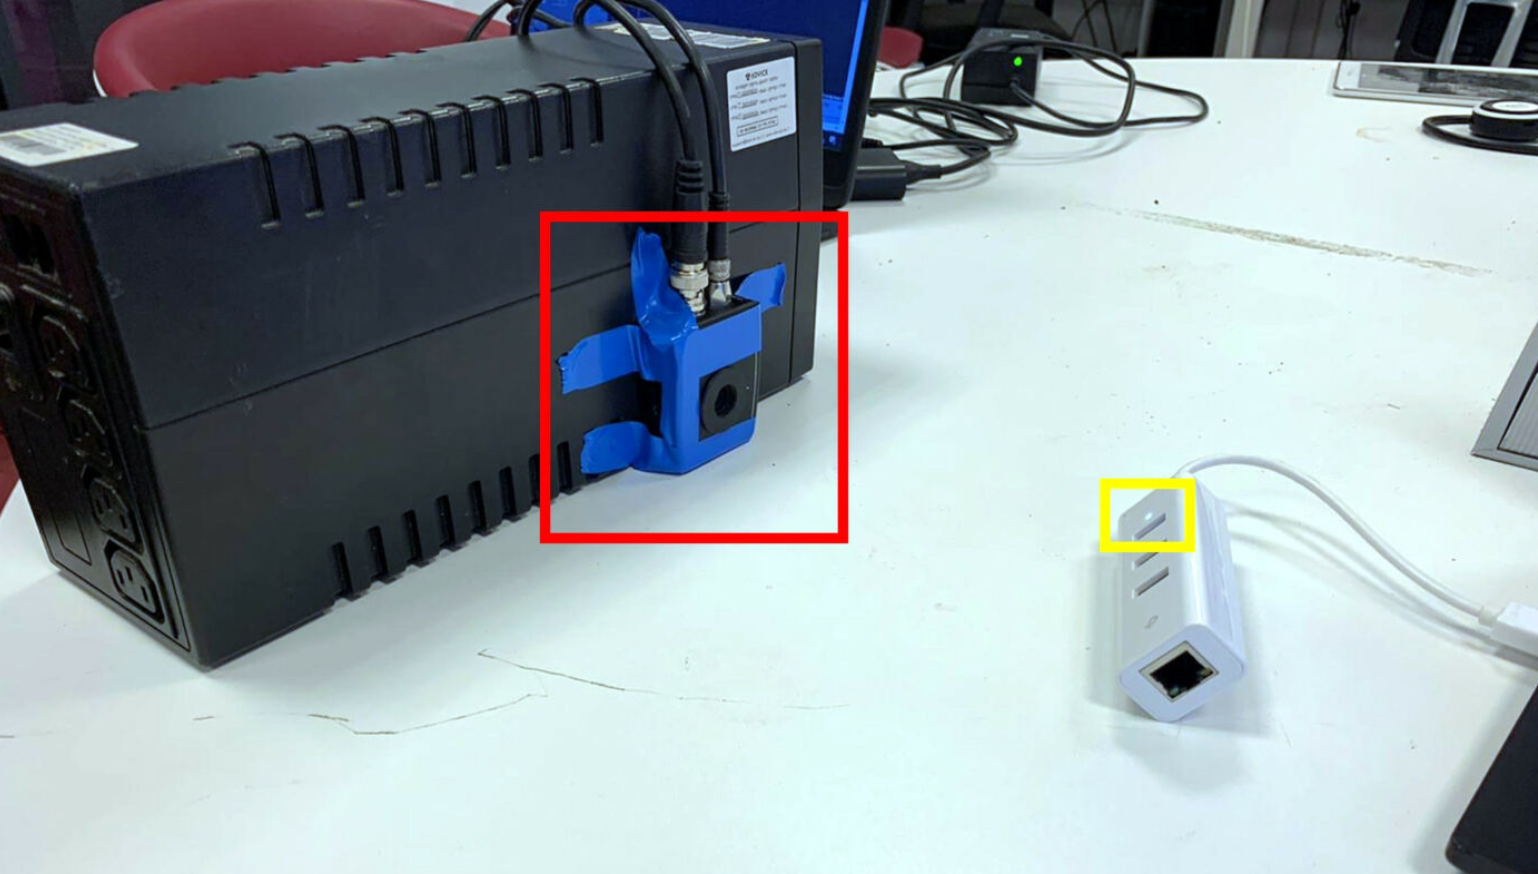
The attack has complete passivity and it differentiates it from comparable approaches like a laser microphone that can pick up audio from the fluctuations on a windowpane. The threat actors of Glowworm do not need any sudden signal leakage or any kind of intrusion.
It only requires “The Thing” well it was a Soviet gift to the US Ambassador in Moscow, and both needed “illumination” and that’s why it transmitted a clear signal while it was being illuminated.
Defense of Glowworm
However, we know that Glowworm has the ability to spy on the conversation without revealing itself, the main thing in this attack is that Glowworm doesn’t communicate with the actual audio, as it only depends upon the side effect of electronic devices that were producing audio during the meeting.
Glowworm has no real risk as it does not capture the audio of the one those who were present in the meeting room, the threat actor generally depends upon the remote participants whose voices are impersonated over the conference room audio system.
Glowworm Probation
After investigating the attack, the analysts have demonstrated the whole Glowworm experiment, this attack may work by designating a telescope with an electro-optical sensor from 35 meters away and along with speakers which are generally equated to the laptop.
0
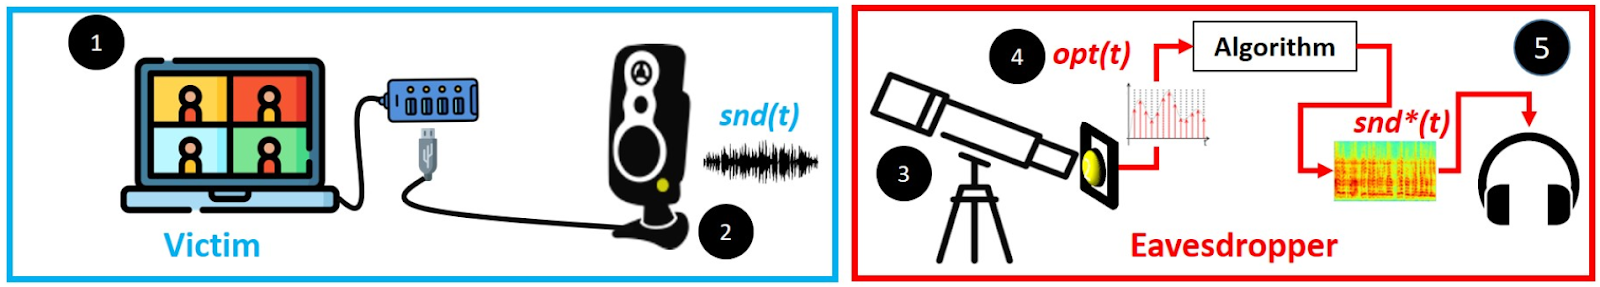
However, the team has successfully captured a statement that was being played on the speakers, and later it was rendered by Glowworm.
Most of the business that was being conducted over platforms like Skype is more sensitive enough and it is also difficult to attract eavesdroppers supplied with telescopes.
Glowworm Attack Demonstration
Apart from this, the security experts have found a way to stop this attack, however, it’s a unique method that will help to expose all the data which were being discussed in the meeting room.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.







