

Internet is being used worldwide, and it is one of the most valuable assets in today’s generation. However, recently, it was being revealed that a data exfiltration mechanism uses the Ethernet cables as a source of “transmitting antenna” to hijack all highly sensitive data from air-gapped systems.
Whenever this type of attack occurs, the risk of leakage of data increases as this attack involves stealing all the sensitive data of an organization.
After encountering such an attack, the organization generally moves to the air-gap isolation. Air-gapped computers are completely separated from external wide area networks (WAN) such as FTP, SSH, and SMTP.
The attack model
After investigating the attack, it was being detected that it comprises two main steps. And that’s why the major step that happens in this attack which makes it more dangerous, were mentioned below:-
- Reconnaissance and Infection
- Data Exfiltration
The data exfiltration is a part of the APT exfiltration phase, and in this, the threat actors the attacker might collect all the data from the compromised computers.
The data that is mostly hijacked by the threat actors can be:-
- Documents
- Databases
- Access credentials
- Encryption keys
It also has two parts, one is data transmission and another one is data reception, that we have mentioned below:-
Data transmission: In this part, after collecting all the data from the organizations the threat actors exfiltrate it just by using the covert channel.
Data reception: In this part, any nearby radio receiver can obtain the covert transmission, after that it simply decodes it and send it to the threat actors.
Virtual Machines (VMs)
The security analysts initially checked if the covert channel can be launched from within virtual machines or not. It’s known by everyone that virtualization has become a standard nowadays in many IT environments.
There are many features that make virtualization one of the standard methods, one property of visualization technologies is the isolation of hardware resources.
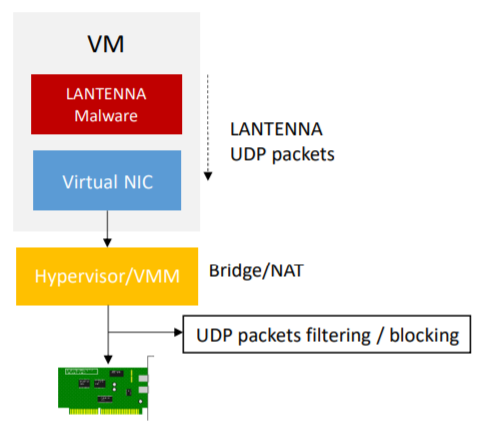
The architecture of virtual machine networking generally utilizes the idea of virtual network adapters, and it is maintained by the hypervisor and is being exposed to the customer through kernel drivers.
Recommendations
Apart from this, it’s been cleared that there are various defensive measures that can be taken against the LANTENNA covert channel, and they are:-
- Separation
- Detection
- Signal Monitoring
- Signal Jamming
- Cable Shielding
After encountering this attack, it’s been clear that the threat actors can exploit the Ethernet cables to exfiltrate data from air-gapped networks.
And they have estimated this covert channel in terms of bandwidth and distance and impersonated a set of countermeasures that we have mentioned above.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity, and hacking news updates.







