

The new ransomware group, LockBit, is targeting the VMware ESXi servers or virtual machines with their new Linux encryptor that is dubbed as “LockBit Linux-ESXi Locker version 1.0.”
Nowadays, companies and organizations are shifting their mode to cloud computing and virtual machines since they are easy to access and handle. While this mode of computing also allows them to do the following things easily as compared to the old school computing:-
- Save computer resources
- Consolidate servers
- Easier backups
Here, the shifting of companies is luring the ransomware groups more, and with time they are also evolving their TTPs and tools to compromise their targets.
As a new move, the new ransomware group, LockBit, has already initiated its work and targeted the VMware ESXi servers or virtual machines with its newly developed Linux encryptor.
LockBit Targets VMware ESXi servers
On the RAMP hacking forums, the operators of the LockBit ransomware group since October started promoting the features of Ransomware-as-a-Service operation and LockBit Linux-ESXi Locker.
While the cybersecurity researchers at Trend Micro have already examined the new Linux encryptor of LockBit, they concluded that operators of the LockBit group use their LockBit Linux-ESXi Locker to target the following products:-
- vCenter installations
- VMWare ESXi
However, similar type Linux encryptors are also used earlier by the threat actors or ransomware groups like:-
- HelloKitty
- BlackMatter
- REvil
- AvosLocker
- Hive ransomware
LockBit Linux-ESXi Locker: Capabilities & Commands
Here we have mentioned below all the capabilities that are offered by LockBit Linux-ESXi Locker:-
- Processor information
- Volumes in the system
- Virtual machines (VMs) for skipping
- Total files
- Total VMs
- Encrypted files
- Encrypted VMs
- Total encrypted size
- Time spent for encryption
In the below image, we have gathered all the commands used by the LockBit Linux-ESXi Locker with their respective description:-
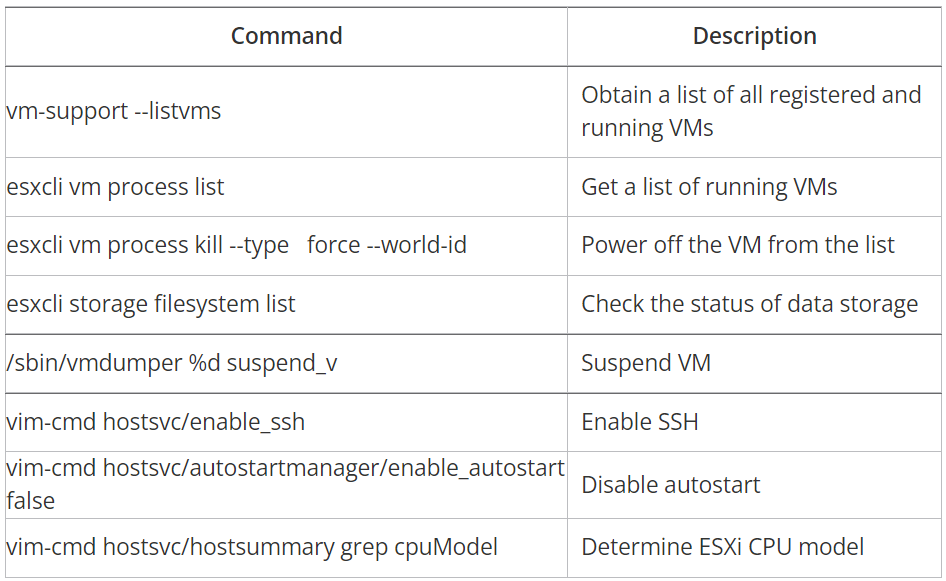
to encrypt the files and decryption keys, the Linux-ESXi Locker uses the following encryption method:-
- AES
- Elliptic-curve Cryptography (ECC) algorithms
That’s why the security analysts have urged admins and all security professionals to be ready to combat the ransomware groups like this with proper security defenses and plans.
Moreover, instead of the typical ransom note, the LockBit advertises the speed of LockBit 2.0, and not only that, but even the operators also list all the sites that they have attacked. Apart from this, they also lure their victims with millions of dollars lure and recruit them in dealings for access to the valuable data of the company.
Since the closure of the REvil ransomware group, the operators of LockBit ransomware have become the most prominent in the current scenario and with time also evolving their encryptors and abilities.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity updates






