

Researchers from Positive Security uncovered a website scanner called “Urlscan” that unintentionally leaking sensitive URLs and data due to misconfiguration.
It appears that a third party accidentally leaked the GitHub Pages URLs, and this incident happened while a metadata analysis was being conducted.
“This information could be used by spammers to collect email addresses and other personal information,” Bräunlein, Co Founder Positive security said. “It could be used by cyber criminals to take over accounts and run believable phishing campaigns.”
Urlscan.io
The URLscan.io service is described as a sandbox for the web and has been referred to as a web scanner. Several security solutions integrate with its API in order to make their solutions more secure and feature-rich.
The idea behind it is to allow users to identify possible malicious websites with ease and confidence using a simple, straightforward tool. A wide range of open-source projects and enterprise customers are supported by the engine.
Sensitive data can be mined
It was discovered that users who enabled Github Pages as a hosting method for a private repository leaked the name of the repository. There does not seem to have been any public official acknowledgment of this breach as of yet.
There is a possibility that an anonymous user could easily search for and retrieve a vast amount and variety of sensitive data within the API integration.
This is because the API is equipped with several varieties of security tools that run scans on incoming emails and conduct Urlscans on every link that is received.
Several types of information are provided with each scan result that is returned by the service, including:-
- Password reset links
- Unsubscribe links
- Account creation URLs
- API keys
- Information about Telegram bots
- DocuSign signing requests
- Amazon gift delivery links
- Shared Google Drive links
- Dropbox file transfers
- Invite links to SharePoint
- Invite links to Discord
- Government Zoom invites
- PayPal invoices
- Paypal money claim requests
- Links to Cisco Webex meeting recordings
- Package tracking links
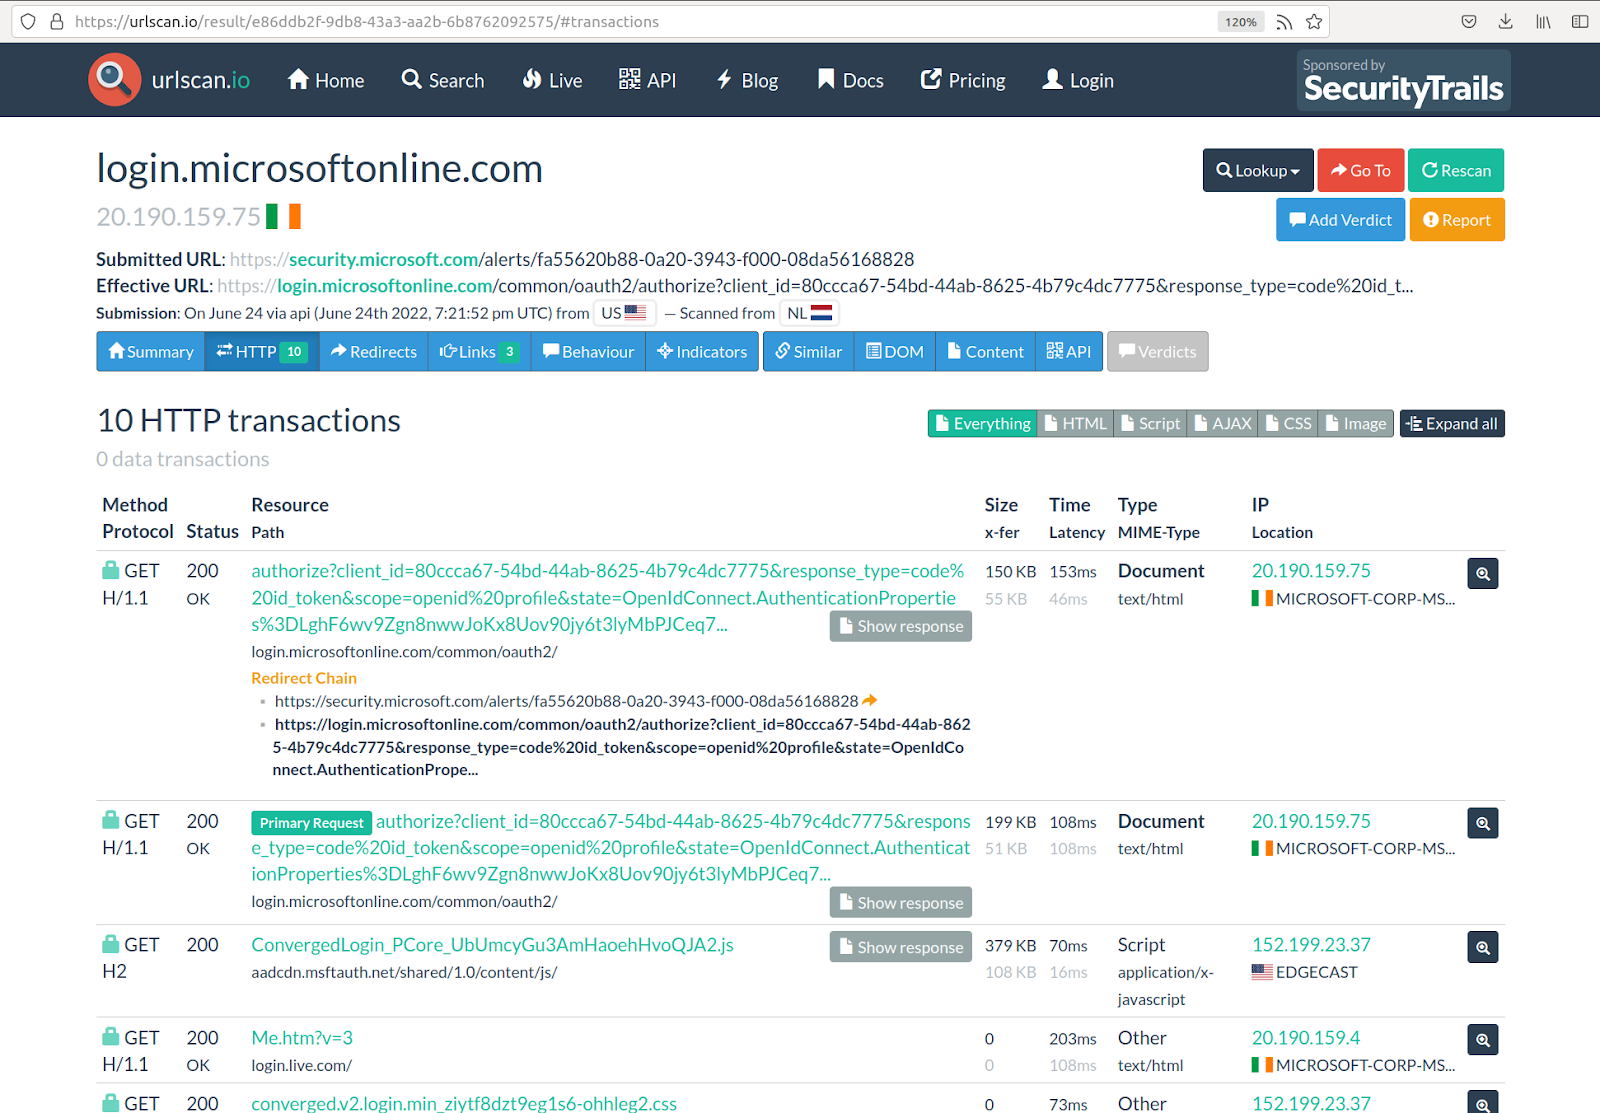
It has been noted that some API integrations use generic Python requests that use the python-requests/2.X.Y module. This would lead to scans being mistakenly submitted as public if user agents ignored account visibility settings.
Integrations
A list of 26 commercial security solutions have integrated urlscan.io’s API and the security solutions include are:-
- Tines – Advanced security orchestration & automation platform
- Palo Alto Networks Cortex XSOAR – Cortex XSOAR is the most comprehensive SOAR platform in the market today
- IBM Security SOAR – IBM Security SOAR Platform
- Cisco SecureX Threat Response – Security that works together
- Splunk SOAR – Security Automation & Orchestration Platform
- ThreatConnect – Threat Intelligence, Analytics, and Orchestration Platform
- Polarity – Augmented Reality for Your Desktop – Integration
- Maltego – A comprehensive tool for graphical link analyses
- Siemplify – Security Orchestration, Automation and Incident Response
- Swimlane – Security Orchestration, Automation and Response
- Anomali – A Threat Intelligence Platform that enables businesses to integrate security products and leverage threat data
- Exabeam – Smarter SIEM, Better Security
- Rapid7 Komand – An orchestration layer for security tools
- Rapid7 InsightConnect – Orchestration and automation to accelerate your teams and tools
- LogicHub – Intelligent Security Automation
- FireEye Security Orchestrator – Simplify threat response through orchestration and automation
- RSA NetWitness – Threat detection & response
- Cybersponse – Security Orchestration, Automation and Incident Response Solution
- ArcSight Enterprise Security Manager (ESM) – Powerful, adaptable SIEM that delivers real-time threat detection and native SOAR technology.
- FortiSOAR – FortiSOAR is a security orchestration, automation, and response (SOAR) solution.
- Metaspike Forensic Email Intelligence – Experts’ choice for investigating email fraud, business email compromise (BEC), malware delivery, and CAN-SPAM Act violations.
- Nevelex Labs – Security Flow is a new automation and orchestration tool for corporate security.
- Sanguine eComscan – eComscan is smart CCTV for online stores
- D3 SOAR – Security Orchestration and Automated Incident Response with MITRE ATT&CK
- DTonomy AIR – SOAR with Adaptive Intelligence
- Joe Sandbox Cloud – Automated Deep Malware Analysis in the Cloud for Malware
- Hybrid Analysis – Free malware analysis service for the community that detects and analyzes unknown threats
There are probably many more enterprise customers missing from this list, including GitHub, which uses this API directly within its SaaS offering.
Impact
Several URLs found by the company also contained publicly-shared links to iCloud files, and some belonged to Apple domains. This has now been corrected and taken down.
In response to Positive Security’s request for contact and the leaked email addresses, an unknown organization responded back to them.
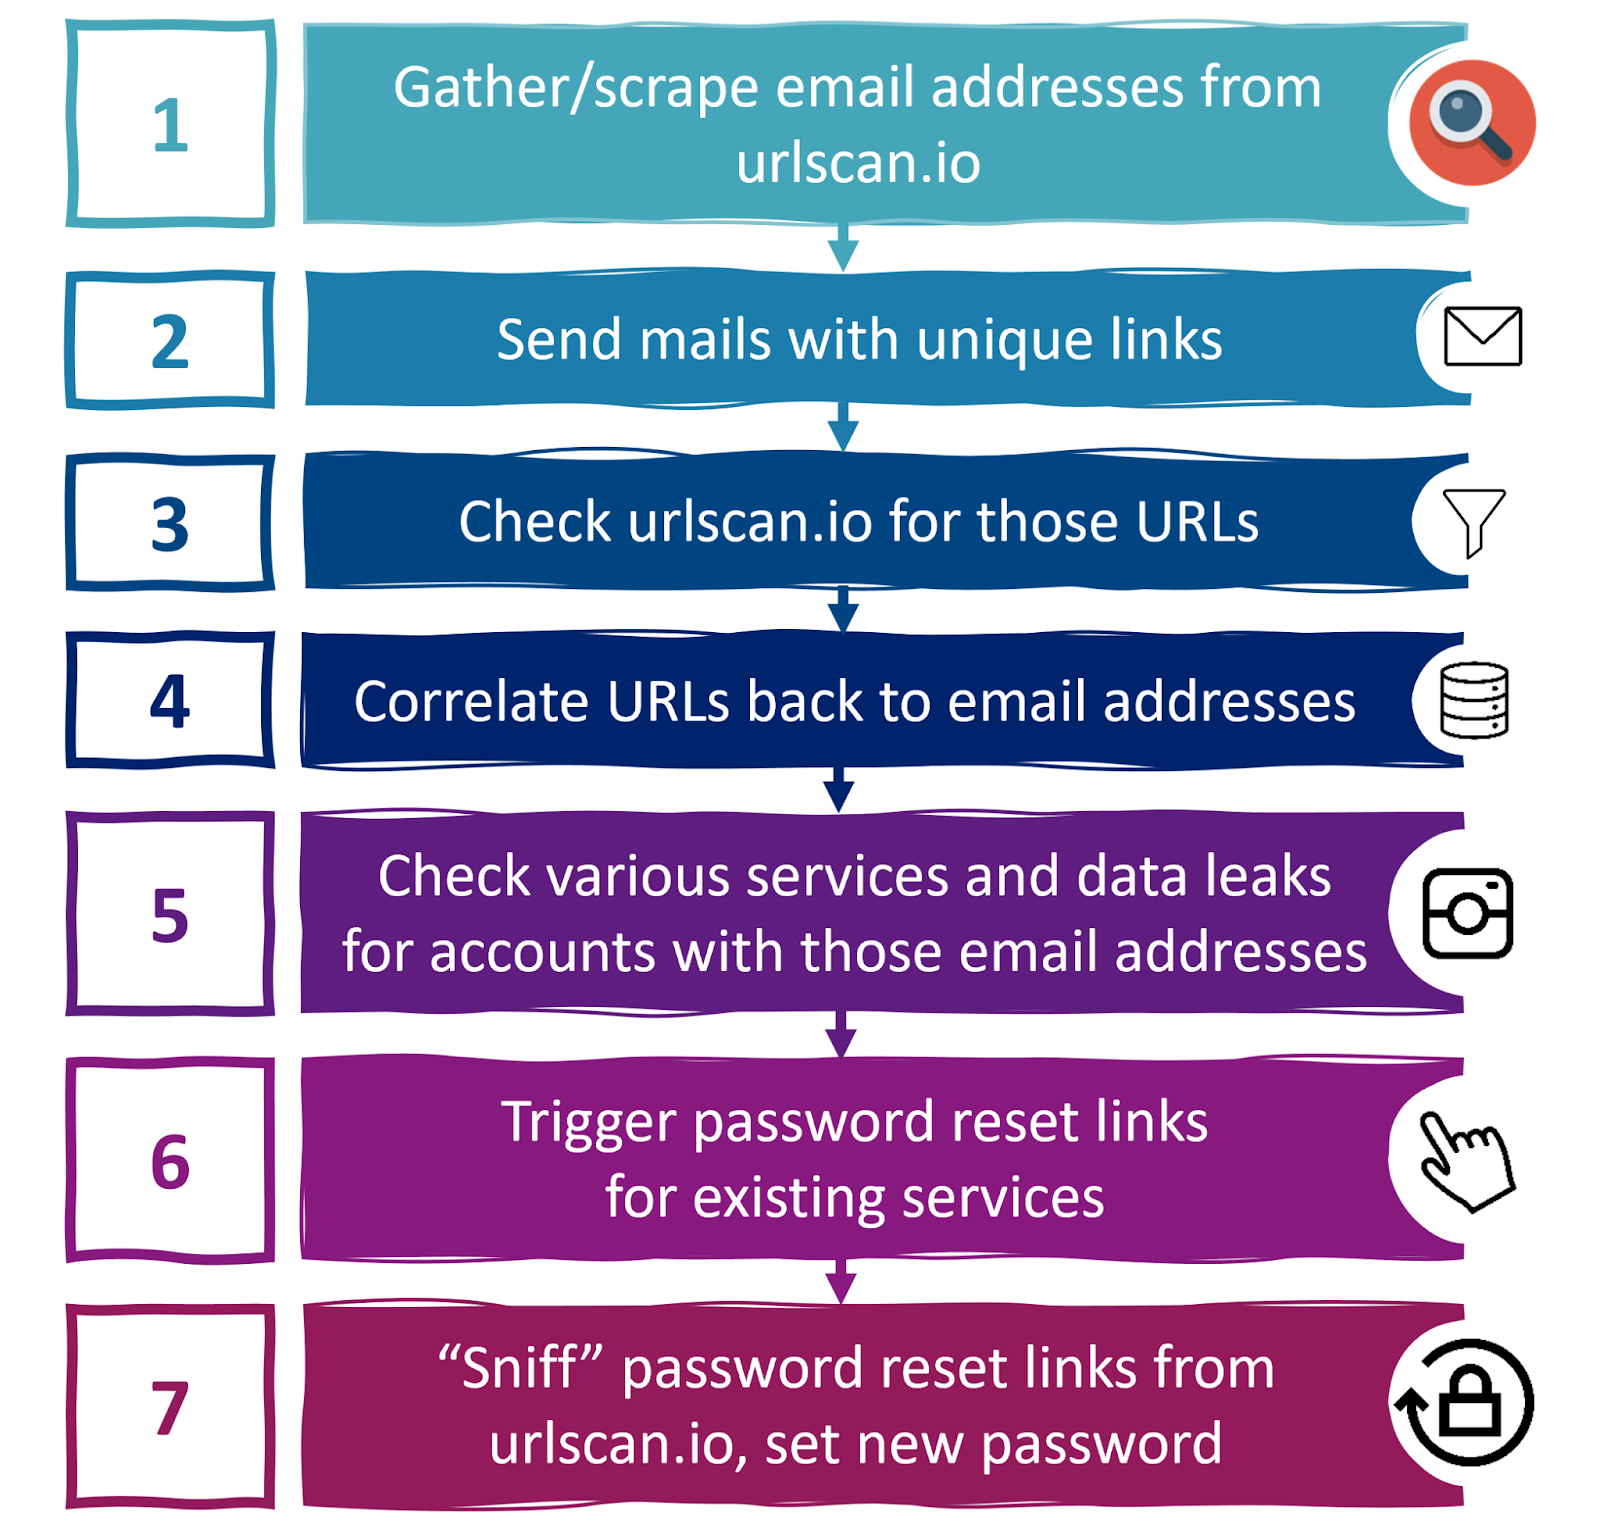
Apparently, the leak was caused by the misconfiguration of Urlscan.io’s SOAR solution which was integrated with a work contract link in a DocuSign contract.
Positive Security informed Urlscan.io in July about its findings after completing its complete assessment. While they did so in cooperation with Urlscan.io’s developers and found a solution to resolve the flaw.
As a result, an enhanced scan visibility interface and team-wide visibility settings were introduced with the release of a new engine version in the following month.
Network Security Checklist – Download Free E-Book







