

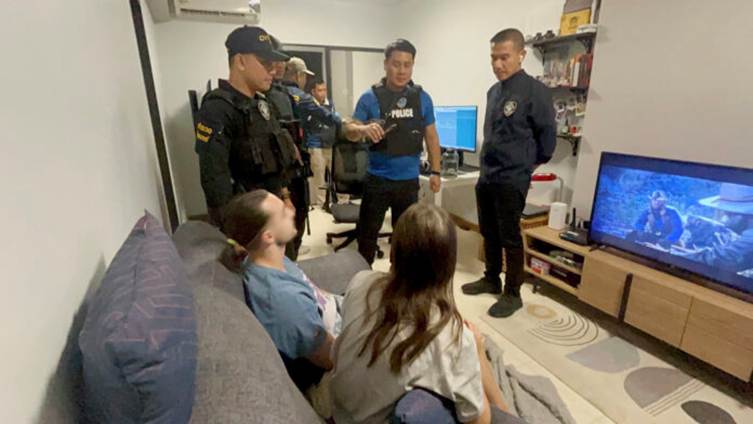
Thai authorities arrested four European hackers in Phuket on February 10, 2025, for their alleged involvement in ransomware operations that inflicted global losses exceeding $16 million.
The arrests, part of the multinational “Operation PHOBOS AETOR,” were executed in collaboration with Swiss and U.S. law enforcement agencies.
The suspects, two men, and two women were apprehended during coordinated raids at four locations: Mono Soi Palai, Supalai Palm Spring, Supalai Vista Phuket, and Phyll Phuket x Phuketique Phyll. Police confiscated over 40 digital devices, including mobile phones, laptops, and cryptocurrency wallets, which were allegedly used in criminal activities.
Operation PHOBOS AETOR
Ransomware Operation on a Global Scale
As per a report by Khao Sod English report, the operation targeted an international cybercrime group responsible for deploying the Phobos ransomware.
Between April 2023 and October 2024, the group reportedly attacked 17 companies in Switzerland, as well as numerous other organizations worldwide.
Using sophisticated cyber techniques, the hackers gained unauthorized access to networks, and encrypted data, and demanded substantial cryptocurrency ransoms for decryption keys.
Victims who refused to pay were threatened with public exposure of sensitive data.
Additionally, the hackers employed cryptocurrency mixing services to obscure their transactions and evade detection, making their digital trail nearly untraceable.
The operation affected over 1,000 victims globally, with damages estimated at $16 million (approximately 560 million baht).
This high-profile arrest highlights the importance of international cooperation in combating cybercrime.
Acting on an urgent request from Swiss and U.S. authorities, Thai officers from the Cyber Crime Investigation Bureau (CCIB), led by Police Lieutenant General Trairong Phiwphan, executed the raids alongside Immigration Police and Region 8 Police.
The suspects wanted on Interpol warrants, were found to be part of a transnational criminal organization.
The suspects face charges of Conspiracy to Commit an Offense Against the United States and Conspiracy to Commit Wire Fraud.
While their identities remain undisclosed, evidence collected during the arrests is expected to be critical in advancing investigations.
Ransomware attacks have become a significant global threat, targeting businesses, institutions, and individuals alike.
The takedown of this operation underscores the increasing need for law enforcement agencies worldwide to collaborate in addressing the growing sophistication of cybercriminals.
Are you from SOC/DFIR Team? - Join 500,000+ Researchers to Analyze Cyber Threats with ANY.RUN Sandbox - Try for Free







