

Kali Linux 2020.1 released with new tools, improvements to theme & kali-undercover, adds Non-Root by default and Kali single installer image.
With the release as previously announced, Kali Linux moved to a traditional default non-root user and also announced NetHunter Rootless Edition.
Kali Linux 2020.1
Earlier this year kali Linux team at Offensive Security announced the move to the “traditional default non-root user” model, now the changes to effect with version 2020.1.
Earlier kali inherited the default root policy from its predecessors, starting from Kali 2020.1 there is no longer a superuser account and default user now is a standard, unprivileged, user.
The change was made due to security reasons, so no more root/toor it should be kali/kali.
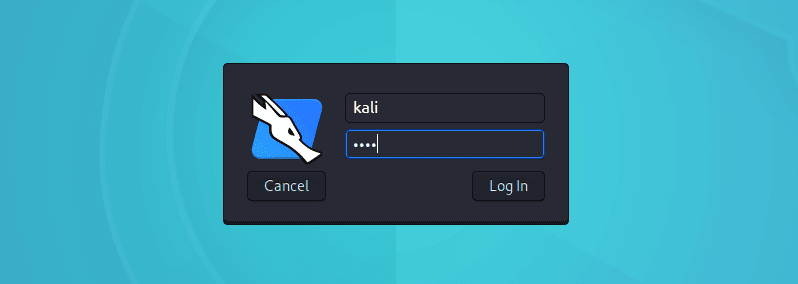
Another notable change is the Single Installer Image, Kali no longer offer images for every desktop environment (DE). Instead, they now provide a single image and ask you to select your desktop environment.
The new edition also lets users select the tools to be included with the installation. To install a custom image except for Xfce and default packages, it requires an Internet connection.

With the Installer image, the live mode is not included, if you want to use live mode then you need to have a live image.
ARM images for 2020.1 continue to run as root by default and the Pinebook Pro isn’t included in the 2020.1 release, “We are still working on getting it added, and as soon as it is ready we will post it.”
NetHunter Rootless
The mobile pentesting platform also comes with new improvements, one of the major changes is that you no longer required to root your phone to run Kali NetHunter.
Here are the three NetHunter editions
- NetHunter – Needs rooted devices with custom recovery and patched kernel. Has no restrictions. Device-specific images are available here.
- NetHunter Light – Needs rooted devices with custom recovery but no custom kernel. Has minor restrictions, i.e. no WiFi injection or HID support. Architecture specific images are available here.
- NetHunter Rootless – Installable on all stock standard, unmodified devices using Termux. Some limitations, like lack of db support in Metasploit and no root permissions. Installation instruction is available here.
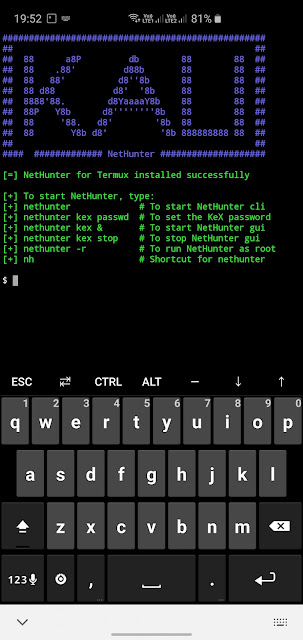
With the NetHunter Rootless, the non-root user also has full privileges in the chroot due to how proot containers work.
Theming & Kali-Undercover
New themes included for Gnome users, it includes both the light and the dark versions. Icons used in the menu also replaced.
Enhancements did with Kali-Undercover mode to make it feel even more like using a Windows operating system.

New Packages & Python 2
New tools such as cloud-enum, emailharvester, phpggc, sherlock, splinter are added and few existing tools were upgraded.
As Python 2 reached the end of life on the 1st of January 2020, the tools that developed based on Python 2 are removed.
Existing users can upgrade to the new version and the fresh images can be downloaded from here.
You are also recommended reviewing our Kali Linux Tutorials page which covers dozens of Kali Linux Tools. Also, Learn The Complete Kali Tools in Kali Linux Operating System.







