Sunday, October 18, 2026

Kali Linux 2020.1a Released – Download Updated Kali Image for Raspberry Pi

World’s leading Penetration distribution Kali Linux 2020.1a released with some of the major changes in the installer which makes the installation process easier for users.

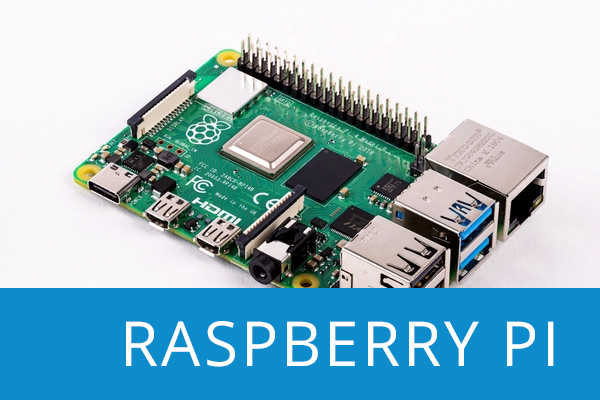
Kali Linux also issued a new updated image for Raspberry Pi, both 32-bit & 64-bit for Raspberry Pi and the file corruption bug has been fixed that affected in an earlier version.
In the earlier versions of Kali 2020.1, Offensive security changed the base images without having multiple different ISOs for each DE, by introducing an “installer” image as well as a “live” image.

According to Kali Linux 2020.1a update, “The “installer” image is the new one, as this uses “debian-cd” on the back-end. We noticed a bug in a dependency chain, which caused an issue with x11. As a result, you may not have got a graphical interface after installing Kali. As a result, we pushed out a fix (2020.1a) to address this.”

With the Kali Linux 2020.1 traditional default non-root user” has been introduced, so there is no longer a superuser account and default user now is a standard.

With the Kali Linux 2020.1 default, the user has been switched to kali with the vagrant image as well. A Vagrant is a tool for building and managing virtual machine environments in a single workflow.

Now for the vagrant images, the update has been reverted, you can also use the KaliLinux on a PineBook Pro.

Also, Kali Linux 2020.1a is only for users who haven’t successfully installed the 2020.1, If you are already running 2020.1, you do not need to reinstall.

New version of Kali Linux 2020.1a can be downloaded from here.

You are also recommended reviewing our Kali Linux Tutorials page which covers dozens of Kali Linux Tools. Also, Learn The Complete Kali Tools in Kali Linux Operating System.

Balaji
Balaji
BALAJI is an Ex-Security Researcher (Threat Research Labs) at Comodo Cybersecurity. Editor-in-Chief & Co-Founder - Cyber Security News & GBHackers On Security.

Hot this week

How To Access Dark Web Anonymously and know its Secretive and Mysterious Activities

What is Deep Web The deep web, invisible web, or...

How to Build and Run a Security Operations Center (SOC Guide) – 2023

Today’s Cyber security operations center (CSOC) should have everything...

Russian Hackers Bypass EDR to Deliver a Weaponized TeamViewer Component

TeamViewer's popularity and remote access capabilities make it an...

Web Server Penetration Testing Checklist – 2026

Web server pentesting is performed under three significant categories: identity,...

ATM Penetration Testing – Advanced Testing Methods to Find The Vulnerabilities

ATM Penetration testing, Hackers have found different approaches to...

Hackers Use ConnectWise SkyKick Credentials to Access Microsoft 365, Halting Cloud Backups

Attackers abused compromised ConnectWise Cloud Backup credentials to access...

Anthropic’s Claude AI Uncovers Origins of NSA-Provided Cryptographic Keys After 25 Years

Anthropic says an internal Claude research model reconstructed how...

OpenBSD Kernel Flaw Dating Back 37 Years Enables Local Privilege Escalation to Root

A newly disclosed OpenBSD kernel exploitation chain combines a...

GhostAction Hackers Hide Credential-Stealing Malware in Fake Font Files Across 94 GitHub Repositories

GhostAction attackers have expanded their GitHub credential theft campaign...

SideCopy Hackers Target Indian Organizations With ReverseRAT Malware to Steal Data

Indian authorities have warned that SideCopy hackers are targeting...

New GhostBat Android Malware Targets 60 Banking and UPI Apps to Steal PINs

A new GhostBat RAT variant targets 60 Android financial...

New ROMULUS Malware Platform Uses Six Servers to Deliver Multiple Malicious Payloads

ROMULUS, a shared ClickFix delivery platform operating across six...

Related Articles

Recent News


