

Recently, a hackers group, known as RATicate has abused the NSIS (Nullsoft Scriptable Install System) installers to deploy RATs (Remote Access Tools) and information-stealing malware to launch several waves of attacks on industrial companies, stated the security researchers at Sophos.
Due to the deadly COVID-19 pandemic, cyber attackers are constantly targeting the organizations to loot their confidential data for monetary benefits.
As a chain of five separate cyberattack campaigns between November 2019 and January 2020, the hackers’ group RATicate had specifically targetted all the European, the Middle East, and the South Korean industrial companies.

Here the most shocking thing is that the security experts at Sophos have suspected that in the past, this hacker group is also behind other similar campaigns as well.
Moreover, a threat researcher with SophosLabs, Markel Picado, said that “A new campaign we believe connected to the same actors leverages concern about the global COVID-19 pandemic to convince victims to open the payloads.”
Infection in NSIS installer
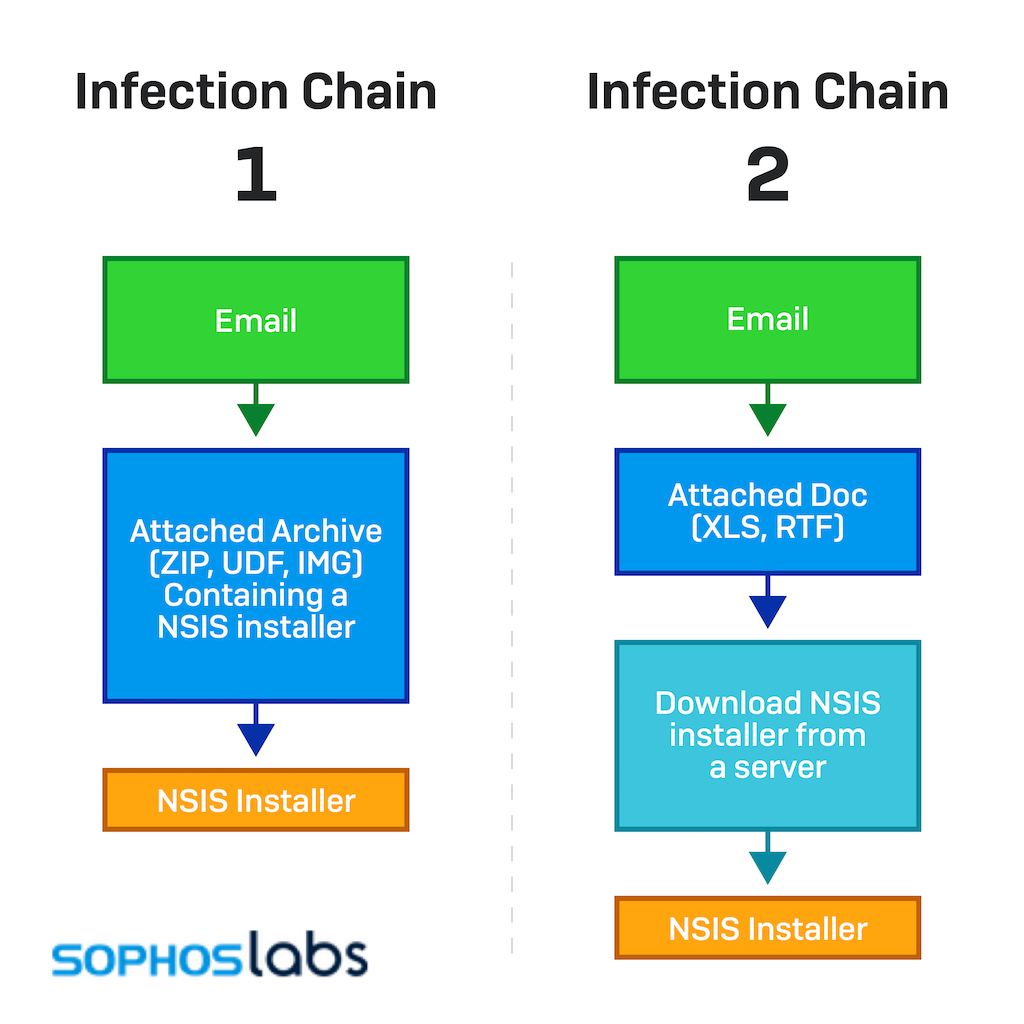
To deliver the payloads via phishing emails with trivial modifications to fool the targets, the hackers use two infection chains to contaminate the targets’ systems.
The campaign uses the NSIS installer after the target opens the documents attached in those phishing emails sent by the attackers with the common extensions like “.ZIP, .IMG, .UDF, .RTF, and .XLS files.”
Don’t know, what is the NSIS installer? It’s is an open-source tool that is backed by Nullsoft for creating Windows installers, and not only that, it’s the tool that is densely used to cover and deploy malware by hackers.
Hackers use the ZIP, UDF, and IMG malicious attachments in which they hide the malicious NSIS installers in the first infection chain.
Moreover, to download the malicious installers from a remote server into the targets’ systems, the hackers use the XLS and RTF malicious documents in the second infection chain.

Apart from this, the security experts at Sophos has explained that “We considered two possible scenarios: either the malicious NSIS package is a generic packer sold on dark forums; or, the same threat actor is using a custom loader to deploy different payloads in a variety of their attacks.”
To be able to communicate with multiple software components, the NSIS installers use a specialized type of plugin architecture that gives the possibilities to kill processes, execute command line-based programs, loading DLL files, and much more.
Targeting and Motivation
According to the Sophos reports and these campaigns, the security experts have clarified that the intention of the attackers is only to gain full access and control of the systems on the targeted companies’ networks.
Moreover, from the emails that were sent by these campaigns, the security experts have recognized the targeted victims, and here they are:-
- An electrical equipment manufacturer in Romania;
- A Kuwaiti construction services and engineering company;
- A Korean internet company;
- A Korean investment firm;
- A British building supply manufacturer;
- A Korean medical news publication;
- A Korean telecommunications and electrical cable manufacturer;
- A Swiss publishing equipment manufacturer;
- A Japanese courier and transportation company.
As final payload-all of them InfoStealer or RAT malware, the attackers used five different types of malware families that were discovered by the security firm, Sophos.
- ForeIT/Lokibot
- BetaBot
- Formbook
- AgentTesla
- Netwire
Even the security experts have also stated that the new wave of attacks of the RATicate group that were detected in March 2020 clearly indicates that to trick the potential victims into installing malware on their systems, they are using next-level tricks and exploits, including the COVID-19 related baits as well.
So, what do you think about this? Simply share all your views and thoughts in the comment section below.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.
Also Read:
Hackers Using InfoStealer Malware that Attacks Windows Servers To Steal Sensitive Data
Hackers Hijack Home Routers & Change The DNS Settings to Implant Infostealer Malware
Hackers Spreading Zeus Sphinx Malware to Hijack Windows Process Using Malformed MS Word Documents
Chinese Hacking group ‘Thrip’ Targets Satellite communications, Telecoms, and Defense Companies







 installers to deploy RATs (Remote Access Tools))