

Recently, the representatives of the ETERBASE has reported on the official Telegram channel of the portal that they have become a victim of hackers. In this incident, the hackers attacked ETERBASE and successfully stole $5.4 million on September 8.
ETERBASE already issued the addresses of the wallets to which the funds were transferred. Here, hackers have hacked six hot wallets that contain Bitcoins, Ether, ERC20 tokens, XRP, Tron, Tezos, and Algorand.
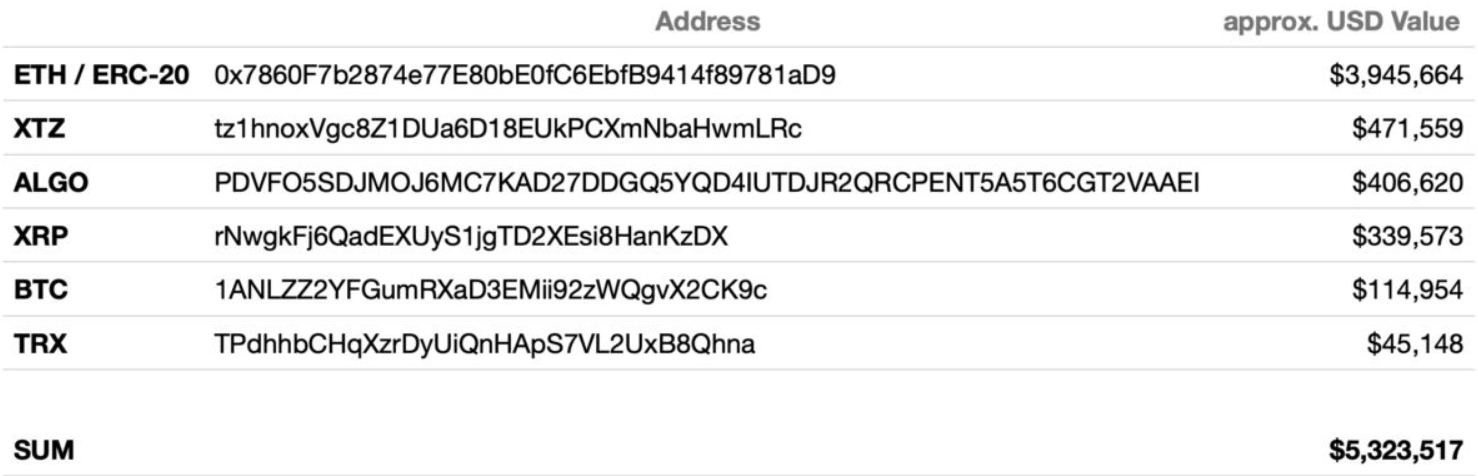
However, the representatives of ETERBASE has already informed the police about the event, and they have already initiated their investigation. According to the reports, the hefty part of the funds went to the popular exchanges, Binance, HuobiGlobal, and Hitbtc.
According to ETERBASE report, as we have informed our customers/community yesterday, the hot wallets of the ETERBASE Exchange were compromised and assets worth approximately $ 5.4 million were stolen.
In the official Telegram channel, the representatives of ETERBASE admitted that they noticed the attack, but, unfortunately, they were not able to stop it. But, the company has already requested assistance from the other exchanges to which the funds were transferred.
But on September 9, ETERBASE reassured that it had enough capital available to cover the payouts of all users, and not only that, even they have also ensured that it had no intention to stop its operations.
Moreover, the CEO of Binance, Changpeng Zhao, has assured that he will do everything in his power to help ETERBASE to recover the funds. The cryptocurrency exchanges are often used to launder money by ransomware operators, and Binance was unable to prevent hackers from withdrawing funds through their infrastructure.
Security experts have hinted towards the Cybercriminal group CryptoCore, as this group is behind many attacks on cryptocurrency exchanges.
This group has been operating since 2018 and has already carried out five cyberattacks, as a result of which about $200 million were stolen from online cryptocurrency exchanges in Japan, the United States, and other countries.
Due to this breach, currently, all the operations on Eterbase are suspended until September 10, but as we told earlier that the company has assured that they will continue all their operations.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity updates
Also Read:
Hackers Abusing Docker Hub Account to Mine Monero Cryptocurrency
Hackers Сovertly Mining Cryptocurrency on Government Websites in India







