

Microsoft security researchers have continued to investigate Solorigate which caused supply chain compromise and the subsequent compromise of cloud assets and have said that the ultimate ambition of the compromise was to pivot to the victims’ cloud assets after deploying the Sunburst/Solorigate backdoor on their local networks.
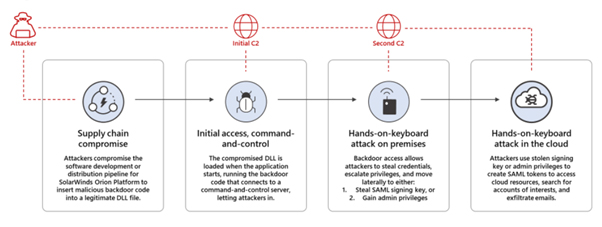
What is Solorigate attack chain?
The Solorigate attack features a sophisticated technique involving a software supply chain compromise that allowed attackers to introduce malicious code into signed binaries on the SolarWinds Orion Platform, a popular IT management software.
The compromised application grants attackers “free” and easy deployment across a wide range of organizations who use and regularly update the application, with little risk of detection because the signed application and binaries are common and are considered trusted.
Target on Cloud Assets
Microsoft mentioned that the target has clearly set on Cloud now.
‘With this initial widespread foothold, the attackers can then pick and choose the specific organizations they want to continue operating within (while others remain an option at any point as long as the backdoor is installed and undetected’
Anticipations as per investigation
Based on the investigations, the next stages of the attack involves on-premises activity with the goal of off-premises access to cloud resources
- The compromised SolarWinds DLL is used to activate a backdoor which enables attackers to remotely control and operate the affected device.
- The backdoor access is then used to steal credentials, escalate privileges, and move laterally to gain the ability to create valid SAML tokens using either one of the below mentioned methods:
- Stealing the SAML singing certificate
- Adding to or modifying existing federation trust
- Then the attacker created SAML tokens to access the cloud resources and perform actions leading to the exfiltration of emails and persistence in the cloud.
Research and mitigation
Many tests, detection and remediation steps are also proposed specially for Endpoint, detecting hands on keyboard activity within on premise environment and cloud enviiroment, Identifying unusual addition of credentials to an OAuth app, Discovering malicious access to mail items, detecting and blocking backdoor activities, etc and thereby shared mitigation measures against unauthorized cloud access making it difficult for threat actors to gain access.
Much clear visibility about the attack chains and related threat intelligence is analysed as early as possible so organizations can identify and take action to stop this attack, understand the potential scope of its impact, and begin the recovery process from this active threat.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity, and hacking news updates.







