

Zyxel Communications Corp. is a manufacturer of networking devices. It is popular for firewalls that are marketed towards small and medium businesses. Their Unified Security Gateway (USG) product line is often used as a firewall or VPN gateway.
The secret backdoor found installed in Zyxel firewall and VPN was discovered by a team of Dutch security researchers from Eye Control.
The Flaw
The flaw, tracked as CVE-2020-29583 (CVSS score 7.8), affects version 4.60 present in wide-range of Zyxel devices, including Unified Security Gateway (USG), USG FLEX, ATP, and VPN firewall products.
According to the advisory published by Zyxel, firmware version 4.60 of Zyxel USG devices contains an undocumented account (“zyfwp”) comes with an unchangeable password. The password for this account can be found in cleartext in the firmware. This account can be exploited by the attackers to login to the ssh server or web interface with admin privileges.
Detecting Vulnerability
According to the researchers, the account uses the “zyfwp” username and the “PrOw!aN_fXp” password. The plaintext password was visible in one of the binaries on the system.
This account seemed to work on both the SSH and web interface. As SSL VPN on these devices operates on the same port as the web interface, a lot of users have exposed port 443 of these devices to the internet.
Javascript and CSS files were requested from the web interface of these devices and found that approximately 10% of devices are running the affected firmware version in the Netherlands.
In this case, an attacker could completely compromise the confidentiality, integrity and availability of the device. For example, the attacker can change firewall settings to allow or block certain traffic. They can also intercept traffic or create VPN accounts to gain access to the network behind the device.
The Affected Product Series and Patch Available
EYE researcher Niels Teusink reported the vulnerability to Zyxel on November 29, following which the company released a firmware patch available.
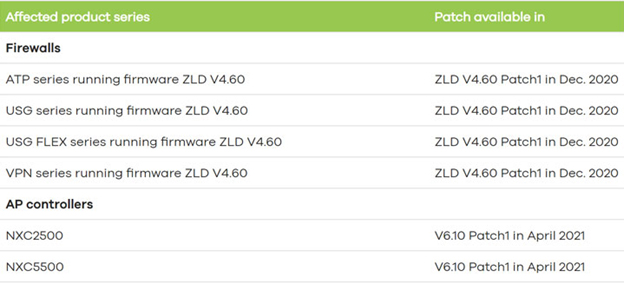
The company is expected to address the issue in its Access Point (AP) controllers with a V6.10 Patch1 that is set to be released in April 2021.
Final Word
The new Zyxel backdoor could expose a whole new set of companies and government agencies to the same type of attacks seen over the past two years.
The researchers extremely recommend the users to install the updated firmware as soon as possible to mitigate the risk associated with the flaw.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity, and hacking news updates.
Also Read







