Sunday, October 18, 2026

Domestic Kitten – Extensive Surveillance Operation Against Iranian citizens

Researchers have studied and analyzed the workings of the hacking group Domestic Kitten. Domestic Kitten also goes by the name APT-50, and has been accused of deceiving people by having them install spyware on their mobile devices and PCs’.

The attacks were targeted against residents of 12 countries, including those of the UK, and USA. The installed spyware was being used to steal call recordings and media files from the victims’ devices.

Domestic Kitten was tricking people into downloading its spyware by:

  1. repackaging an existing version of an authentic video game found on the Google Play store
  2. mimicking an app for a restaurant in Tehran
  3. providing a compromised app that publishes articles from a local news agency
  4. offering a fake mobile-security app
  5. supplying an infected wallpaper app containing pro-Islamic State imagery 
  6. masquerading as an Android application store to download further software
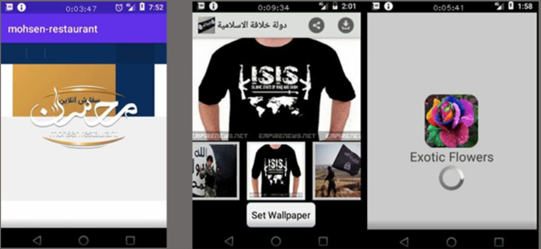
FurBall Repacked ‘Exotic Flowers’ cover, and an ISIS supported cover

It is believed that Domestic Kitten has been running this campaign at least for the past 4 years and that no less than 1200 individuals have been targeted and attacked.

CampaignStartEnd
hass44136Currently active
or4395243983
mat4380044013
hj4358643922
oth43252Currently active
hr4300943040
maj4300943617
mmh42917Currently active
msd42887Currently active
grt4288743709
Domestic Kitten Campaign list

The APT uses a mobile malware that is called FurBall. FurBall is transmitted via a variety of methods including phishing, Telegram channels, SMS messages containing a link to the malware, and Iranian websites.

Once FurBall is installed on the targeted device it intercepts SMS messages, grabs call logs, gathers device information, records communication, steals and stores media and files, monitors the device’s GPS coordinates, and many such activities.

Once the device has been compromised, it collates the data and is sent to command-and-control (C2) servers under Domestic Kitten’s usage since 2018.

Linked IP addresses were traced back to the Iranian cities of Tehran and Karaj. Another group that goes by the name of Infy too has been identified. This group targets users’ PCs’ and not their mobile devices. This group is believed to be state-sponsored and is in existence since 2007.

You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.

Also Read

Fox Kitten – Iranian Malware Campaign Exploiting Vulnerable VPN Servers To Hack The Organizations Internal Networks

Charming Kitten APT Hackers Group Abusing Google Services to Attack U.S Presidential Campaign Members

Gurubaran
Gurubaran
Gurubaran is a co-founder of Cyber Security News and GBHackers On Security. He has 10+ years of experience as a Security Consultant, Editor, and Analyst in cybersecurity, technology, and communications.

Hot this week

How To Access Dark Web Anonymously and know its Secretive and Mysterious Activities

What is Deep Web The deep web, invisible web, or...

How to Build and Run a Security Operations Center (SOC Guide) – 2023

Today’s Cyber security operations center (CSOC) should have everything...

Russian Hackers Bypass EDR to Deliver a Weaponized TeamViewer Component

TeamViewer's popularity and remote access capabilities make it an...

Web Server Penetration Testing Checklist – 2026

Web server pentesting is performed under three significant categories: identity,...

ATM Penetration Testing – Advanced Testing Methods to Find The Vulnerabilities

ATM Penetration testing, Hackers have found different approaches to...

Hackers Use ConnectWise SkyKick Credentials to Access Microsoft 365, Halting Cloud Backups

Attackers abused compromised ConnectWise Cloud Backup credentials to access...

Anthropic’s Claude AI Uncovers Origins of NSA-Provided Cryptographic Keys After 25 Years

Anthropic says an internal Claude research model reconstructed how...

OpenBSD Kernel Flaw Dating Back 37 Years Enables Local Privilege Escalation to Root

A newly disclosed OpenBSD kernel exploitation chain combines a...

GhostAction Hackers Hide Credential-Stealing Malware in Fake Font Files Across 94 GitHub Repositories

GhostAction attackers have expanded their GitHub credential theft campaign...

SideCopy Hackers Target Indian Organizations With ReverseRAT Malware to Steal Data

Indian authorities have warned that SideCopy hackers are targeting...

New GhostBat Android Malware Targets 60 Banking and UPI Apps to Steal PINs

A new GhostBat RAT variant targets 60 Android financial...

New ROMULUS Malware Platform Uses Six Servers to Deliver Multiple Malicious Payloads

ROMULUS, a shared ClickFix delivery platform operating across six...

Related Articles

Recent News


