

Cybersecurity researcher Evan Grant of the security firm Tenable has recently detected a vulnerability in the Microsoft Teams. And this vulnerability allows the threat actor to take control of the account of users.
By exploiting this flaw hackers can easily steal all the sensitive data like:-
- User’s Teams messages
- Emails
- One Drive files
Apart from this, the threat actors can also send emails and messages to disguise themselves as the users so that they can trick their victims easily; but, luckily this vulnerability has been patched.
Malicious Microsoft Teams Tab
This feature is one of the default features of Microsoft Teams, and the security researcher Evan Grant affirmed that the threat actors are taking the advantage of this default key feature.
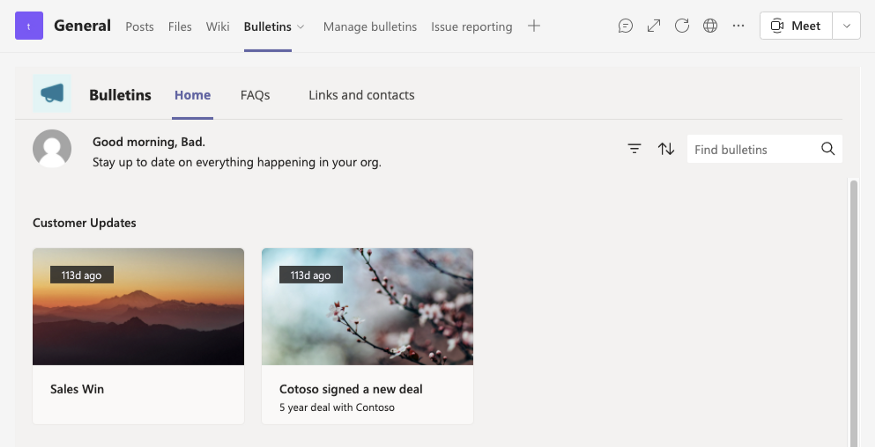
Microsoft Teams Tab feature enables the users to initiate small apps as a tab from the team they belong to, and this feature is applicable for all the users.
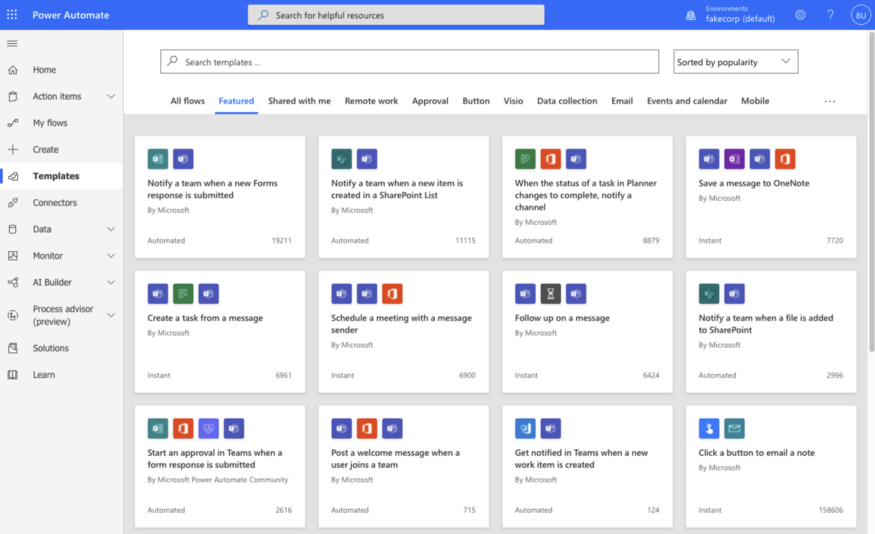
Here the power apps are the subset of the wider Microsoft Power Platform, and the main motive of initiating power apps is to store, manage and share team-specific data, apps, and flows.
But the hackers are miserably abusing this default environment for their own benefits and privileges.
Thieving Tokens
All the power tabs are not built for equal purposes, but, Evan Grant claimed that the power App extension tab types, the app.powerapps.com page generally interacts with both of its teams, “Teams JS SDK” and “Child iFrame,” here just by using the javascript postMessage it communicates.
During an investigation, Grant remarked that the frame which was being replaced is getting access to the tokens from its parent window, and the most important part is that it doesn’t require any further authentication.
Through this, the hackers are getting access to the tokens without any issue, since it doesn’t require any authentication to pass through.
Stealing more tokens, emails, messages, and files
Grant pronounced that, service.flow.microsoft.com tokens are taking more attention, as they can be easily abused by the threat actors to get access to more such tokens.
Once the threat actors get access to the tokens they can easily create a Power Automate flows, which would later allow them to get access to the user’s email from Outlook, files from OneDrive and SharePoint, Team messages, and many more.
Pieces of a PoC
- Office 365 (for Outlook access), and Teams connectors,
- Flow that allows them to send emails as the user.
- Flow that allows them to get all Teams messages from channels the victim is in and to send messages on their behalf.
Shortcomings
Moreover, one can carry out this attack, if he/she is a member of the Microsoft Teams; and this implies that this is a context of insider threat attack.
However, this attack can put a potential impact on the users and could be huge, especially if the motive of the threat actors is to hit an organization administrator.







