

Microsoft has recently claimed that Russia is one of the most active countries in organized cyberattacks. Russian hackers were the most active in the world in implementing strong cyberattacks.
Russian hackers were responsible for 58% of all the cyberattacks that targeted Government networks. Not only this even the “Russian hackers” mostly target the countries like:-
- The United States
- Ukraine
- Great Britain
- The European states belonging to NATO
Till now Russia has been the nation-state threat actor that is conducting many types of attacks in different parts of the world. After Russia, Microsoft has detected that the largest amount of attacks came from North Korea, Iran, and China.
And on this list South Korea, Turkey, and Vietnam are also included, but with less volume of attacks.
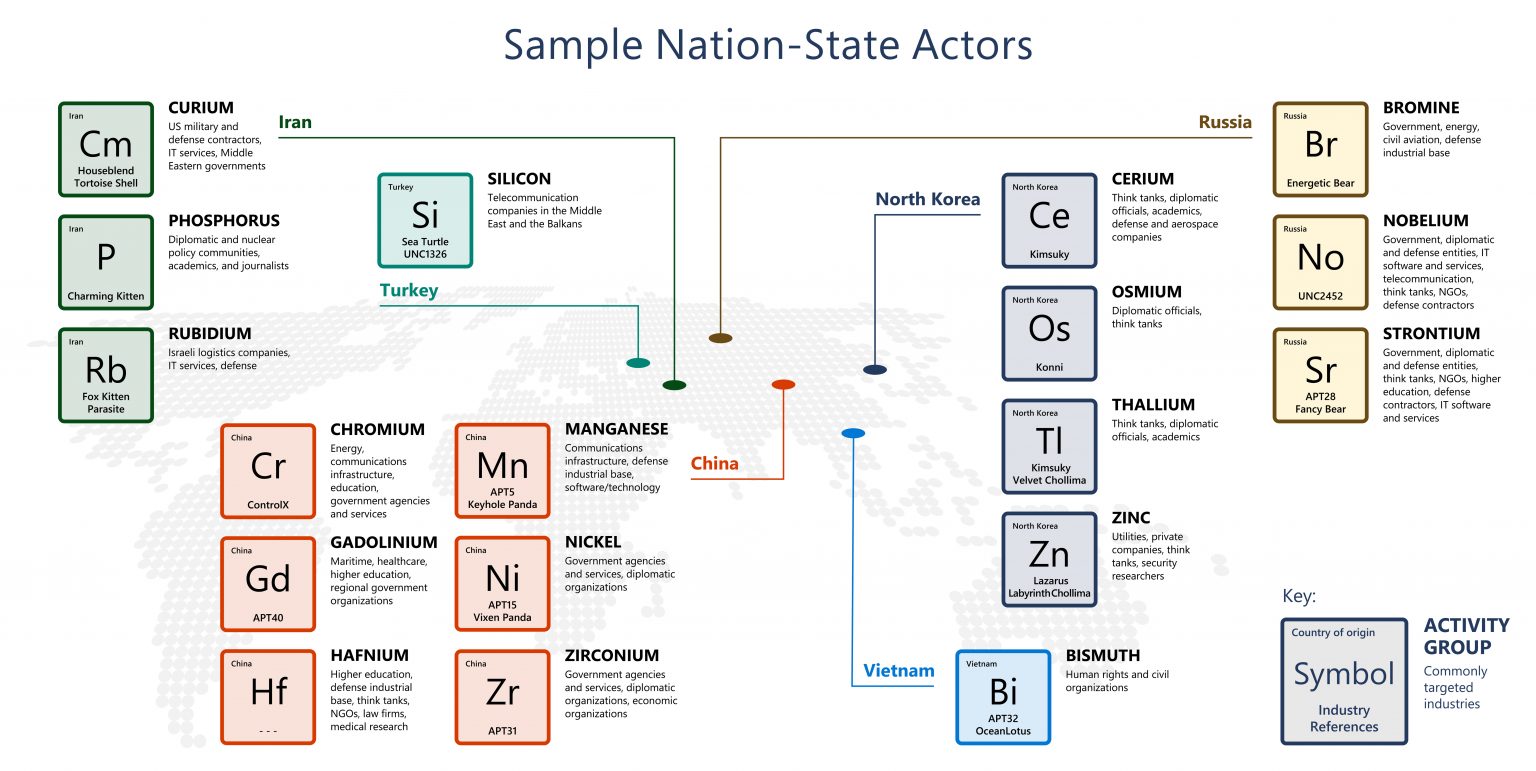
Iran has been targeting Israel in the past year and during the attack, it has launched many devastating cyberattacks that have created huge tensions between the two countries
Whereas, North Korea has been targeting cryptocurrency companies with the motive of profit as its economy was decreased by penalties and due to Covid-19.
Till now 21% of cyberattacks were being observed across nation-state threat actors that have targeted consumers. On the other side, 79% targeted enterprises that include 48% of the government, 31% of NGOs and think tanks, 3% education, 3% intergovernmental organizations, and many more.
Cybercrime
Nowadays ransomware attacks are increasing at a rapid speed, and that’s why cybercrime has become a common problem. However, the nation-state threat actors are mostly targeting victims that have valuable information, and the threat actors are also targeting the victims with money.
To initiate different targets, the threat actors make different profiles to attack the victims. The United States is one of the most targeted countries that encounter more than threefold ransomware attacks.
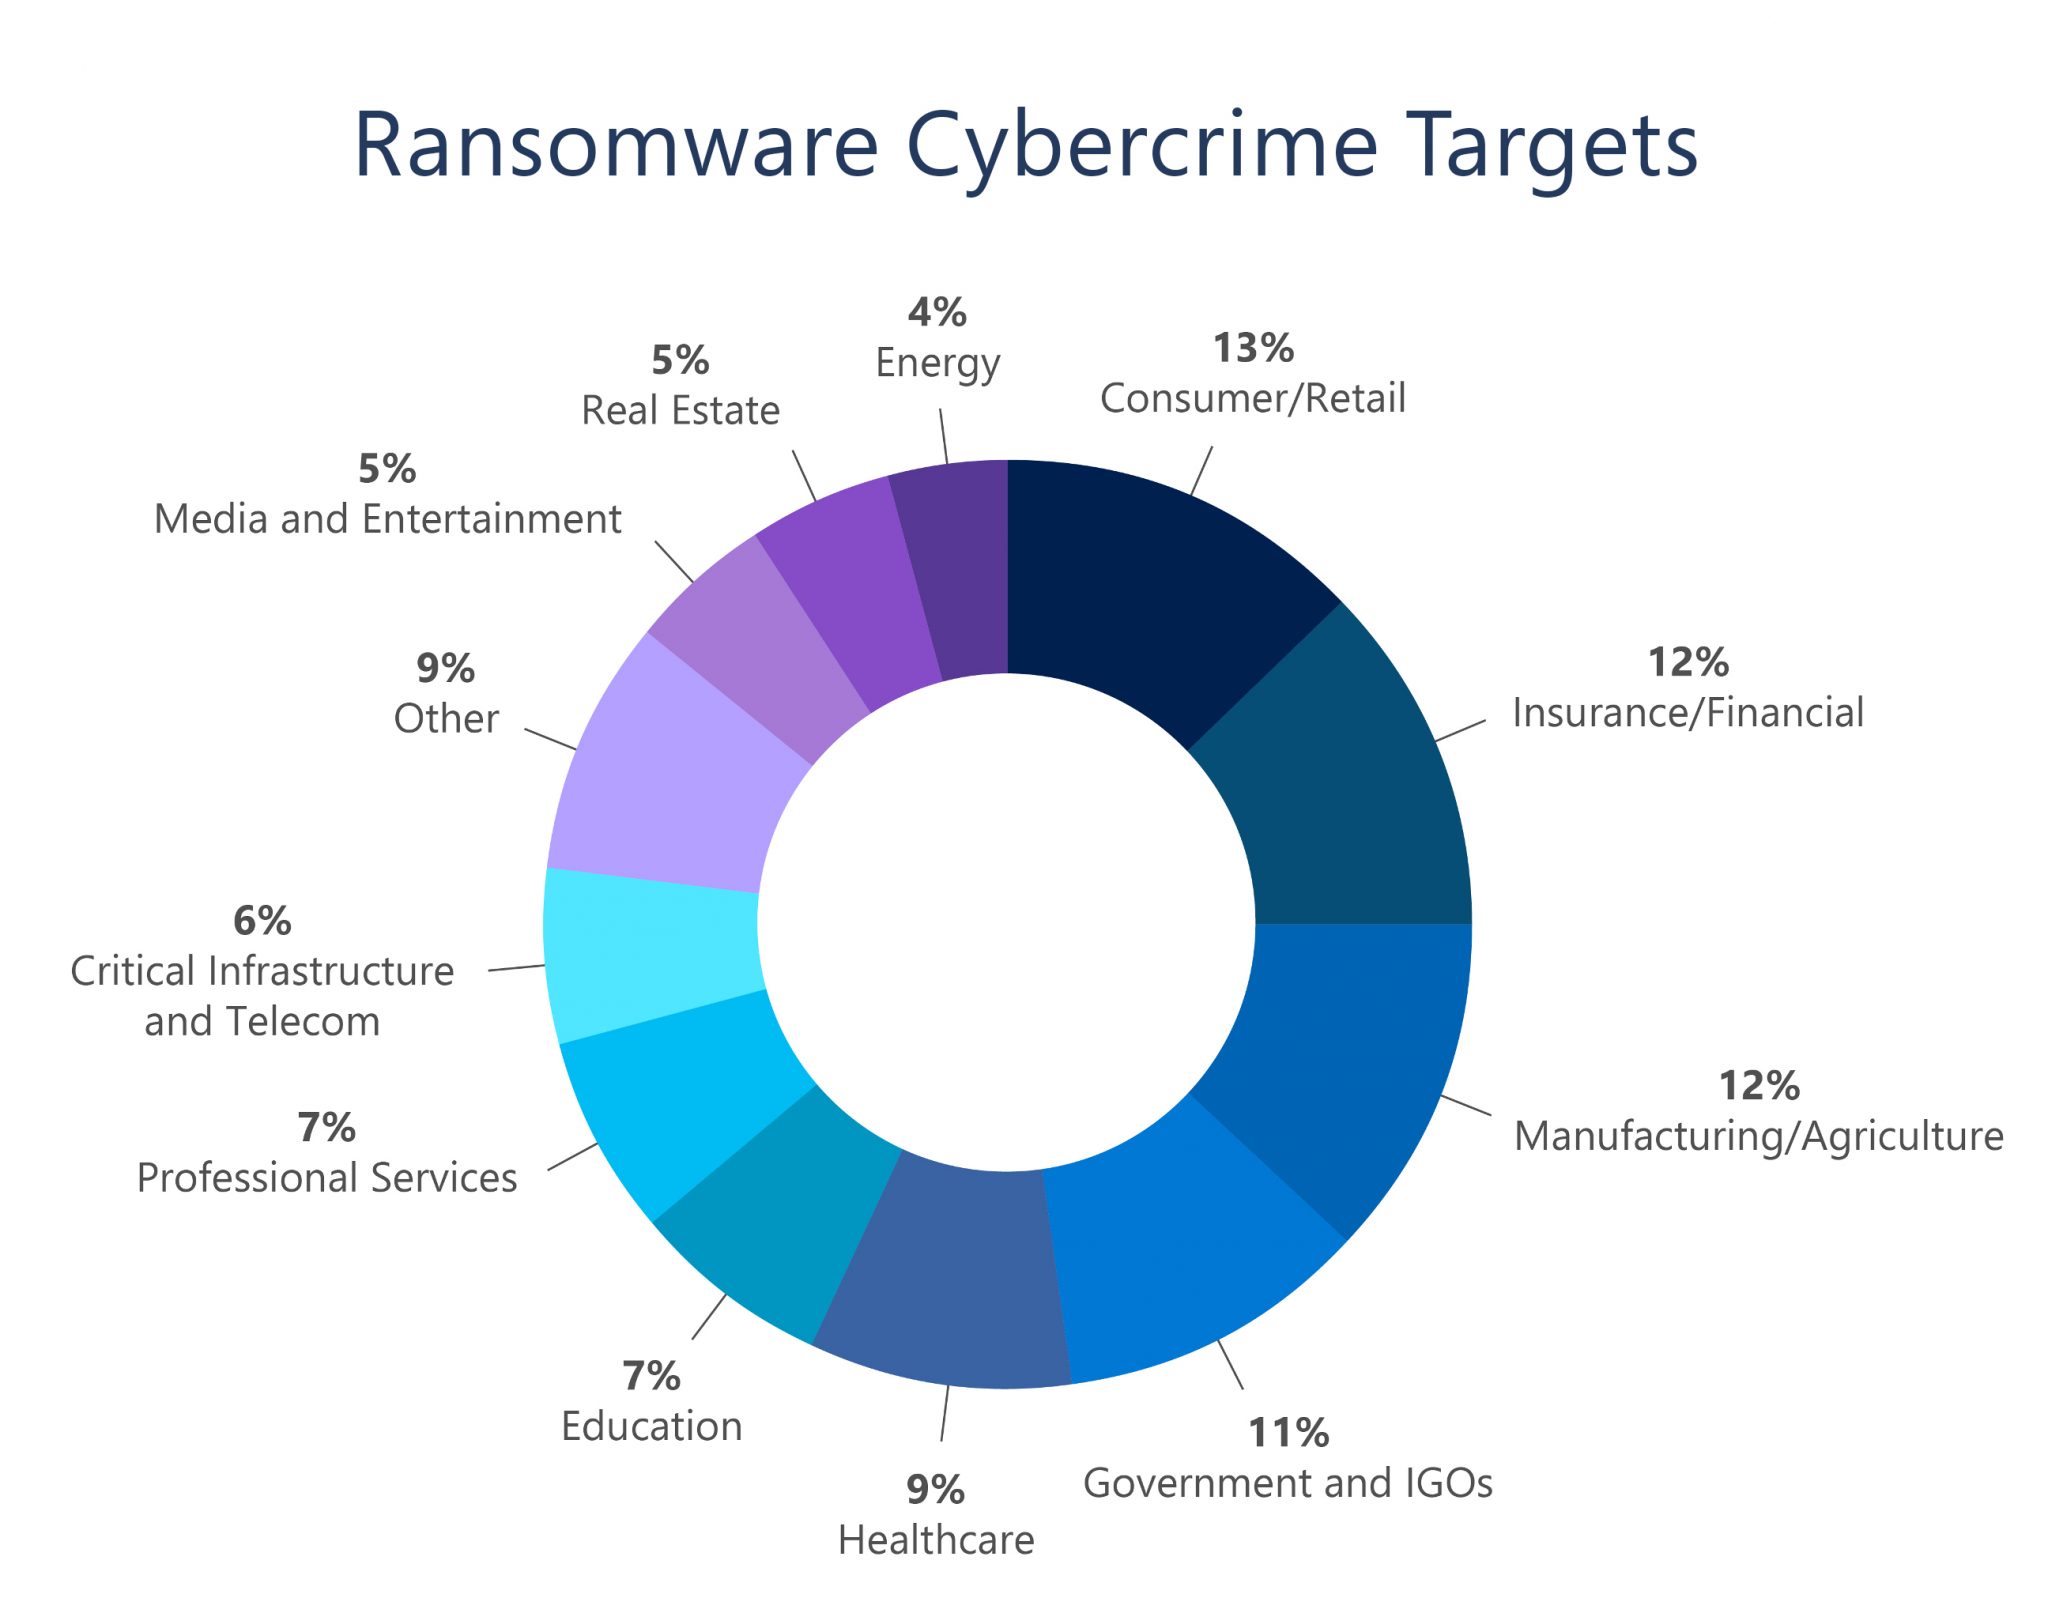
Nowadays the cybercriminals are mainly focused on training themselves in differentiated off-the-shelf infection kits and expanding their use of automation, running down their costs, and increasing their scale.
Till now ransomware remains to be one of the largest cybercrime perils and, in the past year, it has proceeded to develop and to become more disruptive.
Striving back in a hybrid work context
Among all, the online threats are the most common attack, and that’s why Microsoft has claimed that initiatives should be taken to strengthen the first line of defense.
However, the organizations are exercising basic steps to defend themselves from this kind of attack, and the positive point is that, in the past 18 months, it has been recorded a 220% increase in strong authentication usage.
The companies have thought about improving their security posture in a remote work environment. But, the nation-states are increasingly using, and they will continue to attack, therefore companies need to increase the protection to keep themselves safe.







