

In Signalling System No. 7 or SS7 back in 2016, the cybersecurity researchers warned of vulnerabilities in it, and as a result, just a year later, the SS7 attacks turned real ones from theoretical.
To track individuals abroad the government-sponsored hackers exploited vulnerabilities in SS7 in the subsequent years. And not only that even the threat actors also exploited them to hack Telegram user accounts and emails.
Aside from exploitation of SMS, the SS7 security flaws can be exploited for several things like:-
- Intercept or forward calls
- Forward or intercept 2FA codes
- Locate devices
- Spoof SMS
Investigating SS7 exploitation services
For getting the exact data and report, the security analysts at SOS Intelligence decided to investigate all the SS7 exploitation services available on the darknet and analyze them to detect that whether they have vulnerabilities at their end or they are just fake.
As a result, they investigated 84 unique onion domains that claim to offer SS7 exploitation services. To make it more precise and transparent, they narrowed down the results, and they have mentioned four services that are appeared to be still active.
Four services that are appeared to be still active:-
- SS7 Exploiter
- SS7 ONLINE Exploiter
- SS7 Hack
- Dark Fox Market
After examining the network topology data of these websites, they found that some of the websites were relatively private and had few inbound links.
In short, it is not a good and healthy indication of a website’s trustworthiness and credibility. Since all these elements depict that they are newly created fraudulent platforms.
While here, the SS7 Hack website looks like a scam, since it is appeared to be copied from a clearnet website that is created in 2021.
Even the experts didn’t get anything while they tried to use their set of SS7 exploits in the belief of implementing API mirroring functionality, but later the sound that service was disabled.
Services offered
Services offered by the four websites to their customers are mentioned below:-
SS7 Exploiter
- Get Location
- DoS subscriber
- Intercept calls
- Intercept SMS
- Spoof call/SMS
- Manage subscription
- Voicemail settings
- Upload SIM toolkit
SS7 ONLINE Exploiter
- Get Location
- DoS subscriber
- Intercept calls
- Intercept SMS
- Spoof call/SMS
- Manage subscription
- Voicemail settings
- Upload SIM toolkit
SS7 Hack
- SMS Intercept
- Call Intercept and Redirect
- Location Tracking
Dark Fox Market
- SS7 Bypass 2FA (SMS Intercept)
- SS7 Call Intercept
- SS7 Location Tracker
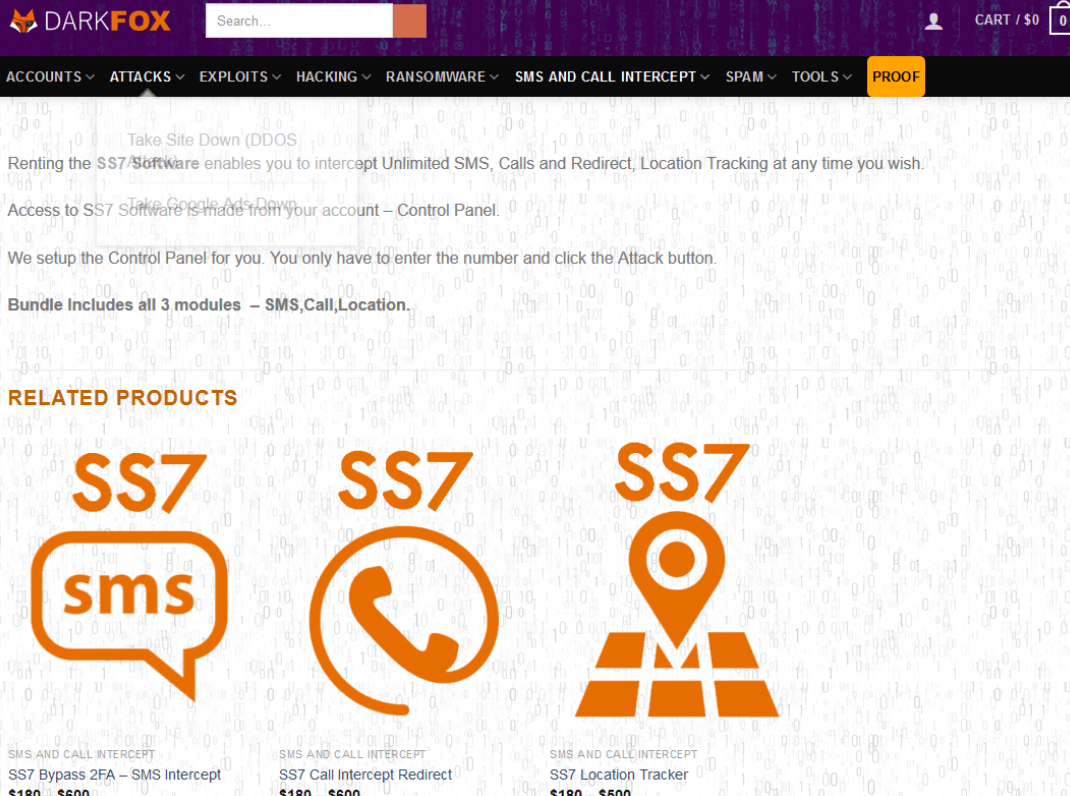
Moreover, during further examinations, it has been detected that in 2016 a Russian-speaking user uploaded demo videos on YouTube regarding the services offered by the Dark Fox Market platform that charges $180 for each attacked phone number.
But, here the most interesting thing is that all the demo videos were stolen from YouTube itself, and they had no relevance to the Dark Fox Market portal.
To get the genuine deal, one would have to dig deeper, as there are most of the portals are filled with fraud and scammers.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity updates







