

The Chinese hacking group known as Tropic Trooper was attributed to a new campaign discovered by cybersecurity researchers at CheckPoint. In this case, a new variant of the Yahoyah trojan is being used along with a new loader called Nimbda.
In addition, the trojan is embedded in a Greyware tool designed for DoS attacks against mobile phones. This tool is called SMS Bomber, and it floods phones with messages.
While such tools are frequently used by beginners in the field of cybersecurity who are looking to conduct attacks against websites.
As a sign of their advanced cryptographic skills, the threat actors developed their own custom implementation of the AES specification, extending its functionality.
Attack flow
A malicious version of SMS Bomber is downloaded as part of the infection process. The following things are contained in this SMS Bomber –
- Tool’s binary
- Standard functionality
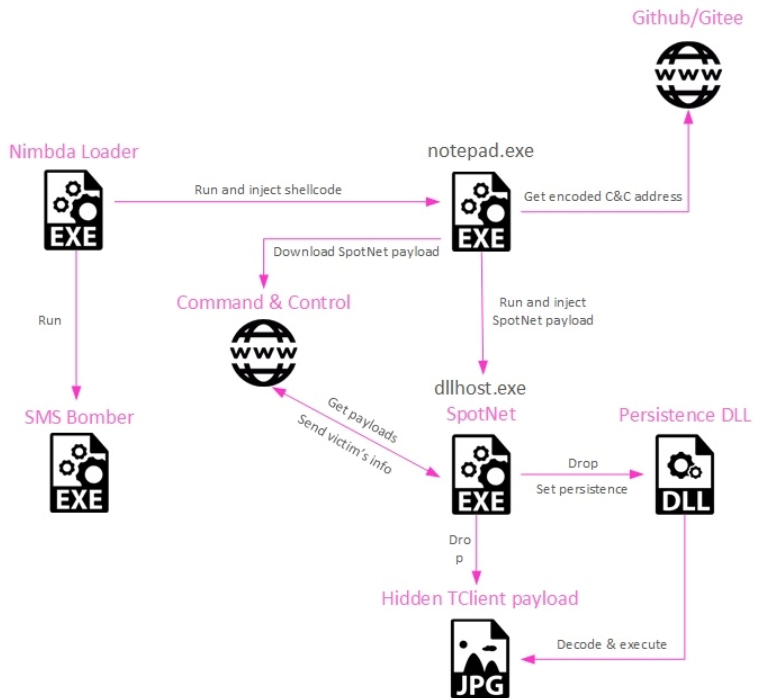
In addition to the modified download, a new file that injects a piece of code within a notepad.exe process has also been included.
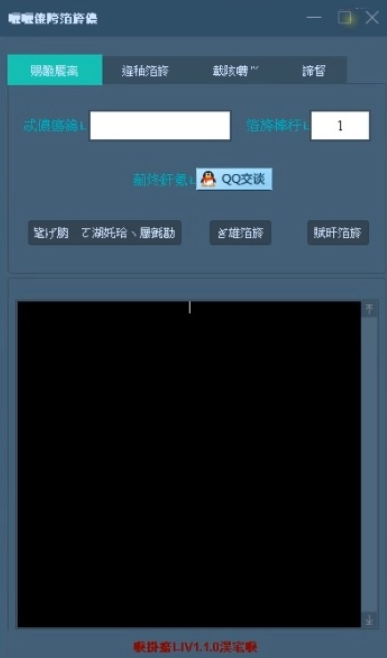
There is actually an executable in the downloaded file called Nimbda which is the loader. SMS Bomber is an embedded executable in this loader that allows it to use the icon associated with SMS Bomber.
Shellcode is integrated into a notepad in order to create a background connection to a GitHub repository. Next, it fetches an executable that is obfuscated, decrypts it, and then executes it through a bug in DLLhost.exe, which exploits this loophole.
A brand new variant of Yahoyah is used for this payload. Here to gather data about the host the threat actors use this payload and then it sends the gathered data to the C2 server.
According to the report, Below we have listed all the types of information gathered by Yahoyah:-
- System name
- Existence of WeChat files
- Existence of Tencent files
- MAC address of the system
- AV products installed on the system
- Local wireless network SSIDs
- OS version
Implementation of custom AES
Yahoyah uses a custom implementation of AES to encrypt data that is sent over the internet. In the technique it uses, double rounds of inversions are performed.
Due to this implementation, Check Point has named it “AEES.” However, it does not make the encryption more robust, but rather, it makes it very hard for the security experts to examine the sample.
At the moment, it is unknown what the exact scope of the targeting will be. In this campaign, it is demonstrated how Tropic Trooper’s stealthy skills and capabilities can be used.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity updates.







