

A surge in the number of Stegomalware instances using Steganography has been reported recently by the cybersecurity experts at Cyble Research Labs.
Steganography is mainly a method that entails concealing data inside of a normal message or file in a specific manner. The type of file it uses:-
- Text
- Image
- Video
There is no doubt that Steganography is one of the most evasive and difficult-to-detect methods of malware. Stegomalware uses image steganography to avoid detection mechanisms such as anti-virus software and anti-malware systems.
As a result of the use of Image Steganography, more than 1,800 malware samples have been identified in the wild over the last 90 days. Below is a summary of the distribution of stegomalware on a Monthly basis.
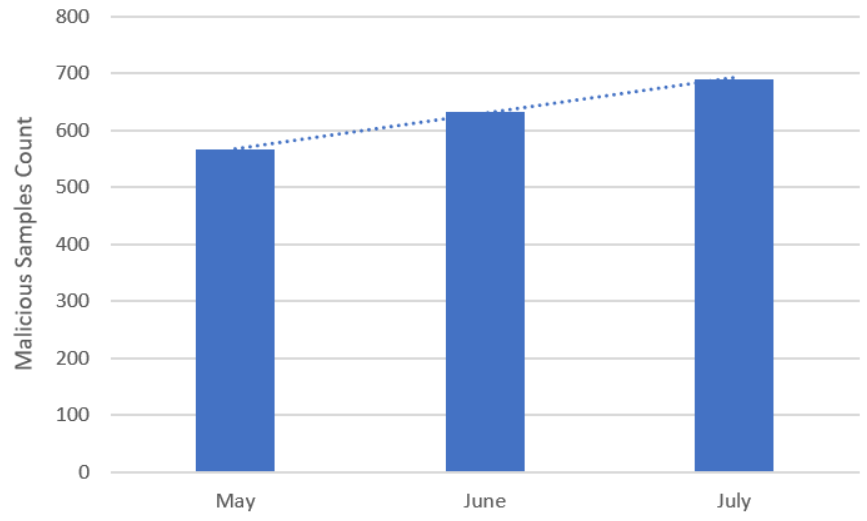
Malware using Steganography
It is worth mentioning that there are several prominent malware families that use Steganography, including:-
- Knotweed
- Web Shells
- Hacking Tools: Mimikatz, Rubeus
- NanoCore RAT
- AgentTesla
- XLoader
It has been discovered that numerous instances of .JPG+EXE malware have been seen during the monitoring of chatter across multiple threat actors.
A malicious exe file is usually disguised as a legitimate image file and it is then injected into an image file using the Image Steganography technique.
Researchers reported two attacks in the last few weeks of July 2022, which were carried out by unknown individuals. Steganography was used in these attacks to deliver malware payloads in order to carry out the attack.
Technical Analysis
Various reports have been made about the effect that APT TAs have used.SFX files to use as a way to attack ICS/SCADA systems using exploit DB files.
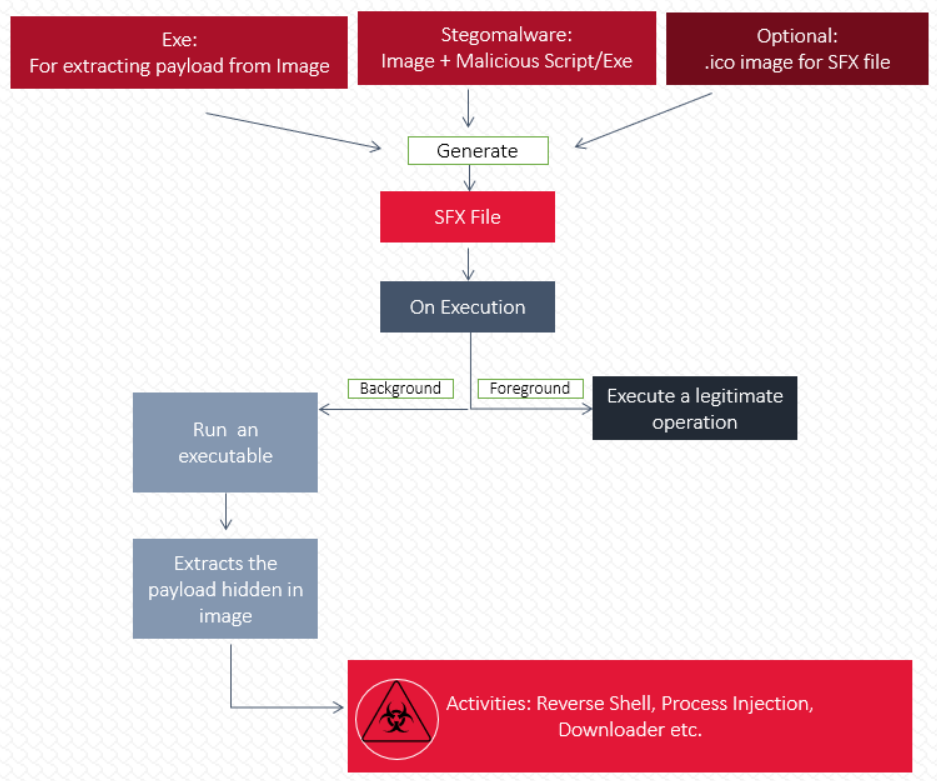
Other systems can also be attacked with this attack vector. An executable file with the extension .SFX contains compressed data that can be uncompressed during the process of implementation.
It is also possible to execute the compressed files that are enclosed in a .SFX file, which allows TAs to easily execute malware through this technique.
Here the AgentTesla malware is extracted from the .JPG file in the archive after the .SFX archive has been extracted.
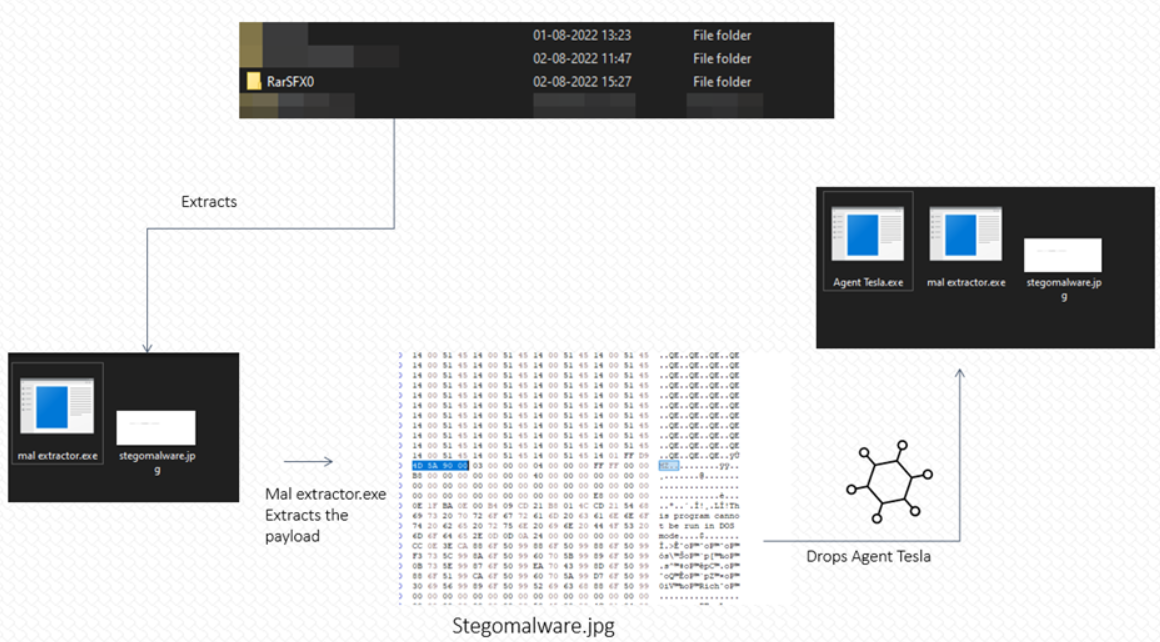
As a result of the extraction of malware, additional evasion capabilities may be leveraged directly by combining it with legitimate processes.
Recommendations
The following are some of the best practices in cybersecurity that are recommended by the experts:-
- Make sure that you are aware of the latest threat actor attack techniques that are being employed by them.
- Be sure that your connected devices, including PCs, laptops, and mobile phones, are protected by an robust anti-virus tools.
- To prevent data exfiltration by malware or Trojans, monitor the beacon on the network level.
- Check the contents of the file at the end, as well as unusual file signatures and properties, when inspecting suspicious images manually
- Before downloading any file, it is recommended that you verify the source.
- Passwords should be updated at regular intervals.
- Make sure you verify the authenticity of all links and email attachments before opening them.
- Virus-spreading URLs, such as torrents and warez, should be blocked.
- Ensure that employees’ systems are equipped with Data Loss Prevention (DLP) solutions.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity updates.







.png?fit=728,380&ssl=1&description=A surge in the number of Stegomalware instances using Steganography has been reported recently by the cybersecurity experts at Cyble Research Labs.)