

Cybersecurity experts at Cyble Research and Intelligence Labs (CRIL) have recently identified a fake AnyDesk website (hxxp://anydesk[.]ml).
They found this website was spreading Mitsu Stealer, and it’s a sophisticated custom-made 64-bit malware. This malware is primarily designed to steal all sensitive information from unsuspecting victims.
One of the most surprising aspects of this malware is that it is constructed from code that is freely available on GitHub.
Currently, the website has not been involved in any malvertising campaigns. However, the mediums used by the operators of this fake website for promotional purposes are:-
- Malspam
- SMS
- Social networks
Infection chain
According to the report, After clicking on the Downloads button on the phishing website the infection chain begins, and the user gets infected by the malware delivered by the phishing site. The Mitsu Stealer malware was downloaded from the remote server in the following form:-
- Anydesk.exe
It’s a 64-bit Windows executable file that is based on the Microsoft Visual C++/C++ GUI.
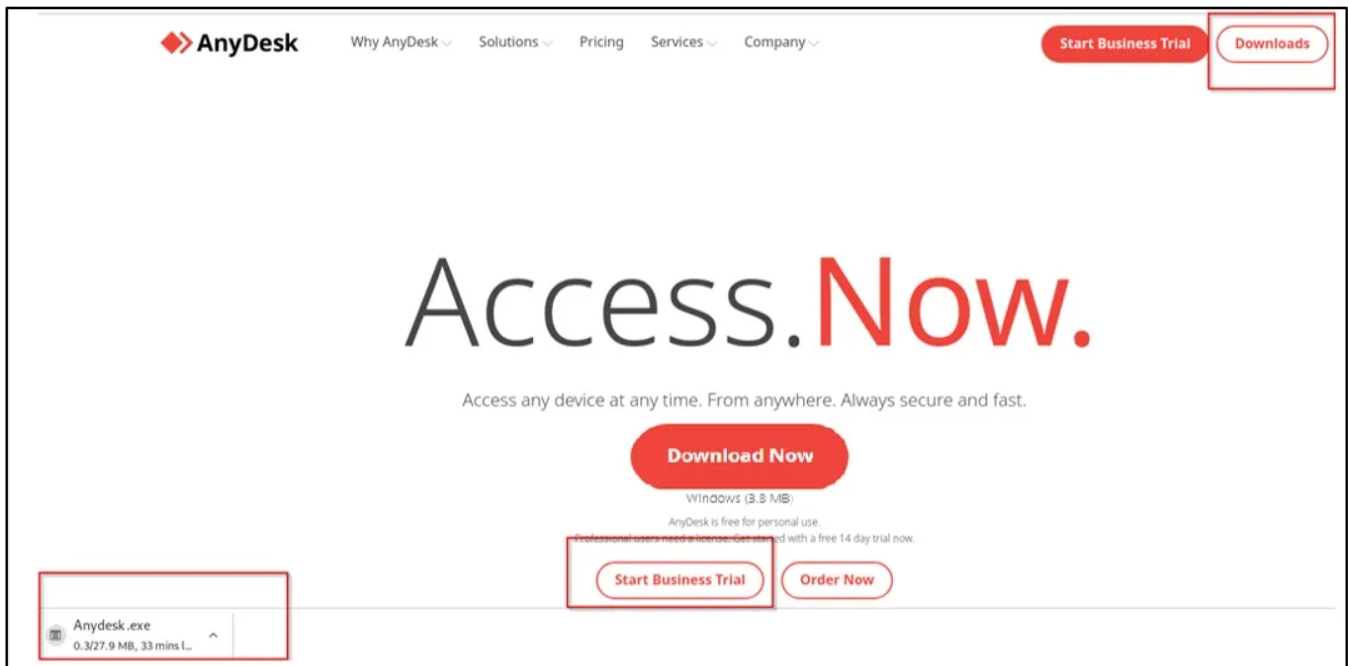
There is much similarity between the phishing site and Anydesk’s genuine website when it comes to its appearance. In short, the threat actors have designed the fake phishing website perfectly with all the elements that are present in the genuine website.
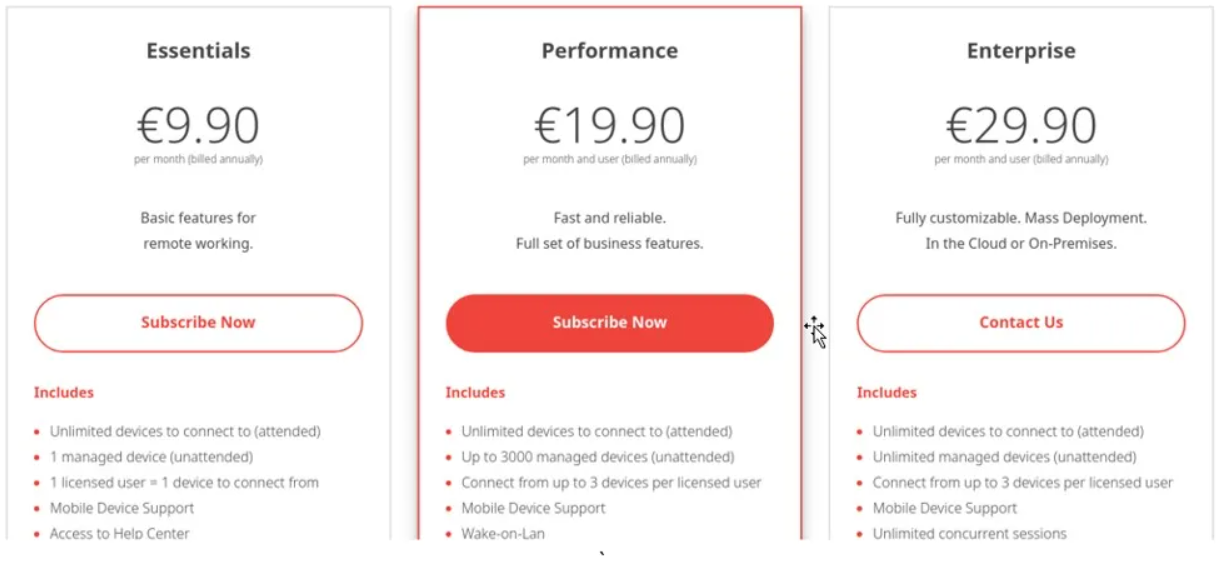
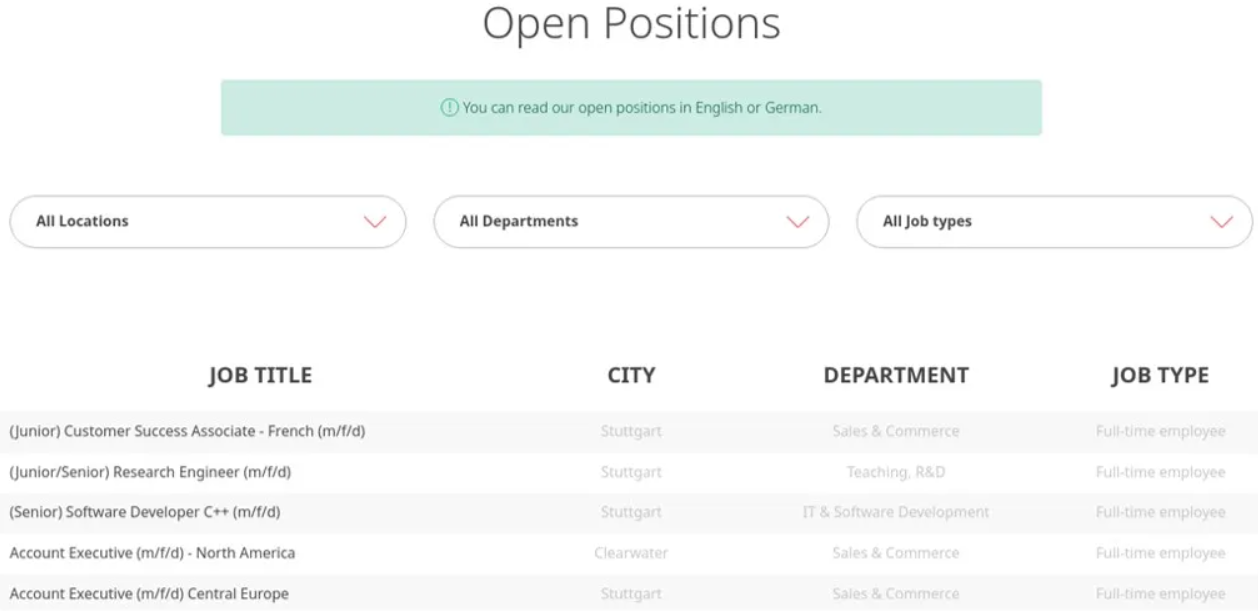
Here below we have mentioned other two key aspects that the threat actors have mimicked from the original one to make the fake website more authentic:-
- Subscription page
- Career section with fake jobs opening
Technical analysis
The Mitsu Stealer was created using the Python programming language. The stealer performs the following illicit actions when it is executed:-
- Drops the python supporting files (e.g. “.pyd” & “.dll” files)
- Steals sensitive information
- Deletes them after successful execution
Upon installation of the malware, it will now create a list of the processes running on the computer system of the user. In order to determine the names of the processes associated with the network analysis tool, the program examines the names of the processes.
Now to replace the API/webhooks with MitsuTheGoat, the malware circumvents the BetterDiscord. Thereafter, from the infected system of the victim the stealer collects all the sensitive data like:-
- Usernames
- Passwords
- Cookies
- Auto-fills
- User profiles
The malware also targets cryptocurrency wallets and other wallets to steal financial information and abuse them for financial gains. For data extraction following SQL queries are used by the malware:-
- SELECT host_key, name, encrypted_value FROM cookies
- SELECT action_url, username_value, password_value FROM logins
Targeted browsers
Here below we have mentioned all the web browsers targeted by the stealer to steal user data:-
- Google Chrome
- Microsoft Edge
- Opera GX Stable
- Opera Stable
- Mozilla Firefox
In order to collect Discord tokens, the malware reads and extracts the following files from a variety of locations across the system:-
- .log
- .ldb
The malware then creates a JSON dump that sends the stolen data to a Discord webhook. Afterward, the stealer downloads a JavaScript file called index.js in order to conduct the illicit activity that the threat actors want.
Recommendations
Here below we have mentioned all the recommendations:-
- Make sure you do not download tools or software that is pirated.
- Passwords should be strong
- Multi-factor authentication should be implemented
- Activate the automatic software update feature
- Make sure you use a reputable antivirus program
- Do not open untrusted links or attachments in emails
- Enable DLP Solutions
Also Read: Download Secure Web Filtering – Free E-book







 have recently identified a fake AnyDesk website (hxxp://anydesk[.]ml).)