

Introduction
Cybersecurity is an evolving space. Cybersecurity threats have grown over the years in number and complexity. This means we should continuously monitor and defend our organization and stay updated about new developments within the space. Traditional ways of security testing are being exploited by hackers as the more sophisticated hacker has learned to recognize test patterns.
To adapt to this development, enterprises have started leveraging breach and attack simulation (BAS) platforms, which enables them to continuously simulate real-time security attacks on their own IT infrastructure in an automated and consistent fashion. This process provides an eagle’s view of the entire security posture of the organization to stakeholders.
BAS platforms provide a new method of security testing that mimics real-world cyber attack scenarios. The attacks are continuous and automated, providing insights from different angles. This mimicking mechanism helps organizations identify potential security vulnerabilities, allowing them to proactively close gaps.
Why We Need to Use BAS Solutions
Traditionally, security attack simulations are done by the Red and Purple Teams in the organization, which is a labor-intensive process. These simulations take a lot of planning and take several days to provide results. By the time the organization receives an actionable report on the results of the test, parts of the report will have become outdated. New vulnerabilities may have already been introduced in the system since the completion of the test. BAS platforms work 24×7, and if you want a status check of your organization’s security posture, you can readily view and take remediation if required.
Different Types of BAS Solutions
We can classify BAS solutions into three categories based on the approach. Each type has its own pros and cons depending on the use case.
1. Agent-based scanners
This approach involves the installation of agents/scanners within the organization’s LAN network. It maps network routes and scans through the routes.
2. Injection of malicious traffic
This involves injecting malicious traffic into the organization’s internal network. Spare VMs are set up in the network to act as the target, which is continuously attacked by a series of security tests.
3. Multi-vector simulated attacks
Out of the three approaches, this is the most advanced. It is capable of generating real-time attack simulations in the IT infrastructure. Lightweight agents are installed on the machines and send data telemetrics to the cloud endpoints. The agents get updated information about the latest vulnerability attacks from the cloud endpoints.
Features an Ideal BAS Product Must Possess
If you are looking for a good BAS product, it is important to know what to look for based on your needs. Some of the characteristics that you definitely should want are integration, depth of coverage, and actionable insights and recommendations.
Integration
This is an essential feature that a BAS platform must provide. In an enterprise, there will be systems/tools for managing the existing infrastructure and closed integration. A good BAS product should be able to integrate with SIEM tools, communication tools, and workflow tools -JIRA/Service now.
Depth of Coverage
The security test coverage suite supported by the BAS platform must be comprehensive, and it should be updated with the latest threats in the market. Also, we have to check whether there is a possibility to add custom tests to the stack providing customizability.
Actionable Insights and Recommendations
A good BAS product should be able to provide in-depth insights about existing security posture and provide a course of action and remediation options. Just providing a view of the threats in the systems isn’t enough. Remediation takes a lot of effort if you move manually.
Example of a BAS Product
One of the main leaders in the BAS Space is Cymulate. The product is an agent-based SaaS platform that can be deployed within 5 minutes and provides insights within a couple of minutes. It acts as a black box on the network and allows integration with existing security systems and other major softwares.
After executing in-depth simulations, it produces a map of the network and its threat profile, an executive summary of the situation that can be presented to management, and a more technical rundown that includes recommendations for mitigations and remediations.
Key Benefits
- Mitigate attacks before they happen
- SaaS-based solution and no hardware required
- Easily Plug and Play
- Immediate results 24/7, 365 day a year
Features
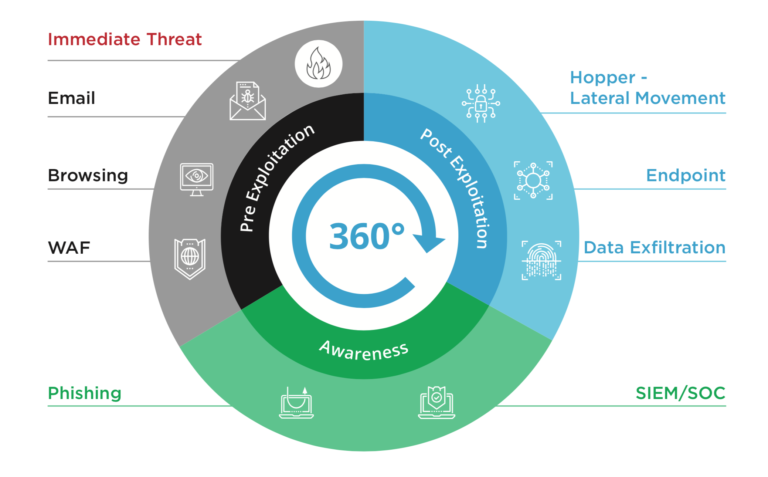
Cymulate continually validates an organization’s actual security against eight attack vectors, identifies real security gaps, monitors security trends, and generates reports for executives and technical staff that include actionable recommendations for addressing vulnerabilities.
Conclusion
With the recent evolution of cyberattacks, proactive scanning and remediation of security vulnerabilities is an unavoidable task for enterprises. BAS platforms really help in this part by continuously running the scan and providing remediation on the fly in an automated manner.







