

GitHub launches a new code scanning tool that helps developers to detect vulnerability before the application reaches production.
The tool was announced initially in May at the GitHub Satellite conference, since that time it is available for GitHub beta testers.
GitHub Code Scanning Tool
Now the GitHub code scanning tool is available for all users and they can enable it to form a public repository. The new tool is the result of the acquisition of Semmle last year.
Semmle is a code analysis platform that helps developers to write queries that identify code patterns in large codebases and search for vulnerabilities and their variants.
GitHub said they “worked to bring the revolutionary code analysis capabilities of its CodeQL technology to GitHub users as a native capability.”
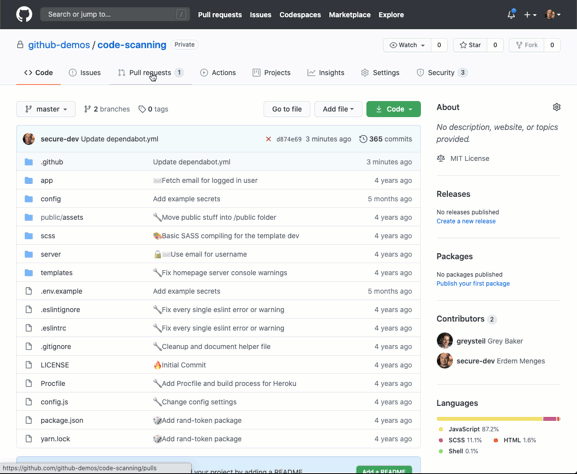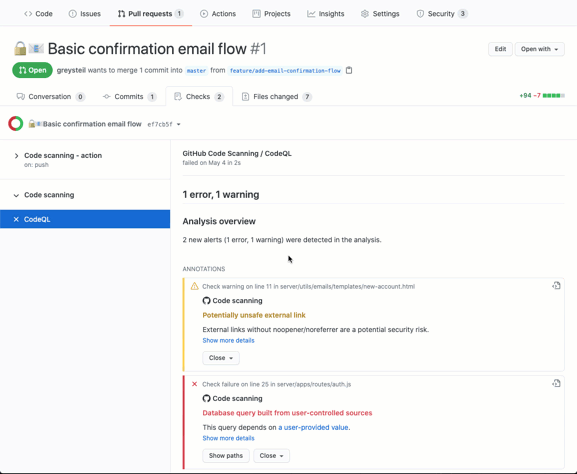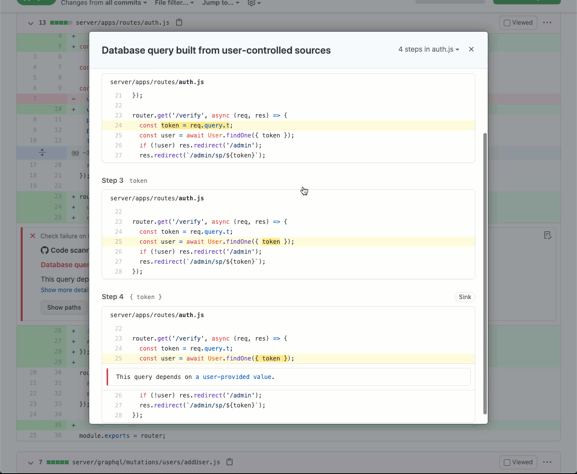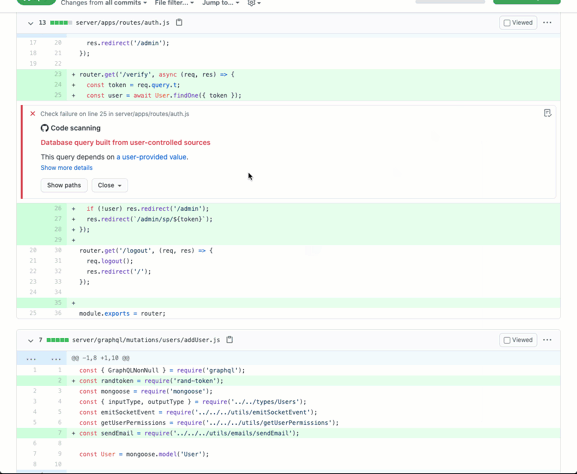
Code scanning tool powered by powerful code analysis engine CodeQL technology to GitHub users as a native capability. The tool gets integrated with GitHub Actions—or your existing CI/CD environment—to maximize flexibility for your team.
Since the launch of the beta version, the tool scans over “12,000 repositories 1.4 million times, and found more than 20,000 security issues including remote code execution (RCE), SQL injection, and cross-site scripting (XSS) vulnerabilities.”
The tool helped developers to fix 72% of security errors before moving the application with the production environment.
Code scanning is free for public repositories here you can find how to enable code scanning today. For private repositories, it is available through Advanced Security.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.
Also Read
GitHub Announces Unlimited Private Repositories For Free Plan


