

A never-seen-before malware that is dubbed as “DazzleSpy” has been found in macOS by the cybersecurity researchers at ESET security, leveraging a Safari web browser exploit.
The hackers are found using exploits that were almost impossible to detect, and not only that, even users can’t stop it once they land on an infected website.
This clearly depicts that the operators or the developers of DazzleSpy are pure professionals who have sufficient resources and skills to develop malware like this.
Features of DazzleSpy
With such cutting-edge capabilities, DazzleSpy offers advanced abilities to monitor and control the Macs that are infected thoroughly.
However, here we have mentioned all the key features offered by the DazzleSpy malware:-
- Keylogging
- File download/upload
- Audio recording
- Executing terminal commands
- Fingerprinting the victim device
- Dumping iCloud Keychain
- Screen capturing
- Harvesting system information
- Deleting itself from the machine
The threat actors have targeted the politically active, pro-democracy individuals in Hong Kong as a part of a watering hole attack. While in November 2021, a similar intrusion was also reported by the Google Threat Analysis Group (TAG).
Attack Chain
In this attack chain, to inject malicious inline frames (aka iframes), the attackers have targeted and compromised a legit website of a radio station or channel in Hong Kong, known as D100 Radio between the following time frame:-
- 30th September 2021
- 4th November 2021
To lure the liberation activists, the threat actors have used the following website:-
- fightforhk[.]com
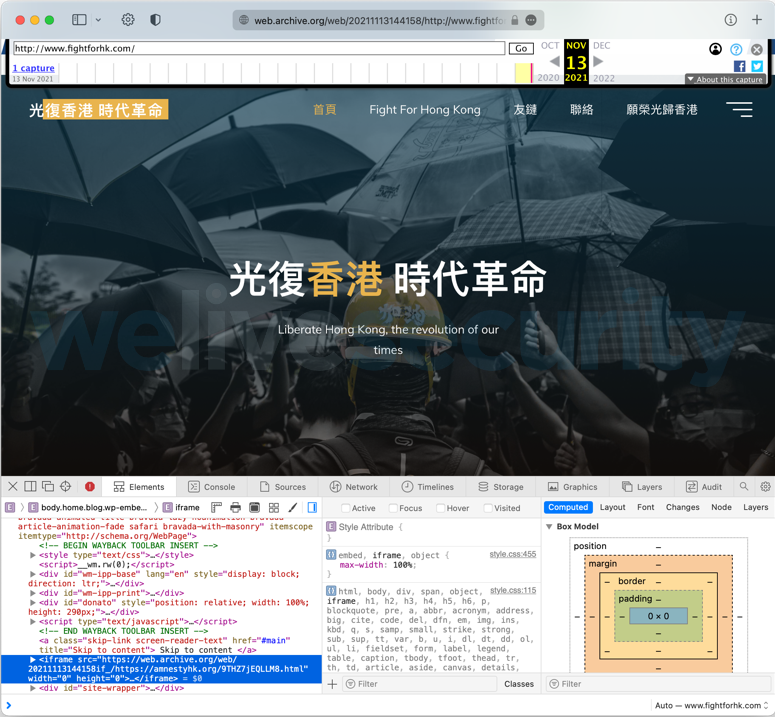
In the recent era, the threat actors are constantly targeting Apple’s Mac with several advanced malware and malicious TTPs, as compared to Windows operating system.
Here’s what the cybersecurity analysts at ESET security firm stated:-
“The exploit used to gain code execution in the browser is quite complex and had more than 1,000 lines of code once formatted nicely. We haven’t seen payloads for Windows nor clues that it would exist. Secondly, they have the resources to develop complex exploits and their own spying malware, which is quite significant.”
To trigger the execution of the intermediate Mach-O binary, the attacker abused the WebKit RCE exploit and recently patched local vulnerability in the kernel component that was tracked as CVE-2021-30869.
All these steps are compiled together by the threat actors to run the next stage of malware with escalated root privileges.
Commands Used
Here we have mentioned below all the commands used by DazzleSpy malware:-
- heartbeat
- info
- searchFile
- scanFiles
- cmd
- restartCMD
- restart
- processInfo
- keychain
- downloadFileInfo
- downloadFile
- file
- uninstall
- RDPInfo
- RDP
- mouseEvent
- acceptFileInfo
- acceptFile
- socks5
- recoveryInfo
- recovery
The operation depicts that DazzleSpy malware primarily targets the entities in Hong Kong who are politically active and pro-democracy individuals.
Moreover, this malicious campaign has similarities with LightSpy iOS malware that was detected by the security analysts of TrendMicro and Kaspersky in 2020, since LightSpy also uses iframe injection on websites.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity updates






