

In a daily routine check-up, cybersecurity researchers have detected a very new wave of malicious apps in Google Play store.
The analysts have found these malicious apps in Google Play Store, the apps are continuously targeting Android users, and hijack SMS message notifications for carrying out billing frauds.
However, these malicious apps are targetting users from Southwest Asia and the Arabian Peninsula. The main motive of the operators of these malicious apps is to target Android users, and they have already targeted more than 700,000 users.
According to the McaFee report, the malicious apps gets removed from the platform before they were discovered by the analysts.
Technical Summary
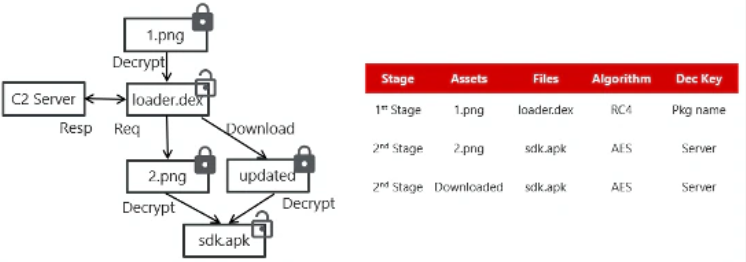
These malicious apps are quite dangerous for Android users, as it has been loaded with some critical malware, and that malware takes the advantage of dynamic code loading.
Moreover, this malicious app contains the encrypted payload, and as per the experts, these payloads appear in the assets folder that is directly linked with the malicious app.
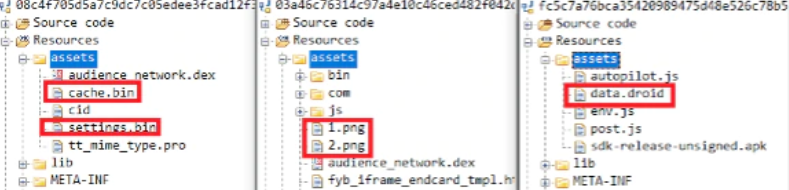
The encrypted payloads that are present in this malicious app using names like “cache.bin,” “settings.bin,” “data.droid,” or harmless“.png” files.
This malicious app is quite hazardous and it contains spyware capabilities, and the experts have mentioned all the capabilities of the malicious app:-
- Stealing contact lists
- All the device information
- SMS messages
Not only this but the malicious app also employs a method known as versioning that is connected directly to clean a version. The analysts also asserted that the hackers are building trust among the users.
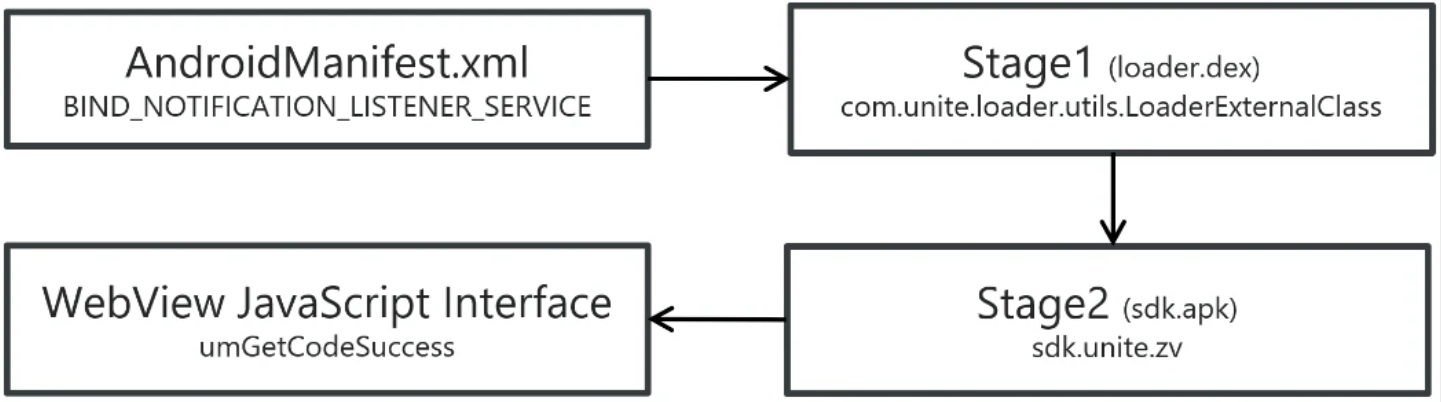
Once the hackers get access and gain trust, they sneakily add the malicious code and at a later stage through an app they update them.
Infected Apps
After tracking all the functions of this malicious app, the experts came to know that Google Play Store has removed nearly 1700 infected apps. That’s why the researchers have suggested a list of nine apps, that are infected:-
- Keyboard Wallpaper
- PIP Photo Maker
- 2021 Wallpaper and Keyboard
- Barber Prank Hair Dryer, Clipper, and Scissors
- Picture Editor
- PIP Camera
- Keyboard Wallpaper
- Pop Ringtones for Android
- Cool Girl Wallpaper/SubscribeSDK
However, the team of cybersecurity analysts at McAfee continues to keep a check on these threats, and they are also continuously analyzing the potential of the malware.
Apart from this, they are working with the app stores so that they can remove it later. Not only this the researchers also recommended the users to must keep a check on such anonymous apps so that they can protect themselves.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity, and hacking news updates.







