

Juniper Threat Labs researchers observed active attacks on Oracle WebLogic software using CVE-2020-14882. This vulnerability, if successfully exploited, allows unauthenticated remote code execution.
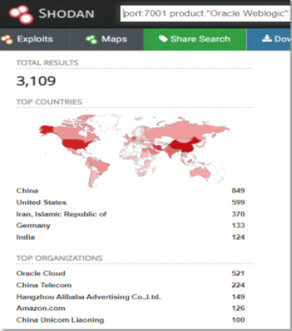
Researchers found almost 3,109 open Oracle WebLogic servers using Shodan. As a minimum of five different variants of attacks/payload. One particular payload installs a bot called DarkIRC.
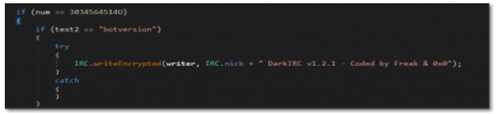
This bot performs a unique command and control domain generation algorithm that relies on the sent value of a particular crypto wallet. This bot is currently being sold on hack forums for $75USD.
DarkIRC
The attack issues an HTTP GET request to a vulnerable WebLogic server, which will execute a Powershell script to download and execute a binary file hosted in cnc[.]c25e6559668942[.]xyz
The source IP is 83.97.20.90. This IP resolves to the C&C of this bot which implies the attacker IP is similar to the C&C.
The Crypter
DarkIRC authors used a crypter to avoid detection, it includes anti-analysis and anti-sandbox features. The malware also tries to detect if it is running in virtualized environments like VMware, VirtualBox, VBox, QEMU, or Xen virtual machine.
If it is not detected, it will load an encrypted file in its resource. After unpacking, we can see what this malware wants to do, based on the name of its functions.
Bot Functions
The bot installs itself in the %APPDATA%\Chrome\Chrome.exe and creates an autorun entry. Its functions are:
- Browser Stealer
- Keylogging
- Bitcoin Clipper
- DDoS
- Slowloris
- RUDY (R-U-DeadYet?)
- TCP Flood
- HTTP Flood
- UDP Flood
- Syn Flood
- Worm or spread itself in the network
- Download Files
- Execute Commands
The malware implements a Bitcoin clipper feature to hijack bitcoin transactions on the infected system by changing the copied bitcoin wallet address to the malware operator’s bitcoin wallet address. It connects to its Command and Control via IRC with an added encryption XOR encryption.
The Command and Control DGA generate a domain, based on the value of a particular dogecoin wallet. It hashes the sent value of the wallet and gets the first 14 characters of the hash to complete the C&C domain.
An account in Hack Forums
Searching for the operators behind this threat, the researchers found an account in Hack Forums that goes online with the name of “Freak_OG” that is advertising the botnet since August 2020.

Conclusion
One of the fastest ways to victimize the attackers is to employ a zero-day exploit and attack the internet, usually through a spray-and-pray technique.
This vulnerability was fixed by Oracle in October and a subsequent out of cycle patch was also released in November to fix a hole in the previous patch. It is recommended to patch the affected systems immediately.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.
Also Read
Hackers Attacking WebLogic Servers via CVE-2020–14882 Flaw to install Cobalt Strike Malware
Oracle Issues Emergency Patch for Remote Code Execution Vulnerability in Oracle WebLogic Server
Oracle Warns Active Exploitation of Recently Patched WebLogic RCE Flaw







