
Attackers are increasingly targeting Docker and Kubernetes environments by exploiting misconfigurations, weak isolation boundaries, and insecure APIs to compromise host systems and entire clusters.
As containerization becomes the backbone of modern cloud infrastructure, threat actors are shifting focus from traditional endpoints to container ecosystems, where a single weakness can expose critical services at scale.
A recent campaign linked to the APT group TeamPCP highlights the growing sophistication of these attacks. The group poisoned a Docker Hub repository used by Checkmarx KICS, embedding a stealer that activated during security scans.
This supply chain compromise enabled attackers to extract Kubernetes secrets and sensitive credentials, demonstrating how trusted tools can be weaponized to infiltrate enterprise environments.
Containers rely on shared host kernels and Linux features such as namespaces and cgroups for isolation. However, this architecture introduces risk: once a container is compromised, attackers may exploit kernel flaws or runtime vulnerabilities to escape isolation and gain control of the host system.
Notable vulnerabilities continue to play a role in real-world attacks. CVE-2019-5736 in runC allowed attackers with container access to overwrite the runtime binary and execute code on the host.
According to Securelist, CVE-2022-0492 enabled container escape via improper cgroup handling, while CVE-2024-21626 exposed host file systems due to flawed file descriptor management. These flaws illustrate how container security is tightly coupled with the underlying operating system.
Even without exploiting vulnerabilities, attackers often succeed by abusing excessive permissions. Containers running in privileged mode or with dangerous Linux capabilities such as CAP_SYS_ADMIN can effectively bypass isolation.
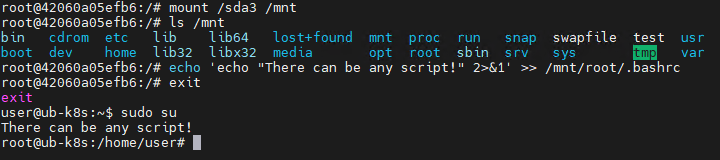
In one common scenario, an attacker mounts the host file system inside a compromised container and modifies critical files, achieving persistence and full system control.
Attackers Exploit Docker, Kubernetes
Misconfigured APIs remain one of the easiest entry points into container environments. Exposing Docker or Kubernetes APIs without proper authentication allows attackers to deploy malicious containers, execute commands, and access sensitive data remotely.
The primary risk of CAP_SYS_PTRACE is that it allows a process to read and modify the memory of other processes, control their execution, inject code, and extract sensitive data directly from memory.
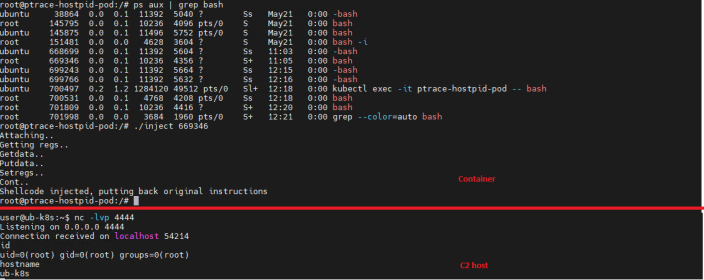
For example, an attacker with access to a Kubernetes API token can enumerate permissions and deploy a privileged pod designed for container escape.
With a simple API request, they can launch a container that mounts host resources, leading to full node compromise. Similarly, mounting the Docker socket inside a container grants attackers control over the entire host, effectively turning one compromised container into a cluster-wide breach.
Supply chain attacks further amplify the threat. Malicious images hosted on public repositories often disguise themselves as legitimate tools. Once deployed, these images can steal credentials, implant backdoors, or establish persistent access.
CI/CD pipelines are also prime targets, as attackers can inject malicious code during the build process without altering application logic, making detection significantly harder.
Modern container attacks are rarely isolated incidents. Instead, they follow multi-stage chains that combine initial access, credential harvesting, lateral movement, and eventual host or cluster takeover.
A compromised container may already contain API keys, service tokens, or environment secrets, providing attackers with immediate opportunities to expand their reach.
In many cases, attackers do not need to escape the container at all. Access to sensitive data within the container or connected services can be sufficient to compromise cloud infrastructure, impersonate services, or exfiltrate valuable information.
As organizations continue to adopt container-first architectures, the attack surface grows alongside them. Misconfigurations, overprivileged containers, and weak API security remain the most common and most exploited entry points.
Defending against these threats requires a comprehensive approach that includes strict access controls, runtime monitoring, secure image pipelines, and continuous configuration auditing across Docker and Kubernetes environments.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.


