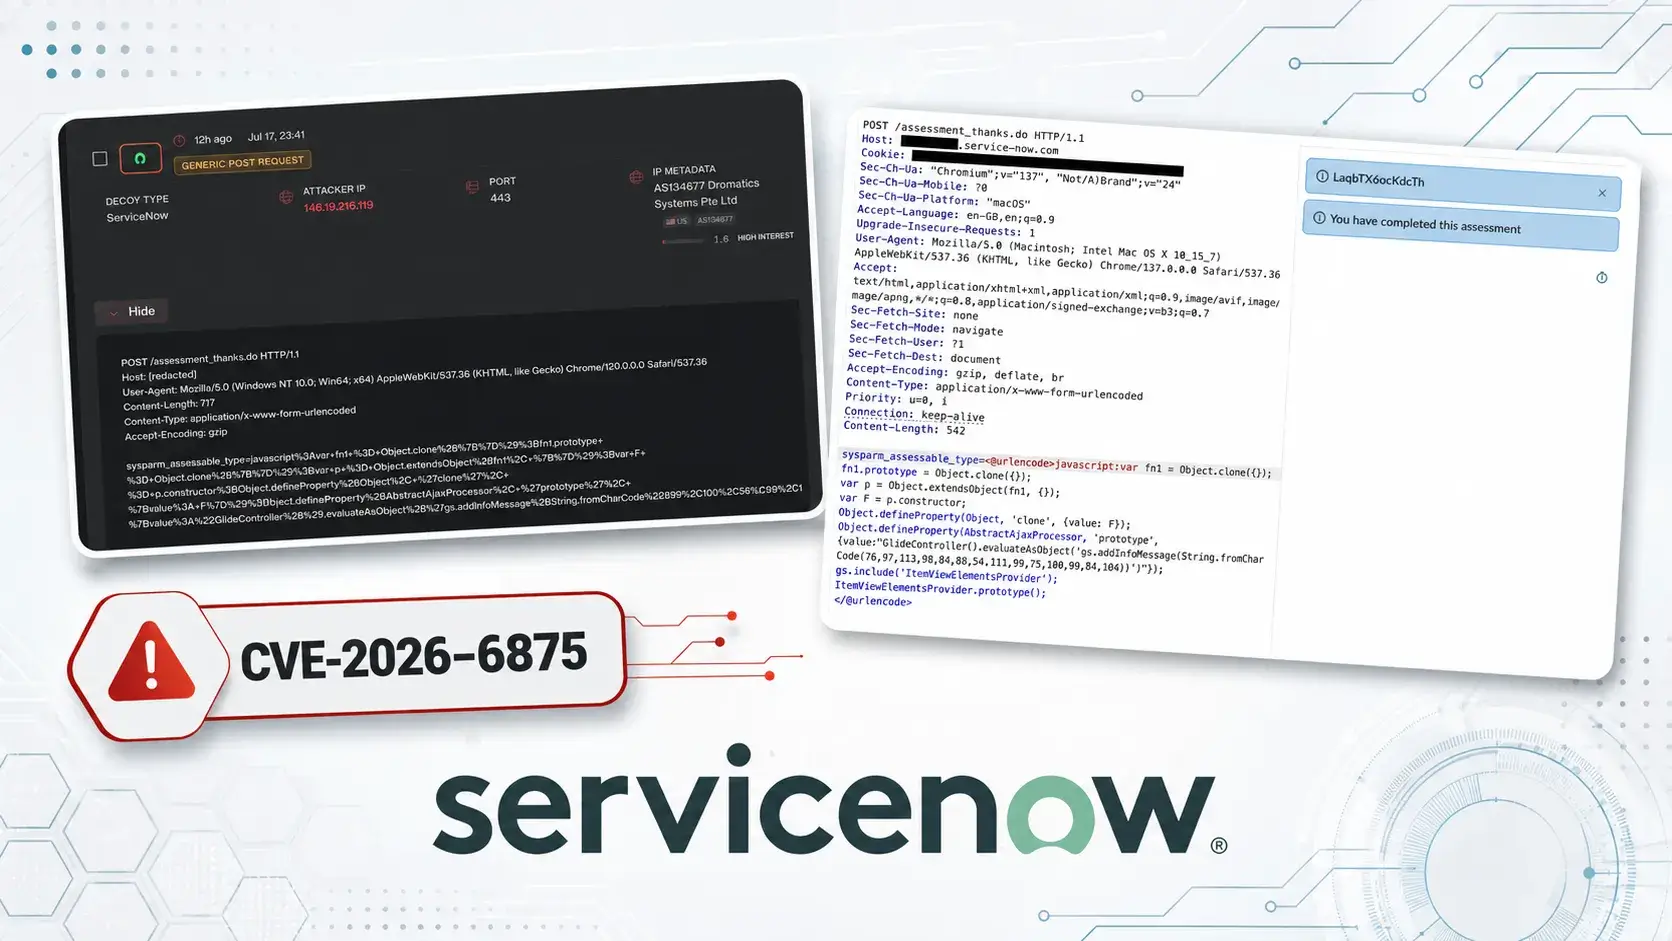

Threat actors are actively exploiting CVE-2026-6875, a critical pre-authentication remote code execution vulnerability in the ServiceNow AI Platform.
This vulnerability allows attackers to escape a restricted server-side script sandbox and execute code without valid credentials.
Reports from Defused indicate observed exploitation activity targeting this flaw. Initially, ServiceNow’s advisory stated it was not aware of any exploitation against customer instances.
Hackers Exploit ServiceNow AI Platform Flaw
The vulnerability, disclosed by Searchlight Cyber researchers, affects how ServiceNow handles JavaScript supplied through certain unauthenticated request parameters.
Attackers can reach the vulnerable flow through the /assessment_thanks.do endpoint, where the attacker-controlled `sysparm_assessable_type` input is passed to the GlideRecord query API. ServiceNow’s query handling supports `javascript:` expressions in filter contexts, creating a pre-authentication script execution vector when malicious input is accepted by the affected code path.
Although ServiceNow executes such expressions in an additional restricted script sandbox, researchers found ways to bypass these controls. The sandbox blocks high-risk capabilities, such as the direct use of `eval`, function declarations, and several dangerous Java classes. However, it still allows the `gs.include()` mechanism, which is used to load ServiceNow Script Includes.
Searchlight Cyber’s research revealed that Script Includes are evaluated in a different context that does not retain the same sandbox restrictions.
By manipulating globally accessible JavaScript objects and invoking a suitable Script Include gadget, an attacker can cause an attacker-controlled string to be processed through the JavaScript `Function` constructor during the include process. This creates an escape from the low-trust sandbox and enables execution in a more privileged ServiceNow scripting context.
Defused noted that the malicious payloads observed in the wild reach the same /assessment_thanks.do pre-authentication sink documented by Searchlight Cyber.
However, they indicated that the exploit chain utilizes a different sandbox-escape gadget than the published proof of concept, suggesting that attackers have adapted their technique rather than simply replaying public research.

Successful exploitation can allow an unauthenticated remote attacker to execute code within the ServiceNow platform. Searchlight Cyber warns that this level of access could enable attackers to access platform data, create administrative users, and execute commands through configured MID Servers or proxy infrastructure connected to internal enterprise environments.
The risk is particularly significant, as ServiceNow instances often contain IT service management records, workflow logic, authentication integrations, incident tickets, asset details, and credentials used by enterprise automation processes. An exposed and unpatched instance could thus become an entry point for data theft, privilege escalation, and lateral movement.
ServiceNow has released security updates for self-hosted customers and deployed mitigations to hosted instances. The vendor recommends that customers promptly apply the relevant patch or upgrade to a fixed family release. Hosted customers should verify that their environments have received the security update.
Security teams should immediately investigate requests to /assessment_thanks.do, particularly those containing suspicious `sysparm_assessable_type` values or `javascript:`-style expressions. Organizations should also review for unexpected administrator creation, unusual Script Include activity, anomalous workflow changes, suspicious MID Server command activity, and unexplained access to sensitive ServiceNow tables.
Additionally, ServiceNow is introducing Guarded Script controls designed to sharply restrict the code permitted in sandbox contexts, reducing the likelihood that similar pre-authentication sandbox escapes can be exploited in the future.
Strengthen Your SOC by Accelerating Threat Detection & Rapid Investigations. -> Integrate ANY.RUN With Your SOC Now.







