Sunday, October 18, 2026

Iranian Based OilRig APT Hackers Owned Email Hacking Tool Leaked in Telegram

OilRig APT hackers group owned Email Hacking Tool leaked by another group of hackers named “Lab Dookhtegan” in Telegram.

This tool named as Jason, which is one among the hacking tools listed in the Iranian Ministry of Intelligence arsenal.

This group also has known as APT 34, a team of highly intelligent hackers and malware developers to be originated from the Ministry of Intelligence of Iran that appears to target financial, energy, telecommunications, and chemical companies around the world.

Another group of hackers who was continuously leaking various hacking tools in their Telegram channel against APT 34 Iranian state sponsor group since March 26.

Email Hacking Tool

The same group already leaked many hacking arsenals in Telegram which includes malware source code, PowerShell Payload, a server-side module which is the c2 made in node.js, ASP Webshell, dubbed “HighShell” that has more than 30k lines of code.

Email Hacking Tool Used for Bruteforce Attack

Leaked Email hacking tool seems to be used for launching a Bruteforce attack against the target then trying to execute the various login passwords until it finds the original password.

Email Hacking Tool

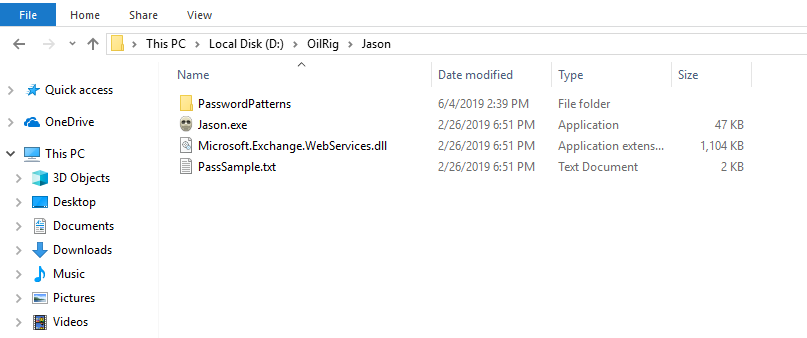
The Email Hacking Tool uploaded as an archived file with the name “Jason.zip,” Once I extracted the file, it compiled with four files, one indicates that the tool used to perform a brute-force attack against Microsoft exchange server.
According to Omri Segev, The tool has been uploaded to Virustotal quickly after it’s released in the telegram channel and has 0 detection rate at the time although compiled in 2015.

The unknown individual from Lab Dookhtegan Telegram channel wrote upon the tool leaks said “We are exposing today another cyber tool (Jason, an Email Hacking tool) being abused by the b**tard Iranian Ministry of Intelligence for hacking emails and stealing information. We thank our suffering compatriots for their cooperation with no hesitation.”

You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity updates also you can take the Best Cybersecurity courses online to keep yourself updated.

Balaji
Balaji
BALAJI is an Ex-Security Researcher (Threat Research Labs) at Comodo Cybersecurity. Editor-in-Chief & Co-Founder - Cyber Security News & GBHackers On Security.

Hot this week

How To Access Dark Web Anonymously and know its Secretive and Mysterious Activities

What is Deep Web The deep web, invisible web, or...

How to Build and Run a Security Operations Center (SOC Guide) – 2023

Today’s Cyber security operations center (CSOC) should have everything...

Russian Hackers Bypass EDR to Deliver a Weaponized TeamViewer Component

TeamViewer's popularity and remote access capabilities make it an...

Web Server Penetration Testing Checklist – 2026

Web server pentesting is performed under three significant categories: identity,...

ATM Penetration Testing – Advanced Testing Methods to Find The Vulnerabilities

ATM Penetration testing, Hackers have found different approaches to...

Hackers Use ConnectWise SkyKick Credentials to Access Microsoft 365, Halting Cloud Backups

Attackers abused compromised ConnectWise Cloud Backup credentials to access...

Anthropic’s Claude AI Uncovers Origins of NSA-Provided Cryptographic Keys After 25 Years

Anthropic says an internal Claude research model reconstructed how...

OpenBSD Kernel Flaw Dating Back 37 Years Enables Local Privilege Escalation to Root

A newly disclosed OpenBSD kernel exploitation chain combines a...

GhostAction Hackers Hide Credential-Stealing Malware in Fake Font Files Across 94 GitHub Repositories

GhostAction attackers have expanded their GitHub credential theft campaign...

SideCopy Hackers Target Indian Organizations With ReverseRAT Malware to Steal Data

Indian authorities have warned that SideCopy hackers are targeting...

New GhostBat Android Malware Targets 60 Banking and UPI Apps to Steal PINs

A new GhostBat RAT variant targets 60 Android financial...

New ROMULUS Malware Platform Uses Six Servers to Deliver Multiple Malicious Payloads

ROMULUS, a shared ClickFix delivery platform operating across six...

Related Articles

Recent News


