Sunday, October 18, 2026

Gustuff Android Banking Malware Uses SMS Messages to Hack Users Device

Gustuff banking malware returns with new features, the threat actors behind Gustuff malware made changes with distribution hosts and disabled C2 infrastructure. The malware uses SMS messages for propagation.

The Gustuff malware is a fully automated one, the malware is capable of stealing login credentials by abusing Accessibility Services in Android devices.

Researchers observed that the latest version of Gustuff uses a “poor man scripting engine” based on JavaScript language, which provides an ability to execute scripts while using its internal commands backed by the power of JavaScript language. This is very innovative in the Android malware space.”

Gustuff Malware Campaigns

Talos researchers first observed the new campaign around June 2019, the campaign uses Instagram to trick the users into downloading the malware. The malware campaign uses SMS messages as the primary method to infect users.

A new wave of the campaign observed starting this month, just like the June campaign. The malware primarily observed targets Australian banks and digital currency wallets. But the new campaign targets Australia based hiring sites’ mobile apps.

Gustuff banking malware
Campaign Hits Credits: Talos

As the campaign based only on SMS, the malware-hosting domains receive only a few hits.

“This method of propagation has a low footprint since it uses SMS alone, but it doesn’t seem to be particularly effective, given the low number of hits we’ve seen on the malware-hosting domains.”

Malware Activation Cycle

The malware attempts creating an uu.dd in the external storage, which has a UUID value and the value is used as ID for the C2 server. It pings with C2 at a predetermined interval and will get commands for execution.

It checks for the list of apps installed and blocks the list of anti-virus/anti-malware software present in the below list.
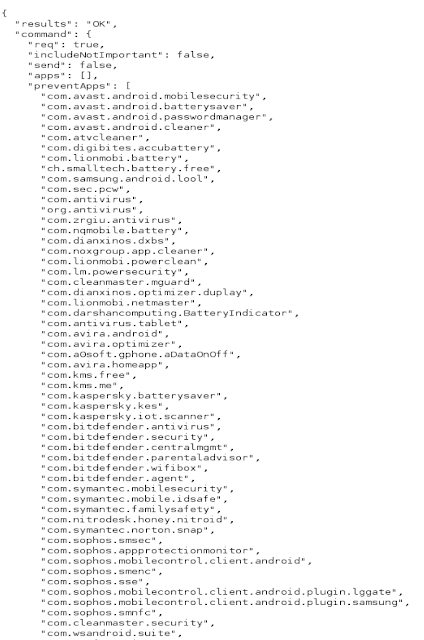
Gustuff banking malware
List of apps Blocked Credits: Talos

The malware sends commands requesting credit card information, but it won’t present a form to enter the details, instead, it leverages the Android Accessibility API to harvest it.

Request Credit Card Data

The malware was initially designed to target only as a banking trojan, later it’s capabilities are expanded to target crypto services, online stores, payment systems, and messengers.

You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.

Gurubaran
Gurubaran
Gurubaran is a co-founder of Cyber Security News and GBHackers On Security. He has 10+ years of experience as a Security Consultant, Editor, and Analyst in cybersecurity, technology, and communications.

Hot this week

How To Access Dark Web Anonymously and know its Secretive and Mysterious Activities

What is Deep Web The deep web, invisible web, or...

How to Build and Run a Security Operations Center (SOC Guide) – 2023

Today’s Cyber security operations center (CSOC) should have everything...

Russian Hackers Bypass EDR to Deliver a Weaponized TeamViewer Component

TeamViewer's popularity and remote access capabilities make it an...

Web Server Penetration Testing Checklist – 2026

Web server pentesting is performed under three significant categories: identity,...

ATM Penetration Testing – Advanced Testing Methods to Find The Vulnerabilities

ATM Penetration testing, Hackers have found different approaches to...

Hackers Use ConnectWise SkyKick Credentials to Access Microsoft 365, Halting Cloud Backups

Attackers abused compromised ConnectWise Cloud Backup credentials to access...

Anthropic’s Claude AI Uncovers Origins of NSA-Provided Cryptographic Keys After 25 Years

Anthropic says an internal Claude research model reconstructed how...

OpenBSD Kernel Flaw Dating Back 37 Years Enables Local Privilege Escalation to Root

A newly disclosed OpenBSD kernel exploitation chain combines a...

GhostAction Hackers Hide Credential-Stealing Malware in Fake Font Files Across 94 GitHub Repositories

GhostAction attackers have expanded their GitHub credential theft campaign...

SideCopy Hackers Target Indian Organizations With ReverseRAT Malware to Steal Data

Indian authorities have warned that SideCopy hackers are targeting...

New GhostBat Android Malware Targets 60 Banking and UPI Apps to Steal PINs

A new GhostBat RAT variant targets 60 Android financial...

New ROMULUS Malware Platform Uses Six Servers to Deliver Multiple Malicious Payloads

ROMULUS, a shared ClickFix delivery platform operating across six...

Related Articles

Recent News


