Sunday, October 18, 2026

CallerSpy Android Malware Advertised as Chat App Steals Call Logs, SMS, Contacts & Files on the Infected Device

Researchers observed a new malware family in May involved in various cyberespionage campaigns advertised as a chat app dubbed “Chatrious” downloaded from the malicious website by clicking the download button on the site.

The campaign back in action again with a different app called “Apex App”, that steals the user’s infection on the affected device. Trend Micro detected the threat as AndroidOS_CallerSpy.HRX.
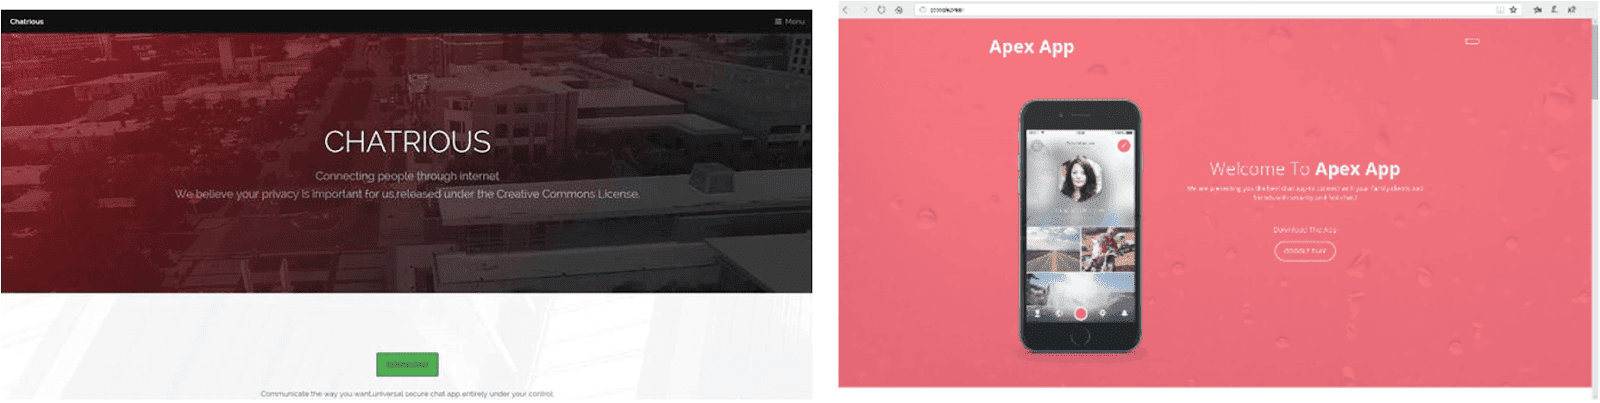
CallerSpy
Two malicious apps

CallerSpy Malware Distribution

CallerSpy distributed as a chat app when the app launched in the victim device connects with the C&C server via Socket.IO and to monitor commands from the C&C server. Also, it schedules new tasks by using Evernote for stealing information.
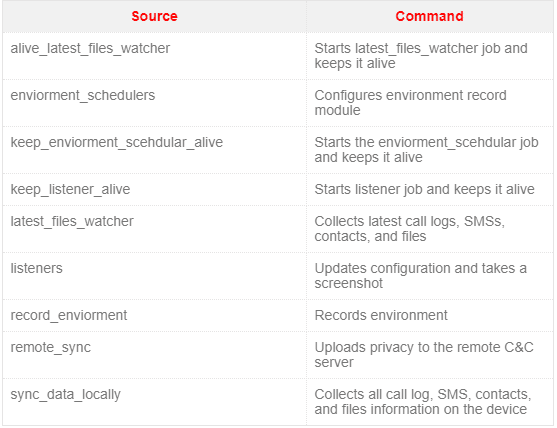
CallerSpy commands
malware functions

The malware is capable of stealing various information such as call logs, SMSs, contacts, and files on the device. It also takes screenshots of the infected device and later sends it to the C&C server.

According to Trend Micro research “The malware creates a local storage on the infected device and they will be uploaded to the C&C server periodically, it looks for the following file formats in the infected device that includes jpg, jpeg, png, docx, xls, xlsx, ppt, pptx, pdf, doc, txt, csv, aac, amr, m4a, opus, wav, and amr.”

All the collected data encoded as Base64 and the data uploaded to the C&C server. To trick the users the threat actors used typo squatted domain gooogle[.]press.

Researchers able to find four C&C IP addresses hosted on the legitimate service and they are connected with port 3000. The malicious app doesn’t provide any user interface (UI) and it uses only the default android app icon labeled as the rat.
Available forms

The download section of the malicious page provides options to download the app indicating Apple, Android and Windows platforms. But now the app supports only for the Android device.

The good news is that the app is not available to download from the play store and the victims of the malware are still unclear.

Also Read: StrandHogg – Hackers Aggressively Exploiting New Unpatched Android OS Vulnerability in Wide Using Malware

Gurubaran
Gurubaran
Gurubaran is a co-founder of Cyber Security News and GBHackers On Security. He has 10+ years of experience as a Security Consultant, Editor, and Analyst in cybersecurity, technology, and communications.

Hot this week

How To Access Dark Web Anonymously and know its Secretive and Mysterious Activities

What is Deep Web The deep web, invisible web, or...

How to Build and Run a Security Operations Center (SOC Guide) – 2023

Today’s Cyber security operations center (CSOC) should have everything...

Russian Hackers Bypass EDR to Deliver a Weaponized TeamViewer Component

TeamViewer's popularity and remote access capabilities make it an...

Web Server Penetration Testing Checklist – 2026

Web server pentesting is performed under three significant categories: identity,...

ATM Penetration Testing – Advanced Testing Methods to Find The Vulnerabilities

ATM Penetration testing, Hackers have found different approaches to...

Hackers Use ConnectWise SkyKick Credentials to Access Microsoft 365, Halting Cloud Backups

Attackers abused compromised ConnectWise Cloud Backup credentials to access...

Anthropic’s Claude AI Uncovers Origins of NSA-Provided Cryptographic Keys After 25 Years

Anthropic says an internal Claude research model reconstructed how...

OpenBSD Kernel Flaw Dating Back 37 Years Enables Local Privilege Escalation to Root

A newly disclosed OpenBSD kernel exploitation chain combines a...

GhostAction Hackers Hide Credential-Stealing Malware in Fake Font Files Across 94 GitHub Repositories

GhostAction attackers have expanded their GitHub credential theft campaign...

SideCopy Hackers Target Indian Organizations With ReverseRAT Malware to Steal Data

Indian authorities have warned that SideCopy hackers are targeting...

New GhostBat Android Malware Targets 60 Banking and UPI Apps to Steal PINs

A new GhostBat RAT variant targets 60 Android financial...

New ROMULUS Malware Platform Uses Six Servers to Deliver Multiple Malicious Payloads

ROMULUS, a shared ClickFix delivery platform operating across six...

Related Articles

Recent News


