

Critical security vulnerabilities discovered with the F5 BIG-IP application delivery controller (ADC) let remote attackers to run commands and to compromise the system.
The BIG-IP application delivery controller (ADC) use to handle application traffic and secure your infrastructure.
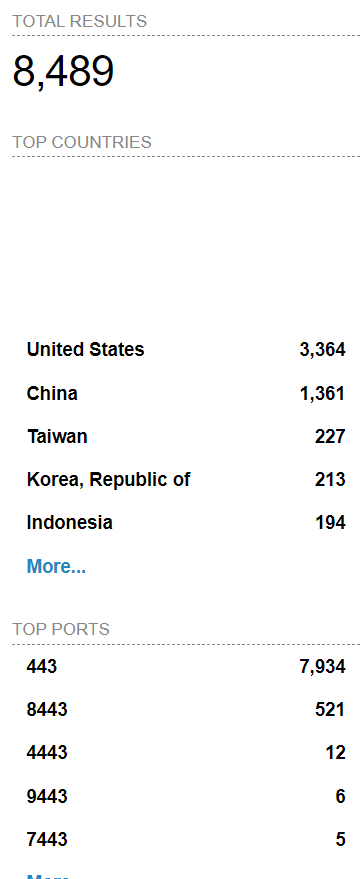
Based on Shodan search more than 8,000 vulnerable devices available from the internet in the world, more than 40% from the united states, 16% in China, 3% in Taiwan, and 2.5% in Canada and Indonesia.
F5 BIG-IP Vulnerability
The vulnerability with the BIG-IP application delivery controller (ADC) was found by Positive Technologies researchers.
It allows a remote attacker to completely compromise the system and to intercept controller application traffic.
CVE-2020-5902 (CVSS score of 10)
This vulnerability poses the highest risk, it can be exploited by an attacker by sending a specifically crafted HTTP request to the server hosting the traffic management control utility (TMUI) for BIG-IP configuration.
“By exploiting this vulnerability, a remote attacker with access to the BIG-IP configuration utility could, without authorization, perform remote code execution (RCE1). The attacker can create or delete files, disable services, intercept information, run arbitrary system commands and Java code, completely compromise the system, and pursue further targets, such as the internal network,” said Researcher Mikhail Klyuchnikov.
CVE-2020-5903 (CVSS score of 7.5)
F5 also fixed XSS vulnerability that allows attackers to run running malicious JavaScript code as the logged-in user.
If the compromised user is an administrator then it leads to a full compromise of BIG-IP via RCE.
The vulnerabilities may result in full system compromise, it affects the following versions (11.6.x, 12.1.x, 13.1.x, 14.1.x, 15.0.x, 15.1.x), if you are running a vulnerable versions users are recommended to update with (11.6.5.2, 12.1.5.2, 13.1.3.4, 14.1.2.6, 15.1.0.4).
Rich Warren, a security researcher for the NCC Group spotted that hackers started exploiting the flaw to steal administrator passwords.
Considering the seriousness of vulnerability US Cyber Command urges F5 customers to patch CVE-2020-5902 and CVE-2020-5903 immediately.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.
Also Read







 let remote attackers to run commands.)