

Ryuk ransomware is known for targeting know for targeting various large organizations worldwide. It is often distributed by other malware such as Emotet or TrickBot.
Ryuk Ransomware initially uncovered in August 2018 since then it infects and compromise various organization and steals millions of dollars from affected victims.
The analysis shows that Ryuk is a result of the custom development of an older commodity malware known as Hermes, believed to have been authored by North Korea’s Stardust Chollima (a.k.a. APT38, believed to be a revenue-generating offshoot of the well-known APT Lazarus Group).
Ryuk With Zerologon
Zerologon is a dangerous vulnerability tracked as CVE-2020-1472, it is due to a flaw in the login process that let attacker establishes a vulnerable Netlogon secure channel connection to a domain controller, using the Netlogon Remote Protocol (MS-NRPC).
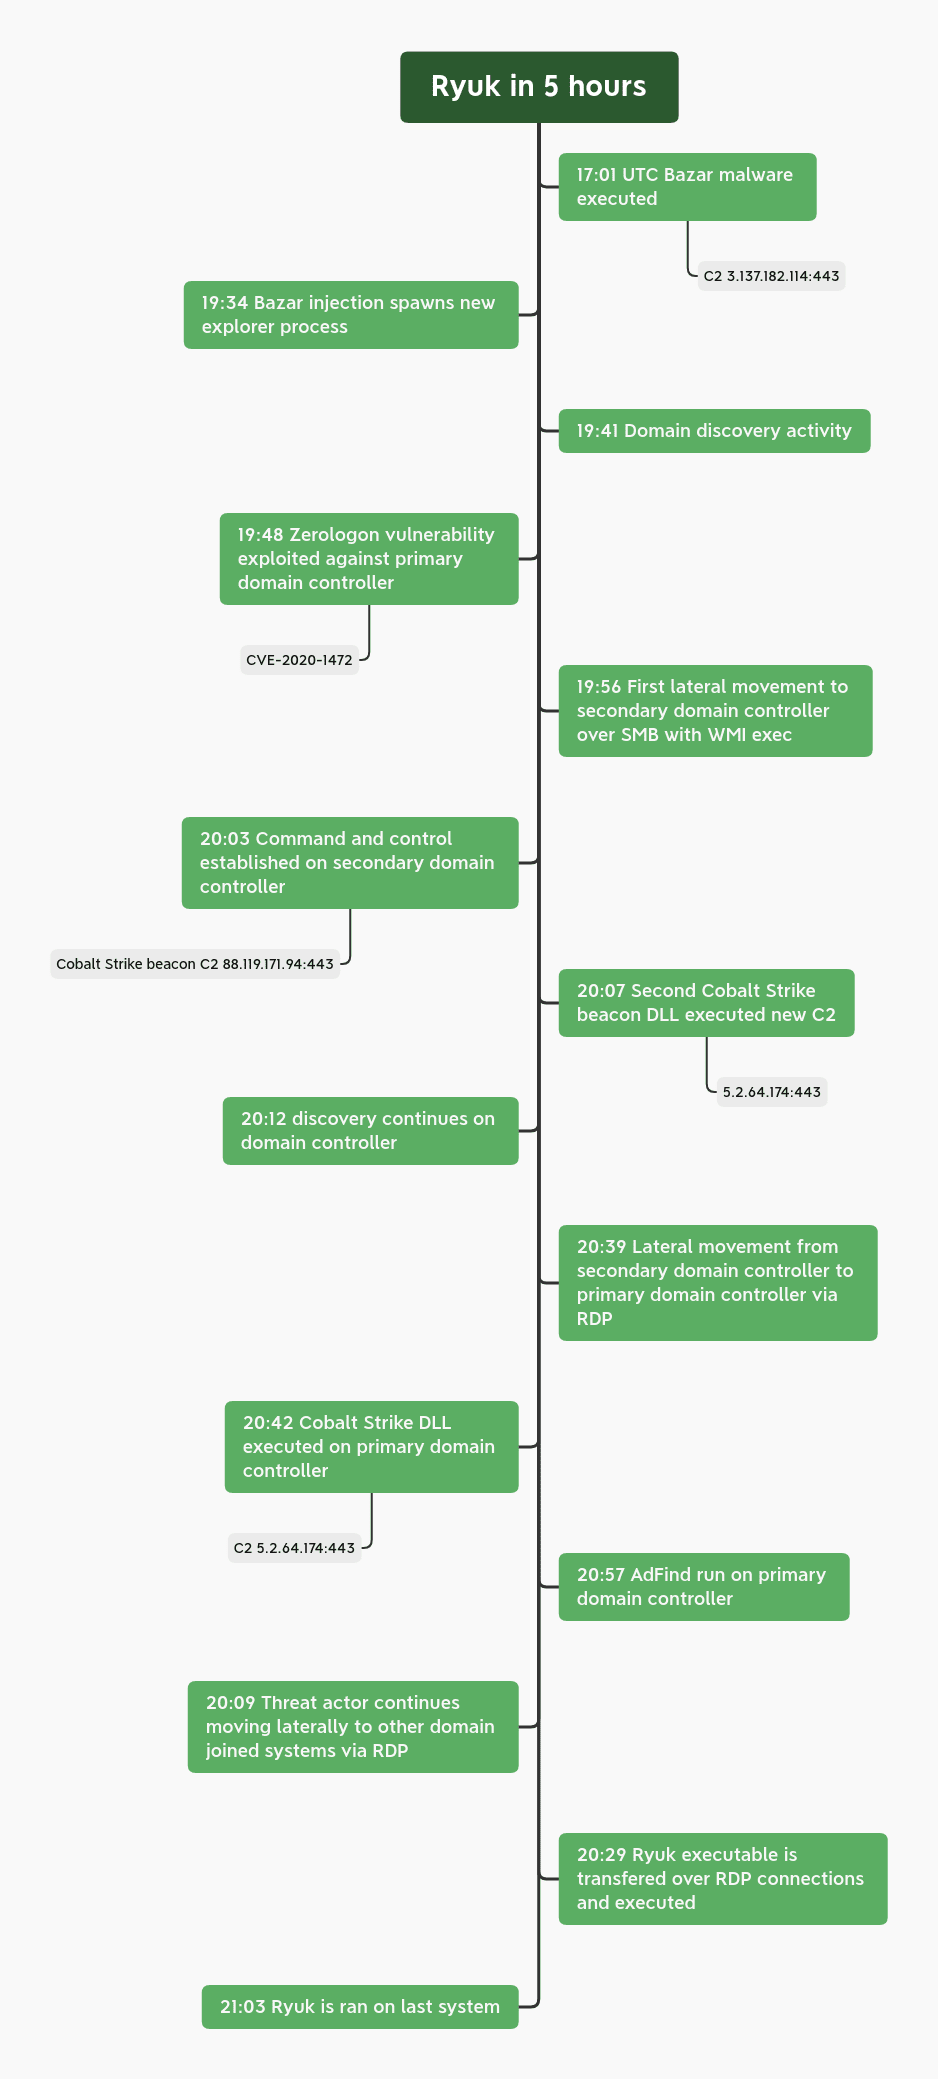
Ryuk threat actors use Zerologon (CVE-2020-1472) vulnerability to complete the ransomware to domain-wide in about 5 hours.
“We saw the threat actors leverage access to an environment via the Bazar Loader malware. This time around, we saw them accomplish their objective faster, but the general tactics and techniques stayed similar between incidents,” reads the DFIR report.
In this case, Ryuk dropped by the sophisticated Bazar Loader malware which is a part of the TrickBot group’s and it primarily focuses on high-value targets.
The attackers started as a low-level user and exploit the recently disclosed Zerologon vulnerability (CVE-2020-1472) to gain access to the primary domain controller.
Lateral movements handled via SMB file transfers and WMI executions, once they moved with secondary domain controller threat actors run more domain discovery via Net and the PowerShell Active Directory module.
In about five hours attackers completed their objective by executing the ransomware on the primary domain controller.
Here you can find the complete timeline
The first thing you should do is work with your IT department to ensure the patch from Microsoft is implemented on your network immediately if it hasn’t been done so already.
August’s patch from Microsoft added five Event IDs for vulnerable Netlogon connections. When a secure channel connection during the initial deployment phase is allowed, event ID 5829 is generated.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.
Also Read:
Cookiethief – Android Malware that Gains Root Access to Steal Browser & Facebook App Cookies
Google Play Store Flooding with Spyware, Banking Trojan, Adware Via Games, and Utility Apps







