

The cybersecurity research team at FireEye has recently warned that they have detected two groups of hackers. And the analysts intended that one of the hacking groups is being linked to China.
The hacking group has exploited many popular enterprise software in this recent months. However, the cybersecurity experts claim that the VPN programs are part of the daily life of many home users, and not only this but it is also an important part of the organizations or companies as well.
The security researchers affirmed that the threat actors are exploiting a mixture of known zero-day vulnerabilities, and a new one, in Pulse Secure’s virtual private network (VPN) software.
Chinese State-Sponsored Hackers likely Behind Attacks
The cybersecurity analysts have stated that the CVE-2021-22893 was exploited in combination along with some other Pulse Secure bugs. This zero-day ruling enables it to be exploited and influence very diverse organizations, as well as government institutions.
Moreover, the analysts of FireEye concluded that there were at least two threat actors which were racked as UNC2630 and UNC2717.
Not only this they have also detected that the threat actors of UNC2630 have already shaken hands with APT5. We all know that the APT group generally operates operations for the Chinese government.
List of Malware Families
After a proper investigation, FireEye experts have mentioned a full list of malware families, and that’s why here we have mentioned them below:-
UNC2630
- SLOWPULSE
- RADIALPULSE
- THINBLOOD
- ATRIUM
- PACEMAKER
- SLIGHTPULSE
- PULSECHECK
UNC2717
- HARDPULSE
- QUIETPULSE
- PULSEJUMP
SLOWPULSE variants
SLOWPULSE was a novel malware family that was found while investigating UNC2630. The researchers came to know that this malware along with its variants is implemented as modifications to the legitimate Pulse Secure files.
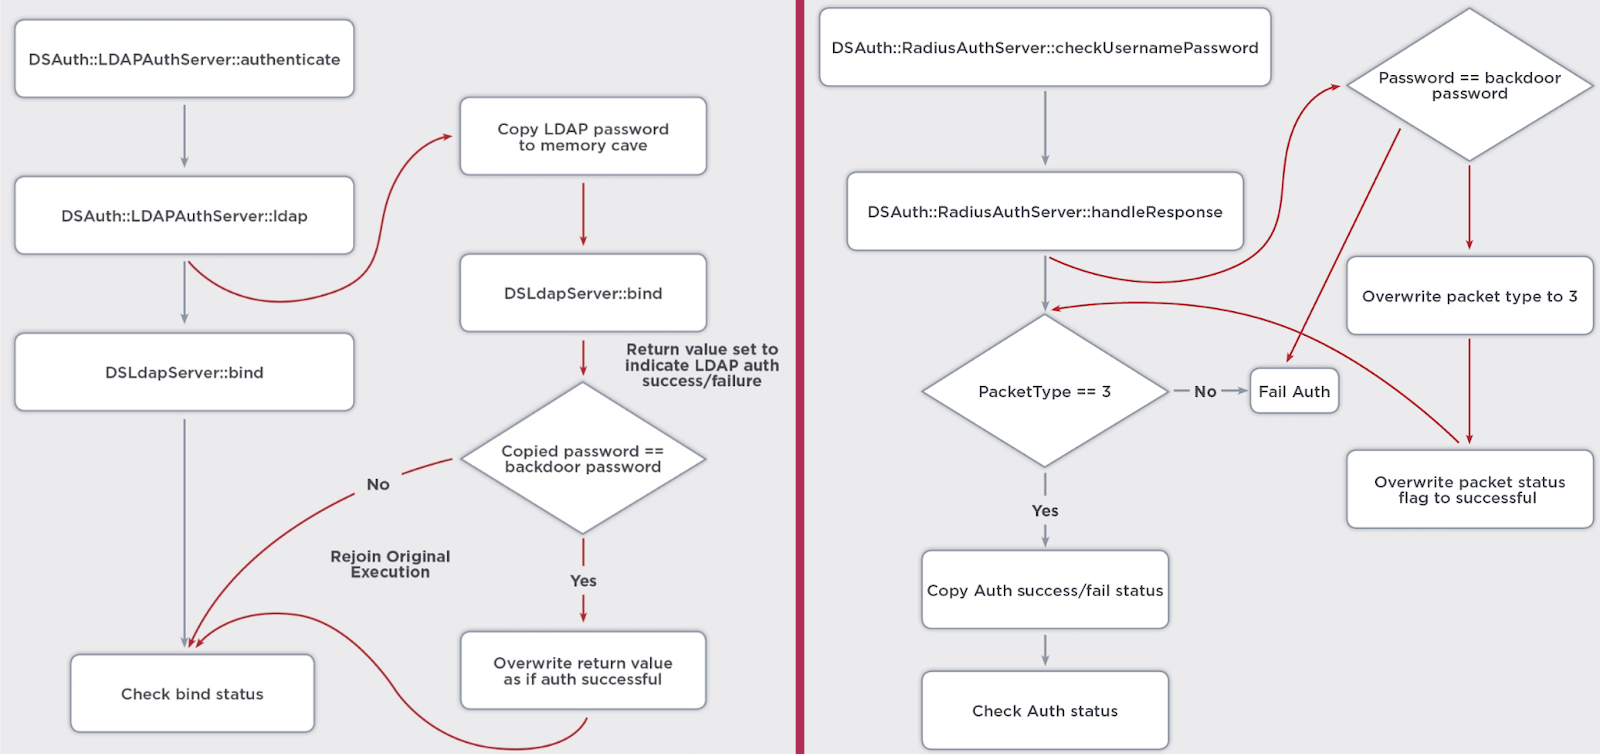
Once it’s done with modification, then it directly bypasses or logs the credentials in the authentication flow, and this malware has 4 variants.
- SLOWPULSE Variant 1 – This variant is qualified for avoiding LDAP and RADIUS-2FA authentication routines. Not only this but this variant inserts a check against the backdoor password, once it’s done with the insert, then its bind routine returns the value.
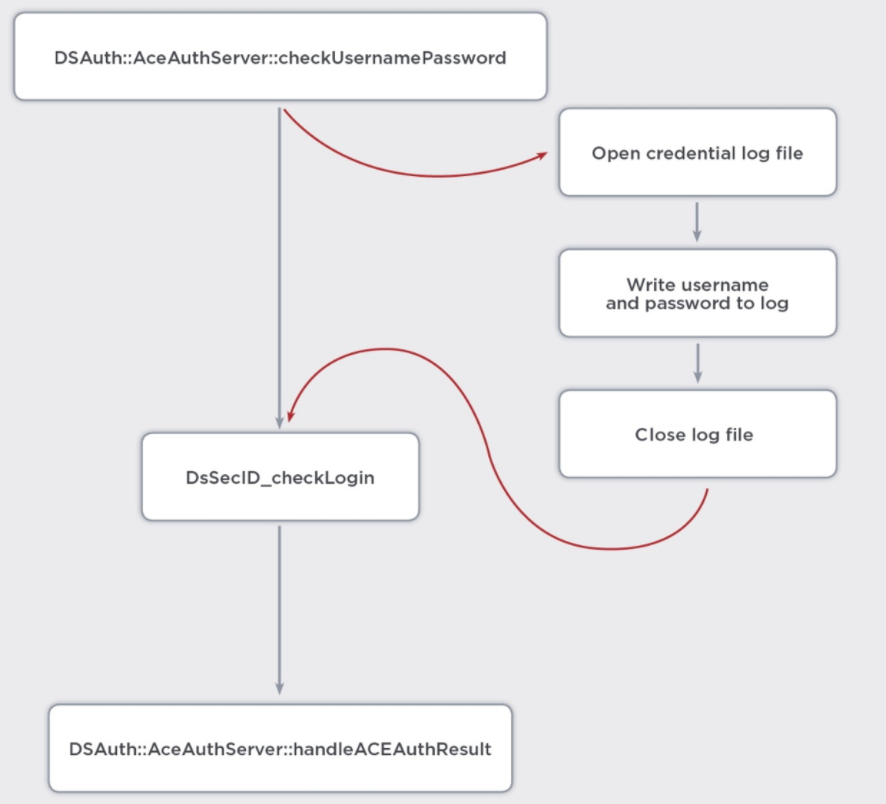
- SLOWPULSE Variant 2 – In this, the experts opined that it is responsible for using the ACE-2FA authentication procedure.
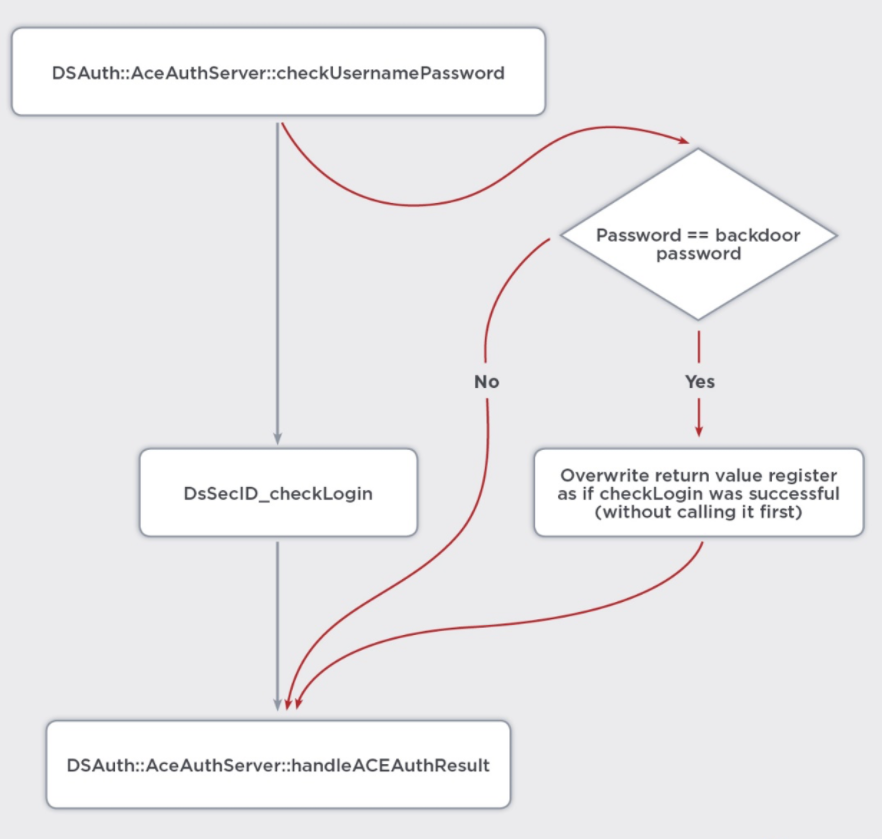
- SLOWPULSE Variant 3 – By using this variant, the threat actors can easily bypass the ACE-2FA logon procedure.
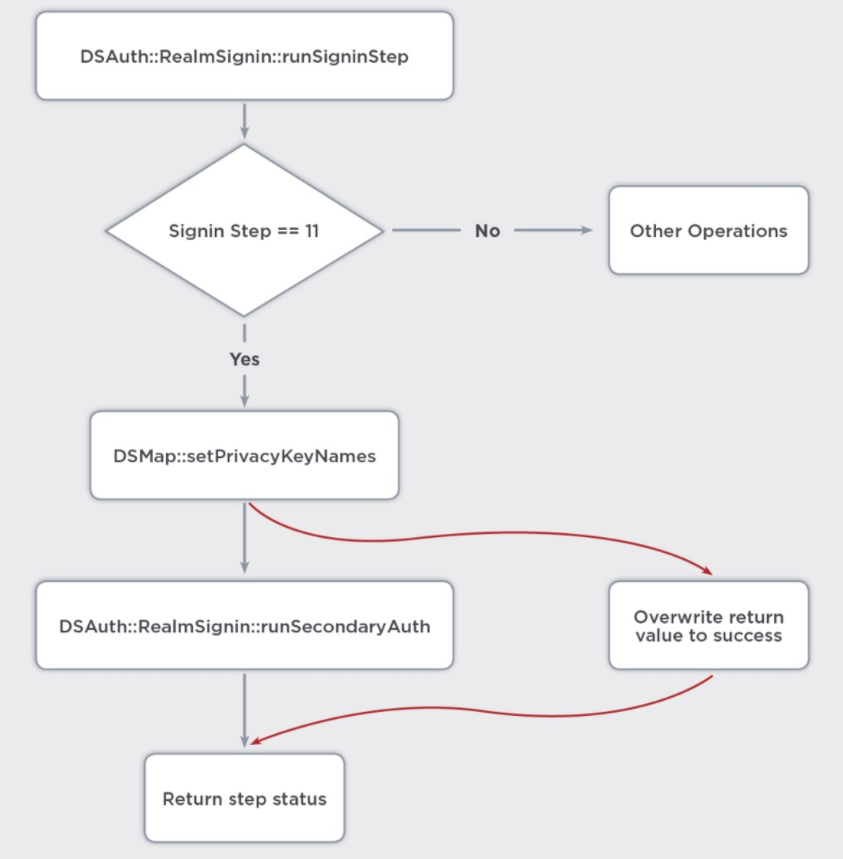
- SLOWPULSE Variant 4 – This variant allows the attackers to modify the execution flow of a particular step of the login method so that it can spoof successful authentication.
Recommendations
According to the cybersecurity experts, every organization should apply the most recent version of Pulse Secure’s Integrity Assurance utility that is released on March 31, 2021.
Moreover, organizations must always examine available forensic testimony to conclude if an attacker negotiated user credentials. Not only this the experts also recommended the organizations for resetting all passwords.
And always keep reviewing the configuration to assure that no service accounts can be utilized to authenticate the vulnerability.
However, the Pulse Secure VPN was one of the vulnerable applications that the threat actors hackers affiliated with China’s Ministry of State Security.
But, the hackers used it to infiltrate the US government, private networks, and financial organizations since last year, that’s why the researchers are trying their best to bypass such threat.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity, and hacking news updates.







